Online Services

Blog

  • This Week’s Top 20 Attacked Themes and Who is Attacking Them

    This Week’s Top 20 Attacked Themes and Who is Attacking Them

    Today we’re publishing statistics on the attacks we are seeing on themes across the WordPress ecosystem. The Wordfence Firewall provides us with attack telemetry across a large number of sites that we protect. The data we’re sharing today is based on the following high level metrics:

    • An analysis of 15,949,826 total attacks across the past 7 days – from Monday August 1st to Monday August 8th (yesterday) on sites that Wordfence protects.
    • Attacks on 519,592 unique Wordfence customer websites.
    • Attacks originating from a total of 72,896 unique IPs. 

    The “Theme Slug” below is a term used in WordPress parlance. It refers to the unique directory name that is created in the wp-content/themes/ directory for the theme when it is installed. This uniquely identifies themes in the WordPress ecosystem. To find out more about the theme, simply Google the ‘slug’.

    The table shows the total attacks we recorded on that theme across all sites, the number of IPs that launched an attack on the theme and the number of unique sites that we recorded attacks for that targeted that theme. To be clear, that is not the number of sites actually running the theme. It’s simply the number of sites where someone tried to attack the theme, whether it was installed or not.

    We explain why most of these themes are being attacked and what the “Bulk Disclosed” column means below the table.

    Theme Slug Total attacks Unique IPs attacking Unique sites attacked Vulnerability Type Bulk Disclosed
    churchope 172,782 2,055 63,115 LFI X
    mTheme-Unus 163,644 2,303 90,803  LFI
    lote27 135,948 1,922 60,638 LFI X
    SMWF 121,725 1,466 85,228 LFI X
    markant 118,962 1,399 83,418 LFI X
    felis 118,437 1,431 81,800 LFI X
    MichaelCanthony 114,503 1,389 79,059 LFI X
    TheLoft 113,990 1,387 78,644 LFI X
    parallelus-mingle 105,648 1,568 54,279  LFI
    urbancity 96,810 1,678 56,952 LFI X
    trinity 89,603 1,410 52,326 LFI X
    authentic 82,692 1,817 37,312 LFI X
    parallelus-salutation 73,025 1,628 35,886  LFI
    elegance 68,928 1,009 21,726  LFI
    awake 68,424 1,031 21,323  LFI
    antioch 63,174 1,365 26,243 LFI X
    modular 62,470 990 19,770 LFI
    epic 53,903 925 17,400 LFI X
    infocus 52,739 989 19,942  LFI
    Newspapertimes_1 50,707 943 29,297  LFI


    Who is attacking these themes?

    Back in December, 2014 a researcher bulk disclosed a large number of WordPress theme vulnerabilities. The disclosure includes a script that targets a single site and tries to exploit vulnerabilities in a large number of themes. The vulnerabilities it tries to exploit are all file inclusion vulnerabilities.

    In the comments at the top of the script that was disclosed, the researcher also includes an example of how to use the script with the powerful INURLBR scanner which he also wrote. This allows attackers and presumably other researchers to bulk find and exploit WordPress sites by trying to exploit the theme vulnerabilities disclosed.

    This is the example included in the disclosure:

    ./inurlbr.php --dork 'inurl:/wp-content/themes/' -q 1,6 -s save.txt 
    
       --comand-all "php exploit.php _TARGET_"

    In the statistics we’ve released above, all the themes marked with an X are included in the bulk disclosure that was made and which included the inurlbr exploit example. So we think what is happening is that so called “script kiddies” (unsophisticated hackers) are grabbing the researcher’s original example from December 2014 and trying to exploit old vulnerabilities in themes.
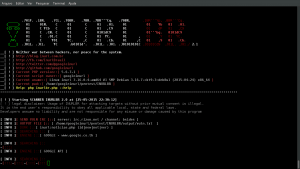
    All these exploits are being blocked by the Wordfence firewall. It’s also likely that many, possibly all of the themes have now fixed this vulnerability, although we recommend that if you use any of these themes you verify with your vendor that your current version contains no vulnerabilities.

    The INURLBR scanner has evolved since it was first released in July 2014 into a powerful tool that allows attackers to bulk locate and exploit WordPress websites and sites using other CMSs. The scanner includes:

    • Support for a huge range of search engines to “Google dork” and find targets for attack.
    • Bulk exploiting of targets once found.
    • The ability to use proxies to hide where queries and exploits are coming from.
    • The ability to rotate proxies to constantly change IP.
    • Ability to hide behind Tor.
    • It can send vulnerable sites to an IRC channel, presumably for botnet integration.
    • It includes many other features like regex matching/extraction and more.

    It’s possible that many users of INURLBR are using the original bulk disclosure to test INURLBR before launching more sophisticated attacks. That may explain why those original themes are dominating our top 20 list of exploited themes.

    At Wordfence we constantly mine attack data to discover how to better protect our customers. Upgrade to Wordfence Premium today to receive real-time firewall rule updates, premium support and much more.

    We encourage you to comment and share this data with the larger WordPress community.

    The post This Week’s Top 20 Attacked Themes and Who is Attacking Them appeared first on Wordfence.

  • Spotlight – How Cart66 Maintains Security for Ecommerce

    Spotlight – How Cart66 Maintains Security for Ecommerce

    Cart66 offers a comprehensive plugin solution for WordPress shop owners. With a unique suite of services, intuitive features, and essential security components, Cart66 provides everything you need to operate a PCI compliant online store. PCI compliance is one of the most important considerations for any ecommerce site. Cart66 connects your WordPress website to a hosted…

    The post Spotlight – How Cart66 Maintains Security for Ecommerce appeared first on Sucuri Blog.

  • A Plugin’s Expired Domain Poses a Security Threat to Websites

    A Plugin’s Expired Domain Poses a Security Threat to Websites

    Do you keep all of your website software (including third-party themes, plugins, and components) up to date? You should! We always recommend this to our clients and readers. Applying updates quickly will make sure that you replace any vulnerable code as soon as the security patch is released. However, this isn’t the only reason to…

    The post A Plugin’s Expired Domain Poses a Security Threat to Websites appeared first on Sucuri Blog.

  • Profile of a Russian Attack IP

    Profile of a Russian Attack IP

    At Wordfence we track attacks across all our customer sites, both free and paid to learn more about attacker tactics, techniques and procedures (TTP’s). Mining this data helps us improve Wordfence Firewall, Wordfence’s Scan and our other features and to do a better job of keeping you safe.

    We use a large distributed cluster to mine the huge amount of attack data we receive. Looking at the data for the past 7 days alone, we have logged 16.6 million attacks for just that period.

    Analyzing our data has been incredibly productive and in the coming weeks we will be sharing additional insights. For today’s post we want to share some detail on the IP address that is responsible for the most attacks on our WordPress customer sites during the past 7 days.

    The first part of this IP is: 46.161.X.X. We’re not sharing the full IP and in general we will mask the addresses of attacking IP’s in case those servers contain vulnerabilities. We don’t want to create new targets for attack. So for the sake of conversation, lets call this IP address Ivan.

    Ivan has been a very bad IP address. In the past 7 days he has launched 2,036,508 attacks on our customer sites which we’ve blocked.

    The next highest attacking IP address is responsible for 468,661 attacks, so this IP is head and shoulders the leading attack IP during the past week.

    In fact Ivan is responsible for over 12% of all the attacks on all WordPress sites that Wordfence protects. That’s quite an achievement.

    During the past 7 days the total number of IP addresses we have blocked attacks from is 77,939 unique IP’s. This gives you an idea of how many attackers there are out there. Ivan has quite a lot of competition and despite that, he managed to come out at number 1.

    During the past 7 days Ivan attacked 32,091 unique websites.

    97% of attacks from this IP address tried to download the wp-config.php file using a wide range of arbitrary file download vulnerabilities in both plugins and themes.

    The themes that were attacked by Ivan are shown in the following table. We also show the total attacks launched on each theme across all sites, along with the number of unique sites that were attacked by trying to exploit a vulnerability in the theme.

    All these attacks use known file download vulnerabilities except one which may be a zero day vulnerability, so we are redacting the name of that theme.

    Theme name Total attacks Unique sites attacked
    infocus 83095 20587
    acento 43898 20481
    XXXXX* 43613 20340
    jarida 43451 20292
    markant 43307 20259
    yakimabait 43291 20300
    tess 43015 20110
    felis 42854 20030
    ypo-theme 42671 19995
    persuasion 41527 20316
    echelon 41398 20264
    modular 41322 20263
    awake 41123 20145
    fusion 41012 20132
    method 40908 20101
    myriad 40702 20007
    elegance 40677 19976
    dejavu 40551 19997
    construct 40278 19882
    epic 37141 17850
    linenity 36656 17619
    parallelus-salutation 36586 17623
    trinity 36295 17503
    antioch 36180 17322
    urbancity 36118 17416
    parallelus-mingle 35740 17179
    authentic 35683 17073
    churchope 35532 17040
    lote 35445 17027


    The following table shows the plugins that are being attacked by Ivan. In all cases the attacker is using an arbitrary file download vulnerability in these plugins to try and download wp-config.php. All plugins have known arbitrary file download vulnerabilities except for one which may be a zero day and which we’ve redacted from this report.

    Plugin Name Total attacks Unique Sites Attacked
    filedownload 46037 21373
    ajax-store-locator-wordpress 44123 20558
    plugin-newsletter 38227 18351
    pica-photo-gallery 37795 18126
    simple-download-button-shortcode 37684 18066
    wp-filemanager 37457 17236
    tinymce-thumbnail-gallery 37270 17888
    dukapress 36697 17495
    XXXXXX* 36303 17358
    db-backup 34966 16627


    One of the things we examined when looking at data from this IP address is whether any cloud WAF providers are blocking these attacks. We were surprised to see 58,089 attacks from this IP in the past week bypassed Cloudflare (came in through their servers) and were not blocked. These attacks occurred on 1,183 unique websites. In each case the attack passed through a Cloudflare server and was blocked by Wordfence.

    The attacks exploit well known vulnerabilities. These customers may be running Cloudflare’s free package which includes “broad security protection” but does not include a WAF. In each case the request we received contained the HTTP header that verifies the source is the attacker we’re analyzing and it came via Cloudflare.

    Cf-Connecting-Ip: 46.161.X.X

    The attacking IP we’ve dubbed ‘Ivan’ is based in St. Petersburg, Russia. It is operated by “Petersburg Internet Network ltd.”. The IP runs Debian Linux and runs a range of services including an FTP daemon, web server (with placeholder page), mail services and SSH.

    What to do

    We are working to contact the net block owner and have this IP shut down. It is already on our internal black lists and it’s attacks are blocked by the Wordfence firewall.

    If you’re a theme or plugin developer and your theme or plugin is listed above, we recommend you put some effort into ensuring that all your customers have already upgraded to your newest theme, assuming you’ve fixed your vulnerability. This IP is exploiting these vulnerabilities because they provide results, so it’s likely there are still a few vulnerable sites out there.

    If you’re a WordPress user, the free version of Wordfence will protect you against the exploits we’re seeing from this IP. As new attacks emerge, we improve our firewall rules which we release to our premium customers in real-time and to our free customers on a 30 day delayed schedule. That’s why we recommend you upgrade to Wordfence Premium.

    The post Profile of a Russian Attack IP appeared first on Wordfence.