Online Services

Tag: Wordfence

  • 8 Reasons Why You Should Choose Wordfence to Clean Your Hacked Site

    At Wordfence we know you have a choice between site cleaning vendors. We feel strongly that you should choose ours because it has very tangible benefits over any other site cleaning service available. So to save you some time, I’d like to describe a few compelling reasons why you should choose Wordfence to clean your hacked site.

    1. We don’t set you up for recurring billing.

    At Wordfence we understand that our business model should not affect how much you pay for site cleaning. Your site is hacked and you need it fixed. You don’t want to be signed up for a monthly or yearly recurring subscription of some sort.

    Our pricing works the way you’d expect an incident response and forensic service to work: A single site cleaning costs $179 and that’s it. Your card will not be repeat billed. It’s intuitive, straightforward and completely transparent. We even include a Premium Wordfence license with every site cleaning that is completely free. This gives WordPress site owners the best firewall and malware detection in the business and it’s included at absolutely no cost to you.

    2. Our prices are the most competitive in the industry.

    At $179 for a site cleaning, our site cleaning service is extremely cost effective. We’re able to maintain the excellent hands-on service and quality we provide because we get tremendous value from the forensic intrusion data we gather during each site cleaning.  When we clean your hacked site, we discover how an attacker gained access and we share that information with you. We also analyze the footprints they left behind and we provide that information to you too. Then we feed that data into our software products like the Wordfence plugin and it improves our protection and detection capability. This helps improve our product and it helps make the larger online community safer.

    Because our larger customer base benefits from the data we get from each site cleaning, we’re able to keep our pricing super competitive while giving you the best incident response and customer service experience in the business.

    3. Our team is highly trained and certified

    Our two senior analysts are Colette Chamberland and Brad Haas. They both hold multiple forensic and security certifications including CEH, CHFI, CISSP, GCFA, and GCIH  certifications. Colette has previously worked for NASA at their Langley Research Center. Brad joins us from US STRATCOM (Strategic Command) and he brings a wealth of security and incident response experience both from his military and intelligence background and his experience in incident response.

    Our team is guided and mentored by Brad and Colette. We provide excellent training and mentorship and the best tools for them in the business.

    4. We have turned site cleaning into a software problem

    At our core, Wordfence is a software engineering organization. Rather than treat each hacked site as a new and isolated problem, we have spent a lot of time thinking about how new customers can benefit from what we already know about hacked websites. We know that each hacked site does present some new challenges and requires the intelligence of an analyst to bring it back into production. But we also know that many hacked sites have a lot in common and that we can use this common data to more efficiently and effectively clean and repair a hacked site.

    We have developed an internal tool we call ‘Omega’ which our analysts use to very quickly analyze and repair a hacked site. Omega uses data from our Threat Defense Feed and from the wealth of knowledge and experience our site cleaning team has gained through cleaning thousands of hacked sites. It also provides a standardized way to approach a hacked site, analyze the intrusion and remediate the hack.

    We treat Omega as an internal software product and it is constantly evolving, improving and getting smarter as the attacks we see evolve and as our engineers come up with new ways to make Omega more effective at assisting our analysts in their forensic work.

    5. Our Process is safe, secure, thorough and very effective

    Our senior analysts and technical leads have created a site cleaning process that ensures that:

    • Your data remains secure. Our clients’ sites frequently include their own customer personally identifiable information (PII). We understand the importance of that data remaining secure and our process ensures that your site data and customer PII remains secure at all times.
    • Our process is safe. We start by ensuring that a full backup is taken of your site and this backup is stored securely and used to perform the site remediation on a separate secure virtual machine that is created just for you. At no time is a site cleaning done on a customer’s live production website. This drastically reduces risk and allows our analysts to be more effective at finding and repairing the infection.
    • We are very effective. Using Omega, our internal forensic tool, along with the extensive training that our team receives and the best tools and techniques in the business, we are extremely effective at finding and completely removing an infection.

    6. Our team and systems get smarter with every site cleaning

    The Threat Defense Feed is a major part of all Wordfence products and services and this feed is the result of our forensic investigation efforts. Internally we have a process that takes all of the attack data we receive from compromised websites and we translate that data into patterns we can use to improve our detection capability. We also turn some of the data into firewall rules that we can use to improve Wordfence’s protection capability.

    Our Threat Defense Feed data also powers our forensic investigation tools. That means that with every site we clean, our detection, protection and repair capability continues to improve. The result is that you benefit from a site cleaning service that has the intelligence gained from thousands of forensic investigations built into it.

    7. We offer a complete service.

    A site cleaning and forensic investigation is far more than simply bringing a hacked site back to life. At Wordfence site cleaning we offer a complete service:

    • We start by capturing a backup of your site to ensure that your data stays secure, we have a snapshot in time to aid our forensic analysis and in case the damage to your site is ongoing.
    • Your site is throughly cleaned by our team.
    • Our team investigates how an attacker gained entry and how the site was compromised.
    • We remove any malware, malicious links or content in your posts, pages, database or source code.
    • We include a detailed report and this report includes the above information – how the site was compromised and what malicious code or content we found.
    • We provide a detailed checklist to help prevent your site from being compromised in future.
    • We include a Wordfence Premium license key to help protect your site in future at no additional cost to you.

    8. Excellent customer service

    We understand that repairing a hacked site is very high priority. You need your site back in production fast to minimize the damage it does to your search engine ranking and your brand. We also understand that clear communication is very important when dealing with a crisis.

    Once you contact our team and we start the site cleaning process, we carefully monitor how your site cleaning is progressing and ensure that it moves forward as quickly as possible and you continue to receive clear communication and updates from us.

    Our entire site cleaning team is based in the United States. Hiring forensic analysts locally means we have a close relationship with each analyst and they are able to effectively communicate with our customers in the major English speaking markets that we serve.

    Quotes from our customers:

    “To the Wordfence team. Thanks for all of your help on my sites.  I have been really impressed with your business model and execution of services.  It feels like I have my own security team.”

    ~Ben

    “One of my websites got hacked… Thanks for cleaning it up Wordfence Cleaning Team. Great job!”

    ~Alexander

    “It’s taken some time to get a handle on it, but thanks to the team over at Wordfence Security, things are now looking in the clear and Google has once again given Business Cat the clean bill of health.”

    ~Tom

    “Thank you Kathy. I am happy that this work was done so fast.”

    ~Tomas

    “Many thanks for not only sorting the issues on my website but for your comprehensive reply.”

    ~Stuart

    “Thanks so much for your work on this. It means I could focus on getting my actual paid work out the door instead of messing about with this.”

    ~Chris

    Get your site cleaning started

    If you have a site that has been hacked, visit this page to start the site cleaning process now and our team will get right on it. Our checkout process gives you the ability to securely send us your site credentials and once checkout is complete, our team will respond quickly and will get your site back into production and provide you with the tools to prevent a future compromise. We’re looking forward to hearing from you.

    Community Site Cleaning Resources

    We understand that some members of our community may not be able to engage the services of a paid site cleaning service. We have provided our community with tools to help empower them to clean sites themselves. If you would like to clean your own site, you will find the links below very helpful. We also encourage you to read the additional content in our Learning Center which will help you gain a more complete understanding of website security. Here are a few resources for website owners who want to clean their own hacked site:

    The post 8 Reasons Why You Should Choose Wordfence to Clean Your Hacked Site appeared first on Wordfence.

  • Wordfence Forensic Team and Site Cleaning Officially Launches

    Wordfence Forensic Team and Site Cleaning Officially Launches

    Today we are proud to officially announce the formation of the Wordfence Forensic Team and the launch of our site cleaning services. I’d like to take a moment and explain why we went into this business, the unique approach that Wordfence takes to repairing hacked sites and in conducting forensic analysis and investigation – and why this is great for Wordfence customers.

    What is Wordfence Site Cleaning?

    If you have a hacked WordPress website, we have a team of highly trained forensic investigators that are ready to help. The service is simple: We’re charging $179 to rapidly get your website clean and back into production. This includes:

    • Cleaning the infection.
    • Investigating how the attackers gained entry.
    • Removing any malicious code, links or other content in your posts, pages, comments and source code.
    • Providing an in-depth report of the infection removal and investigation.
    • We provide a detailed checklist to protect your site from future attacks.
    • Your site cleaning includes a 1 year Wordfence Premium license to keep you safe, worth $59.

    Meet the Team

    One thing I’ve learned as a CEO is that we can best serve our customers by building a team of people who are world-class at what they do. We went out and found the best forensic investigators we could and added them to the core of our team. We started by bringing on board two senior experts in the field:

    resizeccColette Chamberland is one of our two Senior Security Analysts and is a Certified Hacking Forensic Investigator (CHFI) and Certified Ethical Hacker (CEH). She has over 5 years of hands-on forensic investigation experience. You’ll also recognize her name as the person who discovered one of the possible entry points in the Panama Papers breach. She brings a wealth of experience, leadership and knowledge and uses it to effectively lead and mentor our team.

    Brad HaasBrad Haas is our second Senior Security Analyst and joined us from STRATCOM (United States Strategic Command). He is an ISC2 CISSP, GIAC Certified Incident Handler (GCIH) and GIAC Certified Forensic Analyst (GCFA). Brad has over 7 years of forensic investigation experience and provides strong process and technical leadership in forensic investigations for our team along with a hands-on approach.

    Brad and Colette have been working hard at optimizing our site cleaning processes, policies and procedures to ensure customer data confidentiality, integrity and to get our customer sites back online and available as soon as possible.

    Our site cleaning team is now seven highly trained investigators and we continue to bring in more team members as quickly as we can. To recruit, evaluate and train site cleaners quickly and effectively, we decided to turn the challenge into a software problem. We have created a job application system that automatically creates an ‘infected’ virtual machine that our forensic investigator applicants need to clean as the very first step in their job application process. We then take our applicants who have scored well through a rapid evaluation process and if they are accepted into the team, we include excellent training and mentorship from our senior analysts. If you think you might be a good fit for the team we welcome you to apply.

    Why does Wordfence Clean Hacked Sites?

    Our business is to protect WordPress websites from hackers. That means we need to block known and unknown attacks using the Wordfence Firewall. It also means we need to be very good at detecting if a site has been compromised using Wordfence Scan. To be good at both of these things, we need to know how sites are compromised and what indicators of compromise (IOCs) or footprints a hacker leaves behind.

    The best way for us to get this data is to investigate sites that have recently been hacked. Internally we have a sophisticated process that turns the data we gather from hacked sites into what we refer to as our Threat Defense Feed or TDF. The TDF includes the firewall and scan rules that are the product of our forensic investigation efforts. This flows out to the Wordfence plugin in real-time, continually updating our scan and firewall capability to provide you the best protection available.

    What this means is that when you install Wordfence, you have a growing team of forensic investigators working hard to continually update Wordfence with the newest attacks that are occurring on the ground and to protect you from those attacks. The information gained from each hacked site we investigate is used to protect all of our customers from getting hacked using the same method. Furthermore, any footprints an attacker leaves behind are used to improve our scan capability so that we can provide an early warning should the worst case scenario occur.

    Early beach detection and blocking attacks on WordPress websites is what we do. With our forensic investigators constantly increasing the intelligence of Wordfence via the TDF, you have a system that provides the best WordPress protection available.

    Giving Back to the Community

    Most firewalls for WordPress are expensive. With Wordfence, you get the Threat Defense Feed if you’re a free or a paid customer. The only difference is that our Premium customers receive real-time updates while our free community customers are delayed by 30 days.

    As our forensic investigators analyze breaches and we build more intelligence into the TDF, that data flows out to all Wordfence users eventually and does an excellent job of keeping the WordPress community safer. When you choose to have your hacked website cleaned by the Wordfence team, know that the data from your site cleaning ultimately ends up helping to protect the WordPress community.

    Excellence in Customer Service

    I’m constantly surprised by how much positive feedback our customer service representatives and forensic team receives. Today is our official launch but we have actually been cleaning hacked WordPress sites since April 4th.

    Part of our focus at Wordfence, whether we’re providing support for our software or for forensic services, is to provide excellent customer service. Since we soft-launched our site cleaning service I’ve seen many customers who have gone from being frustrated about a hacked site to being overjoyed at how quickly and effectively our team has turned their site around.

    We knew that to provide the best service available for site cleaning, we would have to find the best people – and I’m very proud of our team’s technical ability along with their ability to serve and communicate with our customers and turn an unpleasant situation into a happy customer along with data that helps protect the broader community.

    Let’s Make WordPress and our Community Safer Together

    If you’ve been hacked, contact us immediately by visiting this page and our team will get right on it. We look forward to working with you to get your site repaired quickly and also ensuring that the rest of our community is protected from attacks that are similar to the one you experienced.

    The post Wordfence Forensic Team and Site Cleaning Officially Launches appeared first on Wordfence.

  • XSS Vulnerability in Wordfence 6.1.1 to 6.1.6. Severity: 6.1 (Medium)

    An hour ago a security researcher, Kacper Szurek, reported a reflected XSS vulnerability in the current version of Wordfence. Wordfence is now using CVSS as our standard vulnerability scoring mechanism. The severity of this vulnerability is 6.1 (Medium).

    Impact

    This only affects Wordfence users who have the Wordfence firewall disabled. Wordfence has built in protection against XSS vulnerabilities and has had since version 6.1.1, so if your firewall is enabled you are not affected. If you have the firewall in learning mode or disabled, you are not protected against this vulnerability.

    What to do

    We have already released a fix. If you have Wordfence set to auto-update then it will automatically update to Wordfence 6.1.7 within the next 24 hours and you don’t have to take any action. If you have the Wordfence firewall enabled, you are already protected and were never affected by this issue.

    If you have Wordfence auto-update disabled and you have the firewall in learning mode or disabled, we recommend you sign into your website and manually upgrade Wordfence to version 6.1.7 now. We also suggest that you consider enabling your Wordfence firewall if that is feasible for you.

    Vulnerability Info

    CVSS Severity: 6.1

    CVSS Vector: CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N

    Vulnerability Type: Reflected XSS (Cross Site Scripting)

    Kacper has shared a proof of concept for this vulnerability with us which we have verified. We will not be sharing it at this time but may share it at a future date.

    Further notes on vulnerability disclosure by Wordfence

    At Wordfence we practice responsible disclosure both on products belonging to other vendors and on our own product. Even though this is our own product, you will see a style of disclosure here that uses the same standards that we use when we disclose vulnerabilities relating to other vendor’s products.

    Wordfence has now standardized on using the CVSS 3.0 vulnerability scoring system which we have included in this post. Going forward we will include the CVSS score of every vulnerability in the subject of our blog posts and in an email alert we send to our community. This gives our community an immediate indication at a glance of the severity of a vulnerability. It also provides an objective methodology of scoring vulnerabilities that is not subject to opinion or bias.


    The post XSS Vulnerability in Wordfence 6.1.1 to 6.1.6. Severity: 6.1 (Medium) appeared first on Wordfence.

  • Announcing a new Firewall, a Threat Defense Feed and a New Approach

    Announcing a new Firewall, a Threat Defense Feed and a New Approach

    This morning at 9am Pacific time we rolled out a new kind of firewall to over 1 Million active WordPress websites. The new Wordfence firewall comes with a Threat Defense Feed that updates our firewall as new threats emerge. It also continuously updates our malware scan as we discover new malware patterns through our forensic research.

    If you have auto-update enabled in Wordfence, you will automatically be upgraded to 6.1.1 today which will include the new firewall and features. You can manually update by signing into your WordPress site and upgrading to Wordfence to 6.1.1 or you can download Wordfence from the official WordPress plugin repository.

    I want to share with you some of the journey that we took to arrive at this day. About 9 months ago we took a long hard look at Wordfence and asked the question: “How can we do a better job of stopping hacks and detecting them early?”.

    We also looked at existing firewall providers and discovered they could be doing a better job. And then we looked at our own malware scan and realized that it could benefit from a few improvements.

    So we set ourselves an ambitious goal:

    • Build an excellent forensic analysis team to discover the newest malware infections and new attacks that are used to break into sites.
    • Build a new kind of firewall that stops all attacks immediately, including zero day and emerging attacks.
    • Radically improve intelligence in our scan.
    • Continually feed the data our forensic team uncovers into our firewall and scan.

    We worked for 7 months on the project and about 2 months ago we thought we had finished the firewall. But then we discovered a way to radically improve our protection against SQL injection attacks. It meant building an SQL parser into Wordfence that is both extremely fast and is able to understand SQL the way a database does and determine if something is malicious or not. It was worth taking the extra time to include this important functionality and so we did exactly that.

    Then a few weeks ago, once again we thought we were ready and we realized we could build protection into the firewall against privilege escalation attacks. When you run Wordfence’s firewall, it knows who your users are so the firewall is able to make decisions about what to block more intelligently. So we went ahead and built that into Wordfence 6.1.1 too.

    Instead of letting the marketing team rule, we gave the engineers enough space to solve these very hard problems with innovative solutions.

    During the past month we have been quietly beta testing Wordfence 6.1.1 and our beta community has been an invaluable source of feedback and bug reports. Thank you very much to everyone who kindly participated in our public beta testing. You have helped turn Wordfence 6.1.1 into a rock solid enterprise-ready WordPress protector.

    We have also been running Wordfence 6.1.1 Beta on this site for longer than a month and it has worked perfectly. At times we have had over 3,000 concurrent users on the site and huge traffic spikes. Last Thursday and Friday thanks to the huge amount of press we received for our ground-breaking research into how the Panama Papers were leaked, we experienced a large sustained traffic spike and the Wordfence firewall just yawned and carried on doing a great job of serving up pages and protecting us from attacks.

    It’s really cool watching your own software block hackers in real-time. Instructions on how to watch that below.

    Today we are officially announcing the release of Wordfence 6.1.1 along with our Threat Defense Feed. Here are the details:

    The Firewall

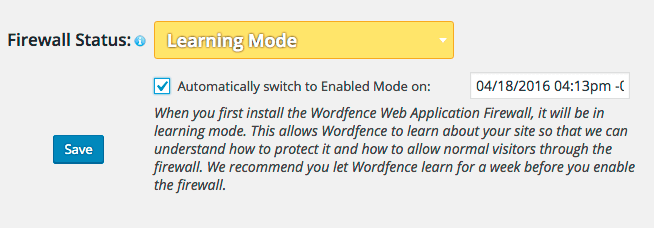
    The Wordfence firewall is installed with 6.1.1 and you will see a new ‘Firewall’ menu option appear in your Wordfence menu. When you arrive on the firewall configuration page, Wordfence should be in Learning Mode if you just upgraded to 6.1.1. It will look like this:

    Screen Shot 2016-04-11 at 4.13.56 PM


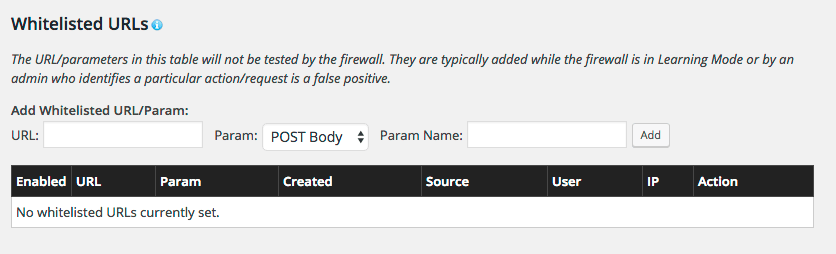
    Wordfence firewall will learn for a week and then automatically switch to “Enabled and Protecting”. During this one week learning period, anything that would have been blocked will automatically be whitelisted. You can scroll to the bottom of the firewall page and see the list of whitelisted items as they grow:

    Screen Shot 2016-04-11 at 4.16.35 PM

    If you don’t like something that has been whitelisted during Learning Mode or think it may be a real attack, you can simply remove it once the firewall is enabled.

    If you don’t want to wait a week you can speed things up by:

    • Visiting all pages and taking all actions you can think of on your site. This includes working in the WordPress admin console, submitting forms on your site and doing everything else that normally happens on your site. This will allow Wordfence to rapidly learn about your site.
    • Then enable the firewall and keep an eye on what it blocks in live traffic. Read on to understand how to view firewall activity in Live Traffic.

    Changes to Live Traffic and How to see what the Firewall has blocked

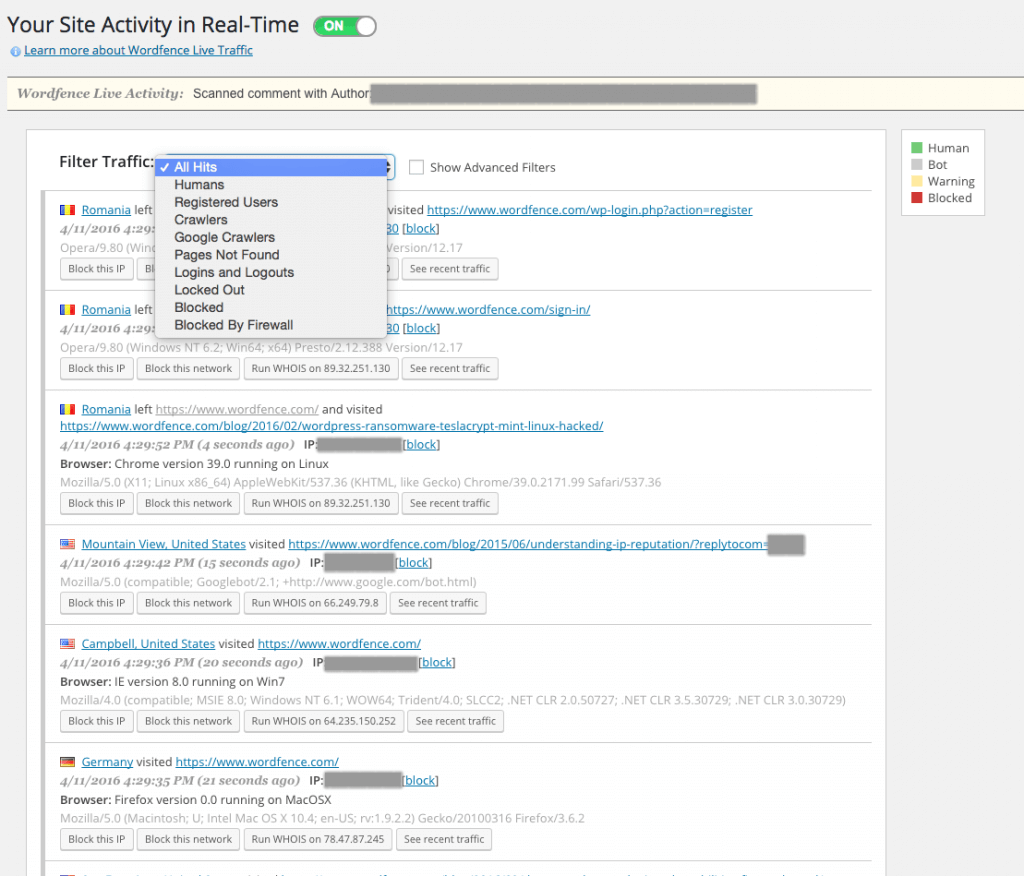
    Wordfence Live Traffic has been given a redesign that I can only describe as spectacular. We have added a drop-down list that lets you filter what kind of traffic you want to see:

    Screen Shot 2016-04-11 at 4.29.35 PM

    Simply select the option “Blocked by Firewall” to see what your firewall has blocked recently. You’ll be surprised what shows up. We have had quite a few attacks on our own site blocked by Wordfence 6.1.1.

    You’ll notice that Live Traffic has an advanced filters option that lets you filter your live traffic any way you can possibly imagine.

    A Threat Defense Feed through Excellent Forensic Analysis

    A great firewall and great scan engine are no good without continuous updates. We started by building an excellent forensic analysis team. Every day our team goes out and analyzes hacked sites and brings that on-the-ground intelligence back into Wordfence.

    Malware samples are turned into signatures used by our scan engine. New attacks are turned into firewall rules which update our firewall logic.

    We unified this flow of data under a single umbrella called the Threat Defense Feed. This feed constantly updates Wordfence’s ability to block attacks and to detect infections or malicious activity.

    Our premium Wordfence customers receive a real-time version of the feed. If a new threat emerges, we can update your rules within minutes. Our free customers receive a delayed version of the Threat Defense Feed.

    Changing the Game on Attackers

    We realized that the status quo isn’t going to cut it if we are to succeed in our mission of making the web safer and protecting our customer’s sites. Wordfence 6.1.1 isn’t just a new product with new data flowing into it. It is an organizational change for us.

    We have had to build a forensic analysis team by bringing senior analysts on board with tremendous depth of experience. Those senior team members have been developing processes and training up more junior colleagues to rapidly get them up to speed.

    We have also had to scale up our operations, make new capital investments in hardware, in software and in operations personnel.

    We have also brought on board additional senior engineers and customer service staff. We have been hiring so quickly that we decided to turn hiring into a software problem which you would have experienced if you’ve been through one of our tests for forensic analysts. Don’t worry, you still get to talk to us humans as part of the process.

    What we’ve ended up with is one of the fastest growing and best performing information security organizations in the world. It has been an incredible experience for me personally during the past 2 years, hiring people who are smarter than I am, stepping back and watching them guide our product, serve our customers and create engineering solutions that are incredibly innovative and that provide a new kind of protection that is able to defeat the new threats that we are seeing.

    I’m incredibly proud of our team for creating, testing and shipping Wordfence 6.1.1. Special thanks to Matt Barry our lead developer and Matt Rusnak our QA analyst who both worked tirelessly to improve, find new ways to break and then continue to improve 6.1.1. Thanks guys, you are both legends. Thanks also to the rest of the team who contributed tremendously, you know who you are and you’re amazing!

    I speak for the whole team when I say that we are proud to have your trust and to have you as a customer. We are working hard to deliver the level of engineering, research and innovation you have come to expect from Wordfence. And we look forward to a long relationship with our community and our premium customers as we continue to deliver the best available protection for your WordPress website.

    Mark Maunder – Wordfence Founder & CEO – April 2016.

    Update: At 11am Pacific time we release 6.1.2 which is a point release that fixes a minor issue. It fixed fatal error when using a whitelisted IPv6 range and connecting with an IPv6 address. This is an edge case and would have only affected a small number of sites.

    Official Press Release available here.

    Press contact: Dan Moen at press@wordfence.com.

    Wordfence is hiring. If you’re passionate about tracking attackers and their methods and want to join our forensic analysis team, we’d love to hear from you.

    The post Announcing a new Firewall, a Threat Defense Feed and a New Approach appeared first on Wordfence.