Online Services

Tag: WordPress Security

  • IP Blacklist Update: The Launch and Evolution of The Wordfence IP Blacklist

    One of our passion projects at Wordfence has been to find a way to create and run an IP blacklist. We have known for a long time which IPs are attacking the sites we protect and that if we can block those IPs outright, it would be a powerful way to improve the security we provide to our customers.

    Blocking a bad IP completely is more effective and safer than just blocking its malicious requests, because you don’t allow it to gather information about the target website it is about to attack.

    We launched the Wordfence Premium IP Blacklist 1 month ago and it has been incredibly effective at improving the security of the websites that Wordfence protects.

    Today I want to share the story behind why we decided to create the Worfence Premium IP Blacklist, how we created and launched it, how it has evolved rapidly to contain over 4,000 dynamically updated IPs and how quickly it is growing.

    Creating and Launching the IP Blacklist

    When we conceived of the IP blacklist about a year ago the challenge we had was to have a way to block bad IPs accessing our customer sites and let the good guys through without actually distributing a list of bad IPs to customer sites. We wanted to avoid distributing the list so that we didn’t also provide other attackers with a list of possibly compromised targets to attack.

    The trouble with not distributing a list of bad IPs is that the obvious alternative is to have our customer sites look-up whether or not a visitor IP is bad for every request. That would have awful performance implications. It would mean a visitor to a site has to wait until the lookup has completed until their page loads. Yuck!

    After background-processing this problem for several months our team came up with a way of getting the best of both worlds. We realized that we could distribute the list of IPs as “hash prefixes” which achieve both of our goals. Our customer sites would not be slowed down because 99.9% of good requests would not need to do a lookup on Wordfence servers. It also made it very difficult for attackers to reverse engineer the IP blacklist to reveal new targets.

    Blocking baddies without blocking goodies

    Once we had figured out how to implement the list, the dev team started work on it and once complete the feature spent a long time with our quality assurance team. We wanted to do a great job of protecting customer sites while creating zero interference with their legitimate traffic.

    First, we developed a way for anyone blocked by the list to report false positives. Since launch, the number of false positives (good people being blocked accidentally) reported is  very low, which is impressive when you consider that the IP blacklist has processed hundreds of millions of requests since launch.

    Then we took a “phased” approach to the launch.

    Blacklist Phase 1:

    We launched the blacklist with a small number of 100 IPs on the list. Then we gradually added around 100 additional IPs by hand every day or two, until we hit 1000 IPs. We constantly evaluated how the list was doing and if there were any false positive reports. There were none.

    Blacklist Phase 2: 

    Once we hit that point, we had not received any false positive reports, so we switched to “dynamic” mode where the list auto-updated hourly. The algorithms we used in dynamic mode phase 2 to continuously identify bad IPs were “coarse” and only included the worst offenders and excluded some IPs that are engaging in lower frequency attacks.

    Blacklist Phase 3:

    In phase 3 we started optimizing our algorithms and lowering the ‘bar’ for what we considered a bad IP. We did this gradually and are still in this phase as we continue to increase the sensitivity of our algorithms to detect malicious IPs. The list is now fully live and is blocking a large number of requests from malicious IPs on our Premium customer sites every day.

    The Growth of the Wordfence IP Blacklist

    The graph below does a great job of illustrating the phases described above and the gradual way we have grown the IP blacklist and how it continues to grow:

    You can see how we steadily added to the IP blacklist manually until it hit 1000. This took about a week. Then we switched to dynamic mode and you begin to see the fluctuations in the number of IPs on the list as the number of attackers changes over time.

    As we increased the sensitivity of our algorithms there is a steady increase in the number of IPs on the list. We are currently at around 4,500 IPs on the list and we continue to increase sensitivity.

    Changes Over Time: The Blacklist is a Living Breathing Thing

    The Wordfence blacklist isn’t something we just continually add to. It is a living breathing thing which is updated continuously. IPs are continuously added and removed. You’ll notice a dip in the chart above which shows how we gradually removed over 1,000 IPs over a 1 week period as they stopped behaving maliciously.

    IPs that start attacking are immediately added to the blacklist. IPs that stop attacking are removed over time and that time is relatively short – usually a few days, depending on their behavior.

    In the chart below we show how dynamic the list is over a single 24 hour period. We chose the 11th of April for our example. You can clearly see that during the day we are constantly adding malicious IPs as they become active and constantly removing IPs that are no longer behaving badly.
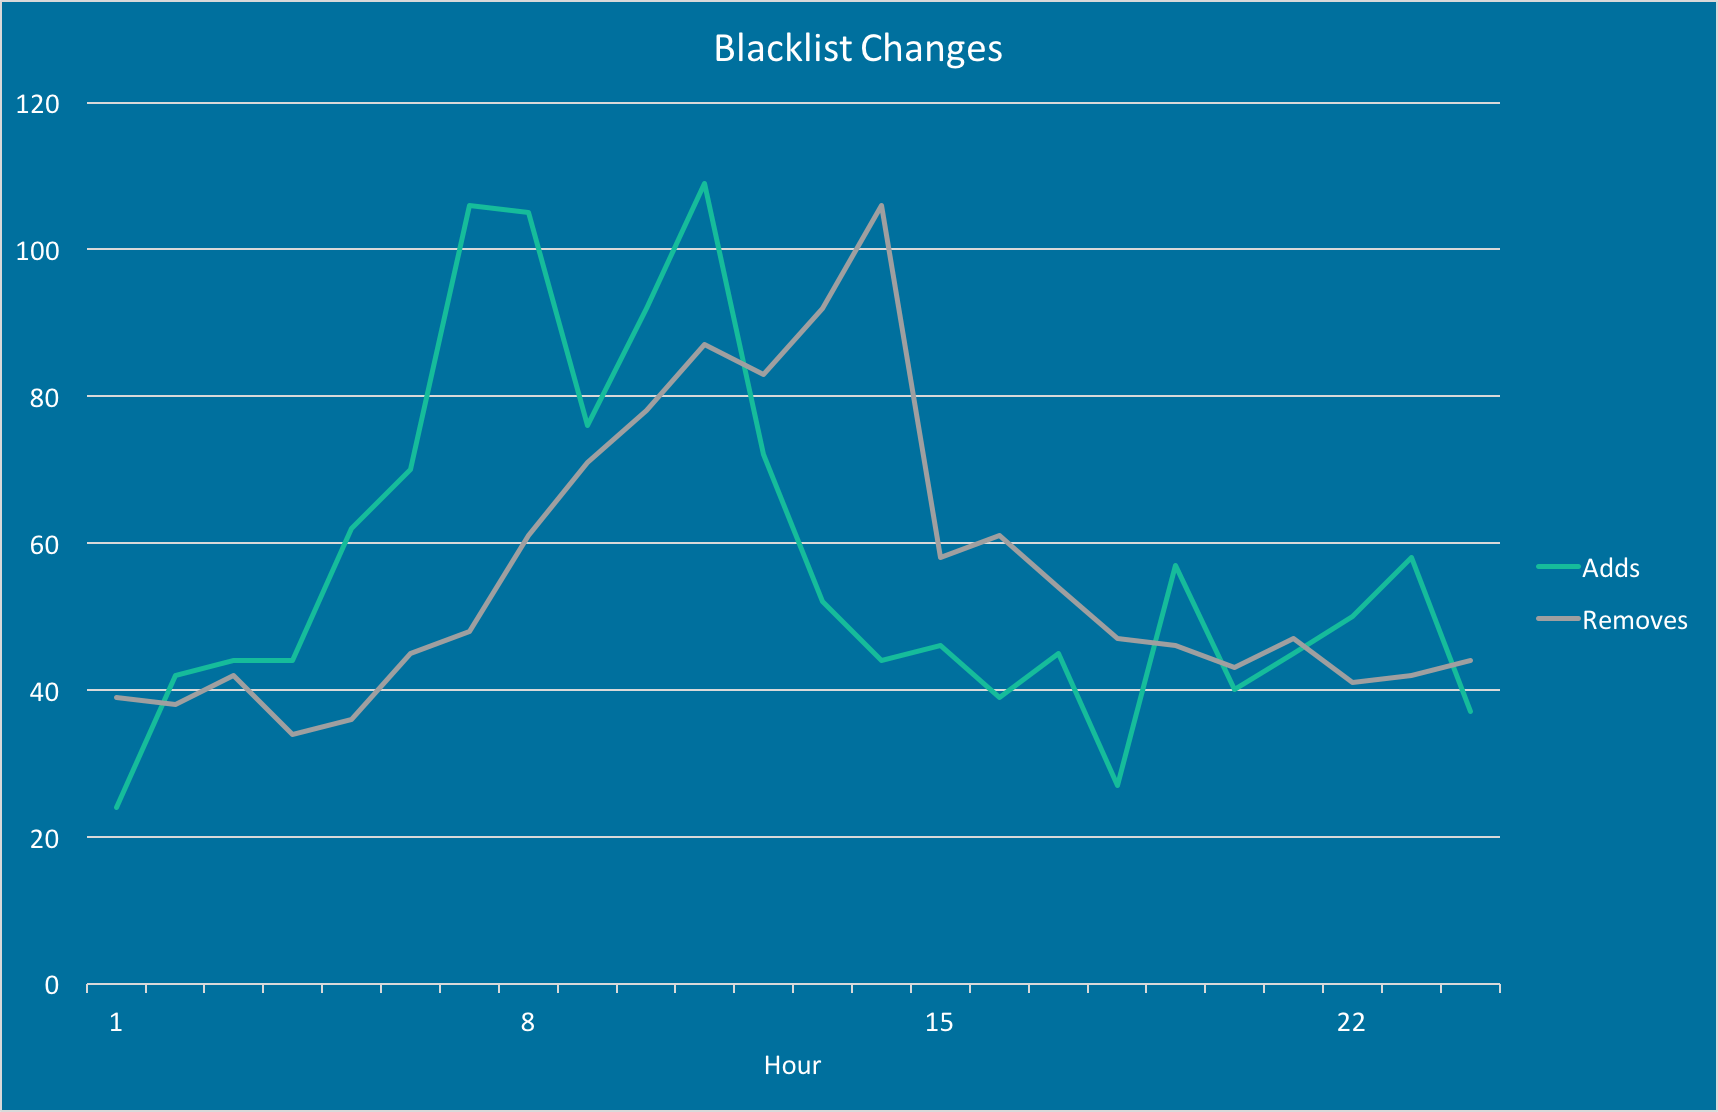
    I know that many of you are “active managers” of your WordPress site security. It can begin to feel like a video game as you’re monitoring live traffic, adding IPs to your block list and blocking networks or user-agents. The blacklist solves that problem comprehensively. It relies on an incredible amount of global attack data and does an excellent job of blocking far more malicious IPs that any administrator could manage. It also unblocks IPs as they stop behaving badly to ensure that false positives don’t occur.

    The Wordfence Premium blacklist blocks new malicious IPs very quickly and any IPs that stop behaving maliciously are quickly unblocked. From the perspective of a WordPress site owner, in my opinion, it is a site admin’s dream come true.

    Ranking Signals for IP Reputation

    We think about IP reputation much the same way as Google thinks about their search algorithm. We use what we refer to as ‘ranking signals’ which are factors that influence how malicious we consider an IP address to be.

    We have no plans to publicly disclose all the ranking signals that we use for IP reputation. We don’t want attackers to be able to completely reverse engineer our methods. But as we grow the list to a significant size, we may make suggestions for network owners to help them ensure that the IPs on their network retain a healthy ranking.

    For example, if you are a hosting provider, a compromised website or hosting account can be used to attack other sites and online targets. That would negatively affect your IP’s ranking on blacklists. Responding quickly to a compromised account or website will ensure that the site IP is not blacklisted and other accounts on the same system are not negatively impacted.

    Next Steps: Optimizing Current Signals, Developing New Signals

    This week we wrote about thousands of home routers that are being used to attack WordPress websites that Wordfence protects. These home routers are engaging in very low volume attacks for short periods of time. This is a new signal that we have discovered and is a relatively weak signal. But when combined with other signals, it becomes strong and clearly reveals IPs that belong on our blacklist.

    We are constantly engaged in R&D like the research we performed to uncover the hacked home routers. This helps us discover and implement new ranking signals to grow and optimize our IP blacklist.  Now that the blacklist is live and dynamic, our goal is to continuously improve, measure and evaluate our algorithms going forward.

    The real-time IP blacklist is one of many great security features in Wordfence Premium. If you aren’t already using Wordfence, try out our completely free (and awesome) plugin today. Then when you are ready to upgrade to Premium, you can visit our home page on wordfence.com to find out more.

    The post IP Blacklist Update: The Launch and Evolution of The Wordfence IP Blacklist appeared first on Wordfence.

  • Thousands of Hacked Home Routers are Attacking WordPress Sites

    Last week, while creating the Wordfence monthly attack report, we noticed that Algeria had moved from position 60 in our “Top Attacking Countries” list to position 24. That was a big jump and we were curious why Algeria had climbed the attack rankings so rapidly.

    What we discovered on closer examination is that over 10,000 IP addresses in Algeria were attacking WordPress websites in March. Most IPs were only launching between 50 and 1000 attacks during the entire month.

    The following chart is a histogram. It groups IP addresses by the number of times they attacked. As you can see by the spike on the left, the most common number of attacks was around 100 to 200 for an IP address. Few of the attacking IPs generated more than 2,000 attacks during the entire month of March, 2017.

    We wanted to learn more about these attacking IPs, so we dug a little deeper.

    A Botnet Using Burst Attacks

    We extracted the list of Algerian attack IPs and we included the time of first attack logged and the time of last attack logged. The majority of the IPs spent just a few hours attacking and then stopped for the rest of the month. The histogram below shows how many IPs spent less than a day (shown as 0) attacking compared to those that spent 1 or more days. As you can see over 7,000 IPs spent just a few hours attacking during March before they stopped.

    These IPs switch on, perform a few attacks and then switch off and aren’t heard from again for a month. What we have found is a botnet that is distributed across thousands of IPs. Each IP is only performing a few attacks, those attacks are spread across many websites and the attacks only last a few minutes or hours.

    The attacker controlling this botnet is using several evasive techniques. They are spreading their attacks across a very large number of IP addresses. They are using low frequency attacks to avoid being blocked. They are also spreading their attacks across a large number of WordPress sites.

    These evasive techniques indicate a higher level of sophistication than we see from, for example, “PP Sks-Lugan” which we’ve written about in the past where we see a single IP generating millions of attacks.

    Hacked Home Routers Hacking WordPress

    When we looked at who owns each of the attacking IPs in Algeria, we found, over 97% of them are owned by Telecom Algeria. There are approximately 30 different ISPs in Algeria. We do see some attacks from other networks, but nothing compared to the volume that originates from Telecom Algeria.

    The attacks we saw in March originated from the following networks:

    • 41.96.0.0/12 which ranges from 41.96.0.0 to 41.111.255.255 had 4671 attacking IPs in March.
    • 105.96.0.0/12 which ranges from 105.96.0.0 to 105.111.255.255 had 4591 attacking IPs in March.
    • 154.240.0.0/12 which ranges from 154.240.0.0 to 154.255.255.255 had 715 attacking IPs in March.
    • 197.112.0.0/13 which ranges from 192.112.0.0 to 197.119.255.255 had 401 attacking IPs in March.

    Telecom Algeria is the state owned telecommunications provider in Algeria. It is therefore the largest telecommunications provider in the country.

    We performed a network survey on a sample of 8,962 IPs on Telecom Algeria’s network. We received responses from 3,855 IP addresses.

    Out of those IPs we discovered that  1501 are Zyxel routers that are listening on port 7547 and are running “Allegro RomPager 4.07 UPnP|1.0 (ZyXEL ZyWALL 2)”.

    Allegro RomPager 4.07 is an embedded web server that has a severe vulnerability, dubbed the Misfortune Cookie by Checkpoint, who discovered it in 2014. The identifier is CVE-2014-9222.

    It appears that attackers have exploited home routers on Algeria’s state owned telecommunications network and are using the exploited routers to attack WordPress websites globally.

    Other ISPs With Vulnerable Routers

    Algeria drew our attention because its country ranking jumped from 60 to 24 in our top attacking countries for March. Once we took a closer look at the attacking IPs, we were able to identify a specific pattern of behavior for these attack IPs:

    • They generally attack for less than 48 hours and then stop.
    • Most of them generate less than 1000 attacks.
    • There is usually a large number of attacking IPs on a single ISP.

    By searching for similar patterns, we found that there are several other ISPs that seem to have the same problem that Telecom Algeria has.

    BSNL – India

    BSNL is a state owned telecommunications provider in India. During March we saw attacks from 11,495 IPs on their network.

    In a survey of BSNLs network, we found that:

    • 11,495 IPs on BSNLs network attacked WordPress sites in March.
    • Out of those attacking IPs, 4857 IPs also have port 7547 open.
    • We found that 1635 of the IPs that attacked WordPress sites are also running “Allegro RomPager 4.07 UPnP|1.0 (ZyXEL ZyWALL 2)” which is vulnerable.

    PLDT aka. Philippine Long Distance Telephone

    PLDT is the largest telecommunications provider and digital services company in the Philippines.

    In a survey of PLDT’s network we found that:

    • 3697 IPs on their network attacked WordPress sites in March.
    • 1612 of those attacking IPs on PLDTs network have port 7547 open.
    • 137 of those IPs are running “Allegro RomPager 4.07 UPnP|1.0 (ZyXEL ZyWALL 2)” which is vulnerable to remote exploitation.

    28 ISPs with Suspicious Attack Patterns Indicating Compromised Routers

    Once we could identify the attack pattern of compromised routers, we searched for other ISPs where the attack patterns fit the same criteria. That is, low frequency of attacks, each IP attacks for less than 48 hours and a large number of IPs are attacking WordPress sites from a specific ISP.

    This is the full list of ISPs we found globally where attacks that match this criteria are originating from. Notice the low “average attacks per IP column” on the right of the table (scroll right) and the large number of attacking IPs per ISP.

    What is port 7547 and TR-069 and why is it a problem?

    Port 7547 is a management port on home routers. It allows ISPs to manage the routers that their customers use on their home networks. It uses a protocol called TR-069 to provide a management interface. The TR-069 protocol can be used to provision devices, provide tech support and remote management, monitor routers for faults, for diagnostics, to replace a faulty configuration and to deploy upgraded firmware.

    This protocol and port has had at least two serious security vulnerabilities associated with it in the past 4 years.

    We have already mentioned the misfortune cookie vulnerability which targets management port 7547 and which some of the ISPs above are suffering from. RomPager version 4.07 suffers from the misfortune cookie vulnerability. In the ISPs that we are seeing attacks originating from, 14 out of 28 ISPs have remotely accessible routers that have a vulnerable version of RomPager version 4.07 on port 7547

    Another vulnerability emerged in November last year which allows an attacker to use port 7547 and the management interface to gain administrative access to a router.

    6.7% of Attacks on WordPress Sites are from Home Routers with Port 7547 Open

    In addition to the network surveys we did on ISPs from which attacks are originating, we also surveyed 865,467 additional IP addresses which have engaged in brute force or complex attacks during the past 3 days. Out of those, 57,971 have port 7547 open indicating that they are home routers from which attacks are originating.

    That means that 6.7% of all attacks on WordPress sites that we protect, during the past 3 days, came from home routers that have port 7547 open.

    Shodan, an internet survey search engine, currently shows that over 41 million devices on the Internet are listening on port 7547. The TR-069 protocol is widely used among ISPs world-wide.


    The Security Risk to Home Users

    If a home router is successfully exploited, an attacker can access your internal home network. They have penetrated any firewall function that the router provides and can also bypass router network address translation. This enables them to exploit internal targets like workstations, mobile devices using WiFi and IoT devices like home climate control systems and home cameras.

    We are already seeing bulk exploitation of TR-069 which has turned home routers into a botnet attacking WordPress sites. It is quite feasible that home network exploitation is already underway as well.

    Security Risk to the Internet at Large

    OVH was hit by a 1 Terabyte DDoS attack in September last year, one of the largest in history. Approximately 152,000 IOT (Internet of Things) devices that had been compromised generated the traffic in that attack.

    In just the past month we have seen over 90,000 unique IP addresses at 28 ISPs that fit our compromised-router attack pattern. We monitor these attacks across our customer websites which is an attack surface of over 2 million websites. We only see a sample of the attacks that all websites globally experience. If you extrapolate the numbers, it indicates that there is a very large number of compromised ISP routers out there performing attacks and acting in concert.

    At this point it would not be a stretch to say that vulnerabilities in TR-069 may have created a very large botnet which could soon generate the largest DDoS attack the Internet has ever seen.

    How ISPs can help

    Exposing port 7547 to the public Internet gives attackers the opportunity to exploit vulnerabilities in the TR-069 protocol. ISPs should filter out traffic on their network coming from the public internet that is targeting port 7547. The only traffic that should be allowed is traffic from their own Auto Configuration Servers or ACS servers to and from customer equipment.

    There are already a large number of compromised routers out there. ISPs should immediately start monitoring traffic patterns on their own networks for malicious activity to identify compromised routers. They should also force-update their customers to firmware that fixes any vulnerabilities and removes malware.

    What we are doing

    At Wordfence we run a real-time IP blacklist for our premium customers. We are adjusting our blacklist algorithms to identify and include IP addresses that engage in these kinds of attacks. We are also working to create awareness among ISPs and security professionals about the risk that TR-069 presents and how they can help to mitigate that risk.

    The post Thousands of Hacked Home Routers are Attacking WordPress Sites appeared first on Wordfence.

  • The March 2017 WordPress Attack Report

    Today we are releasing the WordPress Attack Report for March, 2017. You can also find the following previous attack reports on our blog: December 2016, January 2017 and February 2017.

    This report contains the top 25 attacking IPs for the month of March and their details. It also includes charts of brute force attack activity and complex attack activity for the period. We also include the top themes and plugins that were attacked and which countries generated the most attacks for the period.

    One of the more surprising data points in this report is the rise of Algeria as a source of attacks. After creating this report we dug a little deeper and will be releasing our additional findings regarding Algeria next week.

    The Top 25 Attacking IPs

    I’m including our usual explanation of how the table below works. If you’re familiar with our attack reports, you can skip down to the table below which contains the March data and read my comments that follow the table.

    Brief introduction if you’re new to viewing these reports

    In the table below we have listed the most active attack IPs for March 2017. Note that the ‘Attacks’ column is in millions and is the total of all attacks that originated from each IP. Further right in the table (you may have to scroll right) we break out the attacks into ‘brute force’ attacks and ‘complex’ attacks.

    Brute force attacks are login guessing attacks. What we refer to as ‘complex’ attacks are attacks that were blocked by a rule in the Wordfence firewall.

    We have also included the netblock owner, which is the organization, usually a company, that owns the block of IP addresses that the attack IP belongs to. You can Google the name of the owner for more information. A Google search for any of these IP addresses frequently shows reports of attacks.

    The hostname included is the PTR record (reverse DNS record) that the IP address owner created for their IP, so this is not reliable data but we include it for interest. For example, we have seen PTR records that claim the IP is a Tor exit node, but it is clearly not, based on traffic.

    We also include the country and a country flag. To the far right of the report we show the date in March when we started logging attacks and the date attacks stopped. For many of these IPs we logged attacks for the entire month. For some you can see there is a clearly defined attack ‘window’ where the IP started and stopped.

    The Top Attacking IPs

    Our top two attacking IPs are in Russia and Ukraine respectively. Both of them are only launching complex attacks on WordPress. Our top IP has doubled its attacks from 7 million to 15 million attacks. Our second place IP went from 7 million to 12 million attacks per month.

    The total number of complex attacks from the top 25 IPs went from 63 million in February to 85 million in March. The total brute force attacks from the top 25 IPs increased from 18 million in February to 32 million in March. This indicates an increase in how aggressively these top 25 IPs are attacking sites.

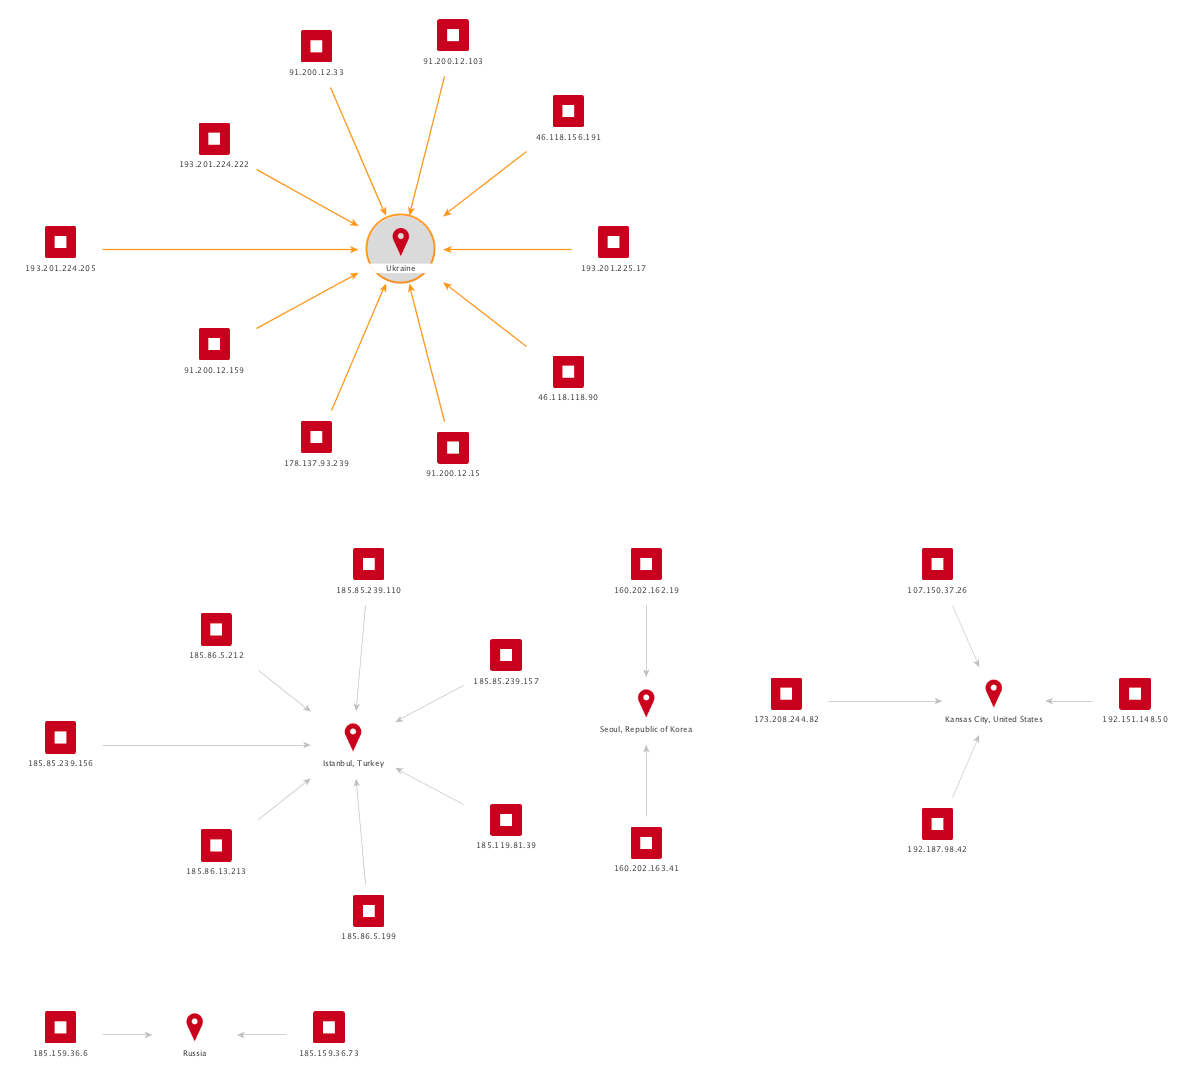
    If we cluster the top 25 attacking IPs by country, it becomes apparent that Ukraine is by far the top source for attacks. We also have a surprisingly large number of top attacking IPs from Turkey in March.


    Brute Force Attacks on WordPress in March 2017

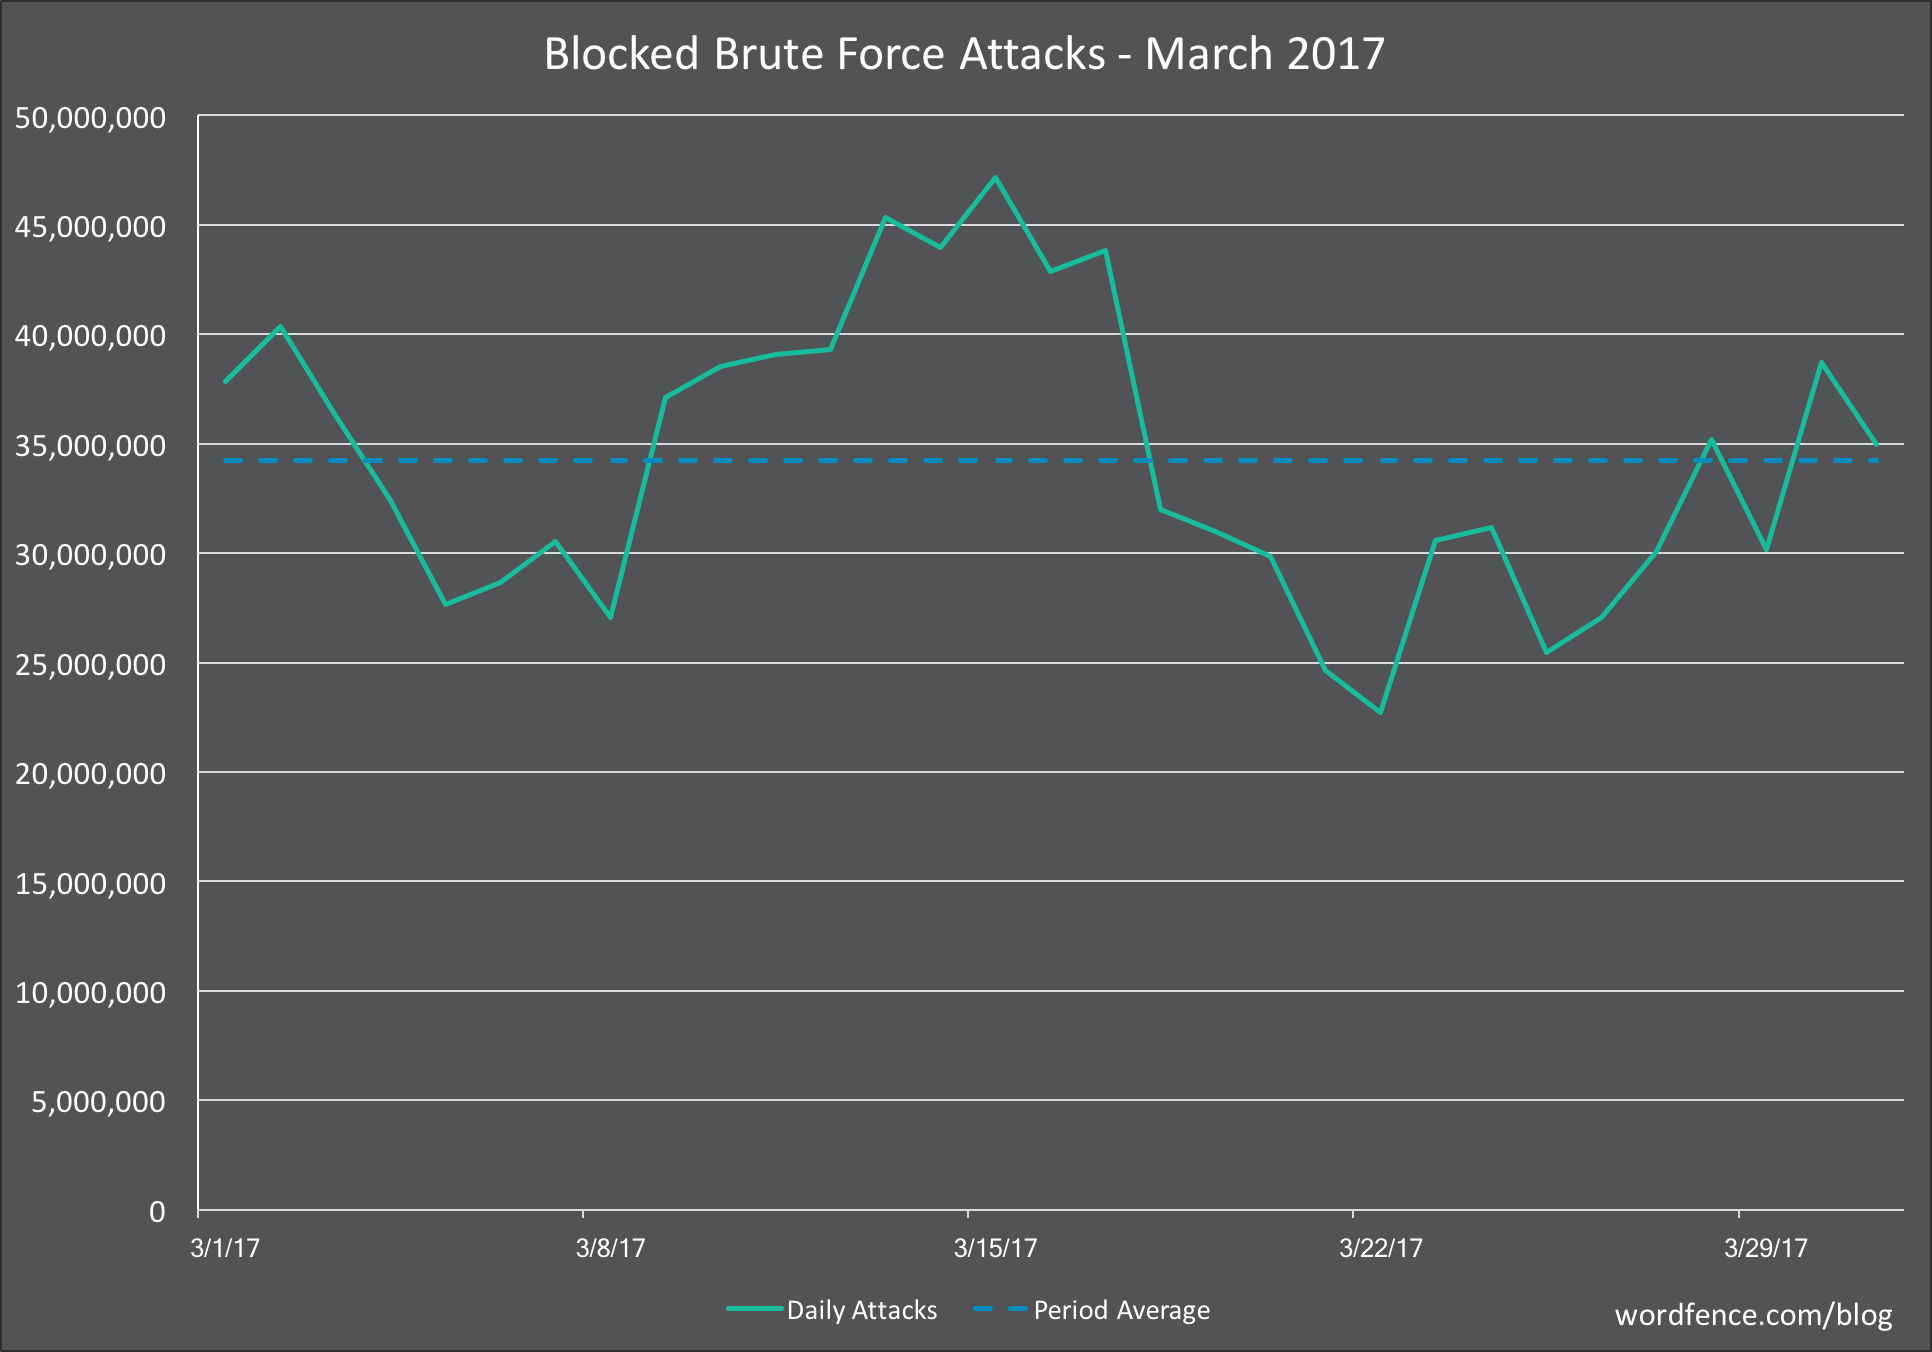
    The chart below shows the brute force attack activity on WordPress sites that we monitor for the month of March.

    We saw a slight increase in the average daily attacks from 30 million in February to 34 million in March. Not a big change, so in general the attack frequency and activity is fairly steady. In February we saw a huge sustained spike in activity towards the end of the month. We did not see that in March for brute force attacks.

    Complex Attacks on WordPress in March 2017

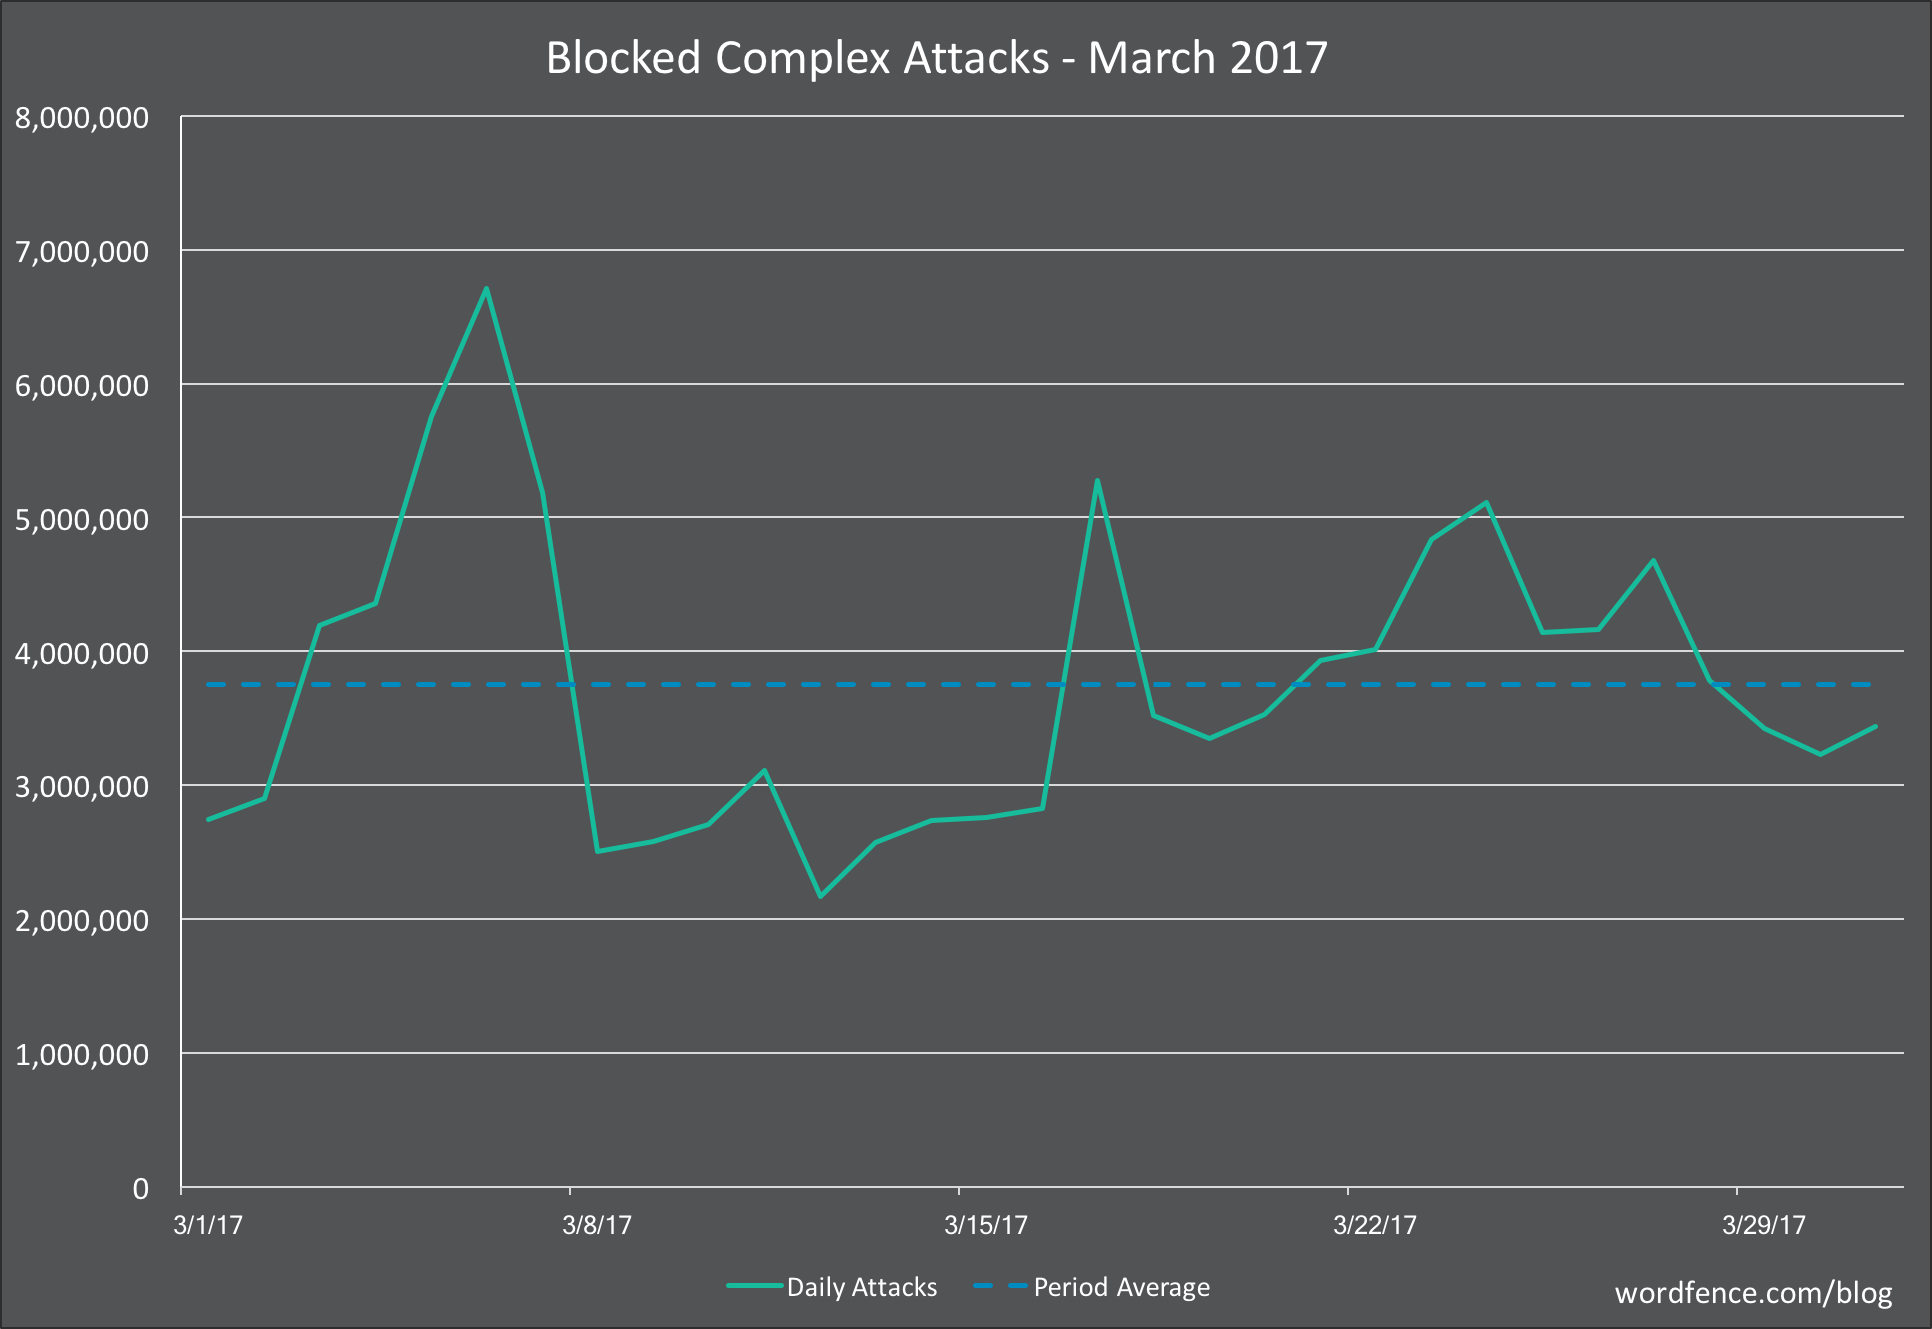
    The graph below shows complex attacks (attacks that try to exploit a vulnerability) for the month of March 2017.


    The average daily attacks increased from 3.4 million in February to 3.8 in March. In February the attack graph was fairly constant throughout the month. March saw a huge spike early in the month which quickly subsided.

    Once the spike subsided, we saw a sustained period of relative calm with only 3 million attacks per day and then a gradual pick-up later in the month.

    Attacks on Themes in March 2017

    The table below shows the total number of attacks on WordPress themes. We identify each theme using it’s ‘slug’ which is the directory in which it is installed in WordPress.

    There is some movement in the rankings, but for the most part the same themes are being targeted.

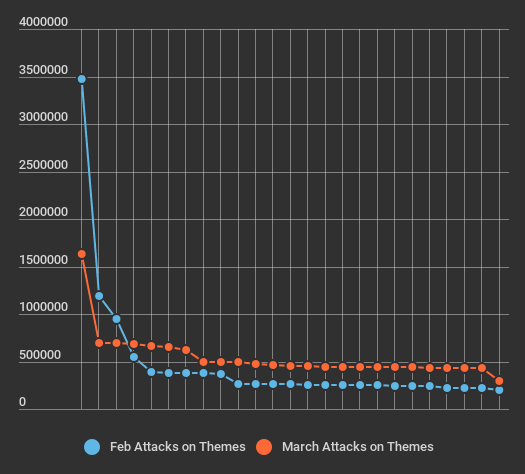
    One interesting change we noted is that for the month of March, the attacks are more spread out. Below we generate a graph showing the “long tail” of attacks on themes. We have created a distribution from left to right of the most attacked themes to the least attacked. It creates a curve which is commonly known as a “long tail” among statisticians.

    As you can see, for the month of March, the long-tail flattens out because we are seeing attacks more evenly distributed across themes, rather than focusing on a smaller number of frequently attacked themes.


    Attacks on Plugins in March 2017

    The table below shows the attacks we saw on plugins across the sites Wordfence protects. As with themes, we identify each plugin by its unique ‘slug’ which is the unique installation directory where the plugin is installed.

    The list of plugins being targeted has had some shuffling around, but as you can see, all plugins in the list are well known targets of attack that are generally in the top 50 attacked plugins for WordPress.

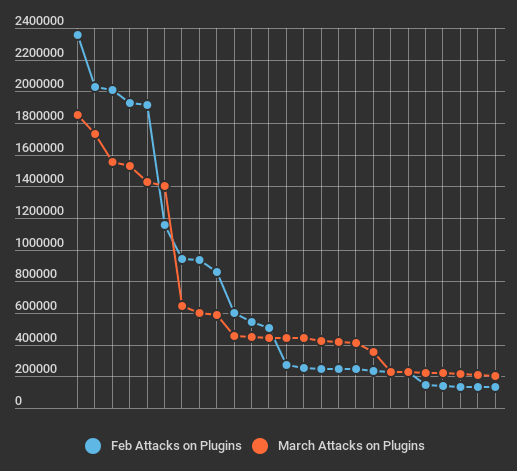
    If we look at the long-tail distribution for plugins we can see that the attack distribution has not changed much and is still roughly the same as February.


    Attacks by Country for March 2017

    The table below shows the top 25 countries that attacks originated from in the month of March on WordPress sites that we monitor. The most surprising thing in this list is the sudden appearance of Algeria as an attack source. In our previous report, Algeria was ranked way down at 60 for total attacks.

    We will be posting a follow-up post which explains why Algeria has suddenly jumped in the country rankings. We dug a little deeper and found some very interesting data that we will be including in a report which we expect to release next week.

    Conclusion

    I hope you’ve enjoyed this overview of the WordPress attack landscape. If you are in the threat intelligence field, I encourage you to grab this data and incorporate it into your own analysis. I know some of you already have and have shared your findings with us privately and I very much appreciate that.

    We will be publishing a follow-up to this report describing why Algeria has risen in the attack ranks some time next week.

    The post The March 2017 WordPress Attack Report appeared first on Wordfence.
  • WordPress Security – Unwanted Redirects via Infected JavaScript Files

    WordPress Security – Unwanted Redirects via Infected JavaScript Files

    WordPress Security – Unwanted Redirects via Infected JavaScript Files

    We’ve been watching a specific WordPress infection for several months and would like to share details about it.

    The attacks inject malicious JavaScript code into almost every .js file it can find. Previous versions of this malware injected only jquery.js files, but now we remove this code from hundreds of infected files. Due to a bug in the injector code, it also infects files whose extensions contain “.js” (such as .js.php or .json).

    Continue reading WordPress Security – Unwanted Redirects via Infected JavaScript Files at Sucuri Blog.