Online Services

Tag: WordPress Security

  • Endpoint vs Cloud Security: The Cloud WAF User Identity Problem

    Imagine you’re a security guard at the entrance to a high security facility. You need to evaluate each person who wants to gain entry to ensure they are allowed access. You use information about each person to make your decisions. You might use information like what they say, whether they’re carrying a bag, if they’re carrying a gun and so on.

    The most important item of information you’ll use in your decision-making is who they are and what access level they have. In other words, their identity. If you don’t have this identity information, you are going to have a very difficult time making a decision about whether someone should be granted access or not.

    In this post, we show you how cloud WAFs like Cloudflare and Sucuri, also known as cloud firewalls, actually don’t know who you are. They don’t even know if you’re signed in or not. The result is that they tend to do a much worse job when it comes to deciding who should be allowed to access a website and who should be blocked.

    This post is a continuation of a series of Endpoint vs Cloud blog posts, which we started on Tuesday. We have already described the Cloud WAF Bypass Problem, and how an endpoint firewall like Wordfence prevents bypass.

    Endpoint Security: Wordfence Knows Who a Visitor Is and their Access Level

    As we discussed earlier this week, ‘endpoint security’ is what all major security vendors are moving towards. The ‘endpoint’ is the target an attacker is trying to gain access to. It might be a workstation, mobile device or your web application like WordPress.

    An endpoint security solution runs directly on the endpoint and protects it in a variety of ways. Wordfence is an endpoint security solution because it executes directly on WordPress, which is the endpoint for an attacker targeting your website.

    Wordfence integrates deeply with WordPress. One of the items of data we have is who a visitor to your site actually is and what access level they have.  In security industry terms, we refer to this as authentication and authorization. We know if they’ve proven they are who they claim to be and we know what they have authorization to access.
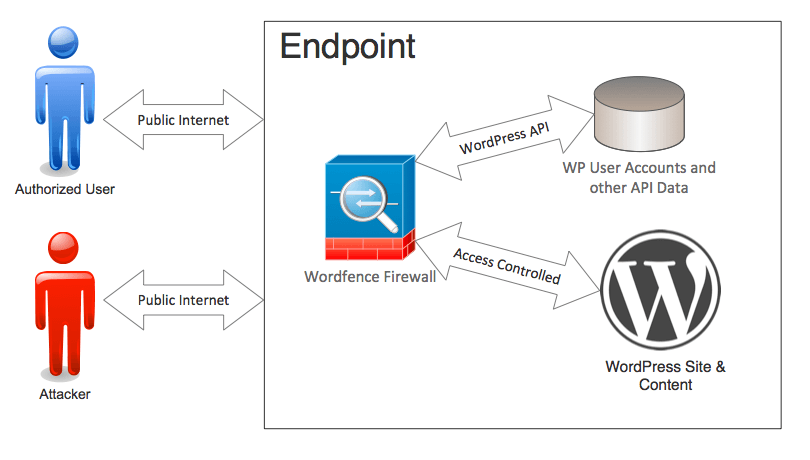
    Wordfence Protecting the Endpoint

    Identity information is a critical part of the decision-making that our firewall performs. It helps us create firewall rules that block the bad guys and make sure that administrators and other privileged users don’t accidentally get blocked.

    User identity and access level is so important to our firewalls decision-making that we use the user’s access level in more than 80% of our firewall rules. It helps us prevent the dreaded “false positive” when a real user is blocked. It also helps us create rules that block against more complex attacks.

    By having user identity and access level, we can be extremely aggressive in the kind of rules that we create. Along with user identity we use other information to make our decisions, like the path being accessed, the URL query string, the type of request being made, the body of the request and other headers that might be included in the request.

    Cloud Firewalls Don’t Have Identity Information

    A cloud firewall like Cloudflare or Sucuri’s WAF uses servers based out on the Internet, away from the endpoint they’re protecting. Visitors and attackers who come to your website first arrive at the cloud WAF. The cloud WAF runs the request through a series of rules and decides if it’s allowed or not.

    Cloud WAF providers have a firewall that runs physically and logically separated from the endpoint. They don’t interact with the endpoint API to make their firewall rule decisions. They don’t have authentication and authorization data that can use to help with that decision making.
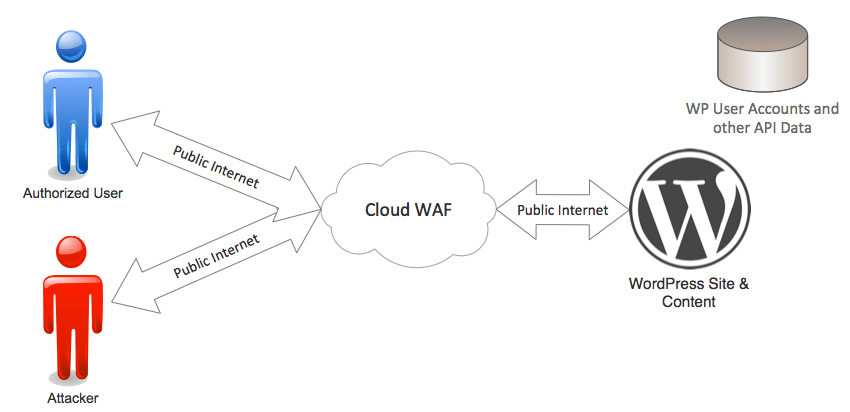
    cloud1

    A cloud WAF might be able to see if a user has a login cookie, but that cookie can be easily faked because they can’t verify its authenticity, because they don’t have access to the endpoint API, data and execution environment.

    As we have explained, it’s critically important that a firewall knows who a visitor is and what permission level they have to make effective decisions. A cloud WAF does not even know if a user is signed in or not. 

    Cloud WAFs use pattern matching. They examine the arriving web request and use patterns to try to determine if it’s an attack or not. This results in much less effective decision-making. They block a few attacks but miss many others.

    Cloud WAFs may also suffer a higher rate of false positives because they can’t identify real users making perfectly legitimate requests that trigger their rules. The only way to fix the false positives is to loosen up the rule-set, which results in more attacks getting through. It’s a Catch-22 situation.

    Endpoint Security for WordPress: Local Knowledge, Defense in Depth
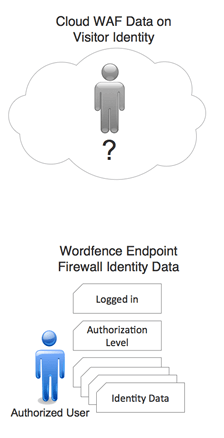
    identity2Wordfence is an endpoint security solution that executes within the WordPress environment. That means we have full access the the WordPress API and we can use any data in this API to make our decisions about who is granted access. That’s one of the reasons the industry is moving towards endpoint solutions: they have local knowledge to help their decision-making.

    To help the Wordfence Firewall make its decisions, the WordPress API provides us the following data:

    • If the user is signed in or not.
    • The user’s identity.
    • The user’s authorization level e.g. ‘subscriber’, ‘editor’ or ‘admin’.

    If we see a verified admin user trying to access something that looks like a common attack, we might allow it to pass if all other data indicates it’s safe. If we see the same request coming from a ‘subscriber’ level user or someone who is not signed in at all, we will block it.

    Protecting Against Complex Attacks

    Wordfence protects you against more complex attacks, like a “privilege escalation attack”, or privesc attack as we refer to it internally. If you look at the list of firewall rules we’ve deployed on your site, you’ll see at least three privesc attack rules that are currently active and protecting you.

    A privesc attack is where an attacker uses an account with low level access, like a ‘subscriber’ level WordPress account. Then they use the lower level privileges that account has to exploit their way to administrator level access.

    To protect against privesc attacks, you need to know if a user is signed in and what access level or level or ‘authorization’ they have. If you don’t have authorization information, you don’t know if a subscriber level user is trying to perform an admin function or if it’s a real admin taking the same action. 

    Wordfence in effect has local knowledge about the system it is protecting. To make better firewall decisions we have made sure we simply have better data.

    Conclusion

    Smart decision making requires the best data.  By protecting against attacks at the endpoint, you can make smarter decisions about who should gain access and who should be denied. With better data, you can also benefit from a far more aggressive rule-set without risking false positives, because you know who is using your web application. That is why Wordfence protects against attacks at the endpoint.

    The post Endpoint vs Cloud Security: The Cloud WAF User Identity Problem appeared first on Wordfence.
  • Endpoint vs Cloud Security: The Cloud WAF Bypass Problem

    Earlier this year at Black Hat 2016 there was a lot of buzz around “endpoint security”. In this post I’m going to explain a few issues with a cloud approach to web firewalls. Then I’ll explain the benefits of endpoint security and why Wordfence takes an endpoint approach to protecting your investment.

    The Cloud WAF Bypass Problem

    Cloud firewall providers like Sucuri and Cloudflare have servers that live out on the internet. When you configure a cloud firewall (or cloud WAF), the provider will ask you to point your website at their servers by making a DNS change. Once you’ve done that, the cloud provider configures their servers so that when your web traffic arrives there, it is filtered using their firewall rules.

    Once filtered, the traffic is forwarded over the public Internet to your website. In this configuration your original website is known as the “origin” or your “origin server”. That is where your site originates from and is actually hosted.

    Your origin server may be hosted at Bluehost, Hostgator, Godaddy, on your own server or with one of the many other hosting providers.

    In theory once you have configured your website with a cloud firewall (or cloud WAF) you are protected by it. The expectation is that attackers will try to access your website using your domain name of www.example.com, they will be pointed to the cloud WAF and their attacks will be filtered out.

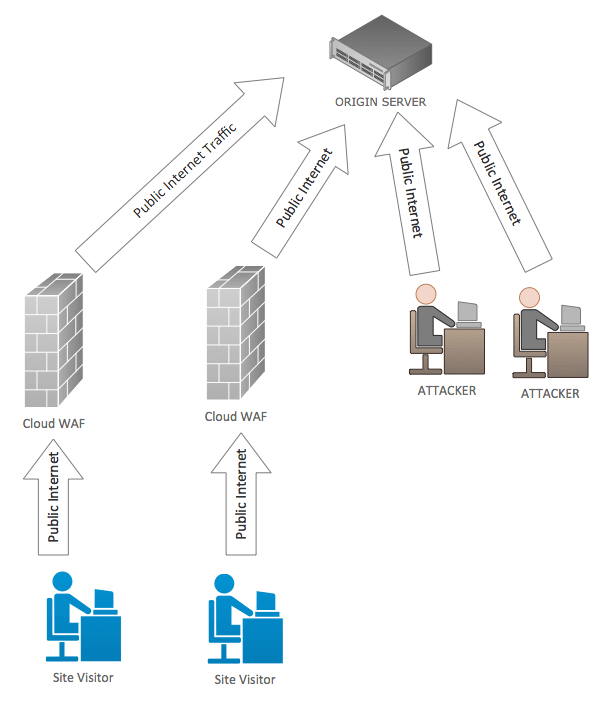
    In reality, if an attacker can discover your origin IP address, they can simply bypass the cloud WAF as the diagram below shows:

    cloud-waf-diagram

    In the case of a cloud WAF, you aren’t actually “behind” a firewall because the server is still on the public internet. Anyone on the net can access your server directly if they discover your origin server IP address. Knowing your origin server IP allows them to simply go around the cloud firewall provider and attack your origin server.

    Cloudflare have acknowledged this problem in a blog post and they provide various suggestions on how to keep your origin server IP address “secret”. They also explain how to access your origin server directly for testing if you have the IP address.

    We refer to this problem as the “Cloud WAF Bypass Problem”.

    The Cloud WAF Bypass Problem is Well Documented

    This issue is well documented by many security bloggers. Tools like CloudPiercer.org and CrimeFlare exist to help attackers bypass a Cloud WAF.

    CrimeFlare lets you look up a Cloudflare customer’s origin IP address or download an entire database of 1.5 million Cloudflare customers and what CrimeFlare detected as their origin IP address.

    CloudPiercer uses an array of techniques to reveal a targets real IP address. They estimate that 70% of sites protected by cloud WAF providers have their origin IP address exposed. More detailed stats and our own data is included below.

    Keeping the Origin IP Address Secret is Difficult

    There are many ways to discover a site’s origin IP address. You can:

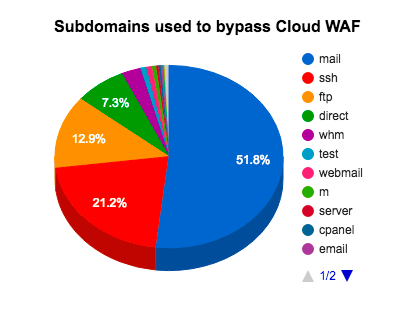
    • Look up the IP address of subdomains like mail.example.com and ssh.example.com. In many cases they point to the origin IP address. (See below for detailed statistics)
    • Use an IP history database like viewdns.info to look up where the origin IP was hosted before the website started using a cloud WAF.
    • Use the site certificate and a search engine like Censys.io or Shodan.io to locate the origin IP address where the certificate is installed.
    • Perform an action that gets the site to connect somewhere, revealing its origin IP address. For example, on WordPress you can initiate a pingback to a site which will cause it to connect back to you, revealing its origin IP address.
    • Use DNS records like SPF which might reveal the origin IP or adjacent addresses.
    • Examine site HTML source which may include subdomains that point to the origin IP address.
    • Examine public source or log files which may include the origin IP address or subdomains pointing to the origin.

    The original designers of the net never intended IP addresses to be secret. There are no standards or conventions on the net that describe how an IP address might stay secret. In fact standards like SSL certificates and de facto standards like WordPress Pingback make it virtually impossible to keep an IP address hosting a website secret.

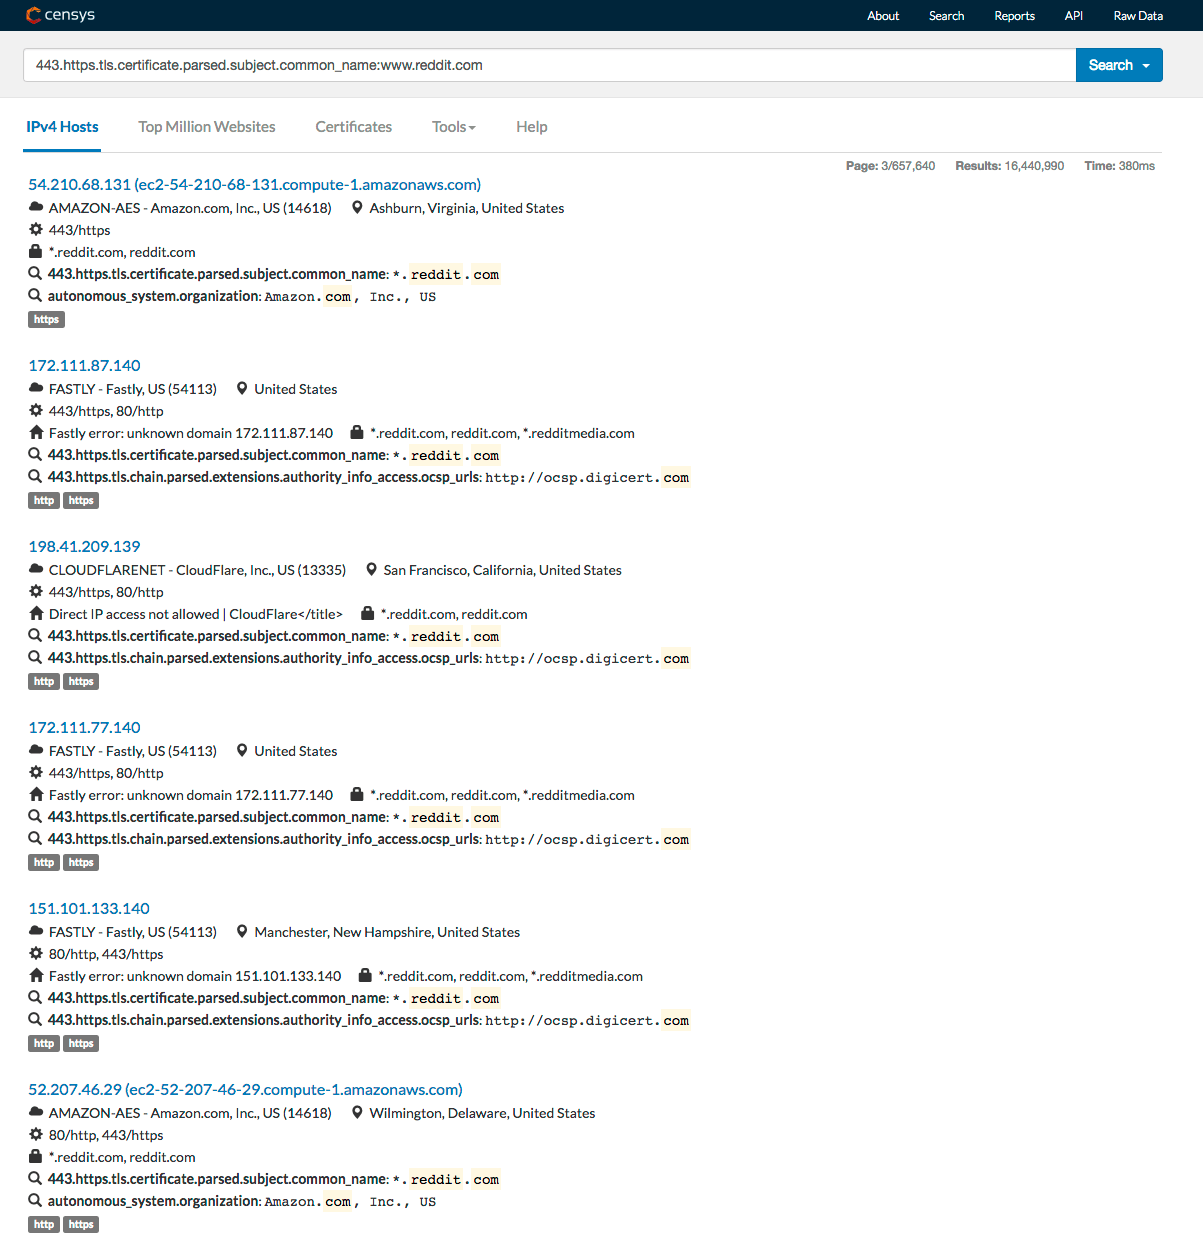
    Search engines like Censys.io and Shodan, well known in the hacker community, go around and index the internet at a network level, indexing SSL certificates and network service information. They provide a treasure trove of information to attackers who are looking for targets.

    Censys.io lets you easily search for the origin IP of any website by using that sites certificate. The results below are from a search on Censys using the certificate common name (website hostname) of Reddit.com which is behind Fastly and Cloudflare. An attacker would use the origin server addresses to launch an attack that bypasses the cloud WAF.

    screen-shot-2016-10-04-at-7-57-23-am


    34% of Cloudflare sites can be bypassed using just one of these techniques

    To determine the scale of this problem we did an automated survey of 30,753 randomly selected Cloudflare customers. We tested how many sites are accessible by simply bypassing Cloudflare and accessing the site directly. We only used one technique to discover the origin IP: Looking up a common subdomain. We didn’t use the pingback technique, site certificates or any of the several other techniques detailed above.

    We found that we could directly access 34% of Cloudflare customers, or one in every three customers, bypassing any security that Cloudflare provides, by simply looking up a common subdomain.

    To perform the audit on subdomains, we took the following steps:

    1. Verify the customer is using Cloudflare and store a copy of their website home page. We checked HTTP and HTTPS and the site with and without the www. prefix to locate it.
    2. Look up common subdomain IP addresses.
    3. Verify the subdomain IPs don’t point to Cloudflare.
    4. Remove duplicate IPs.
    5. Try to fetch the site from the origin IPs directly by connecting directly and specifying a ‘Host’ header in the HTTP request.
    6. Where we received a response, compare the original page title and first asset (first item in a src= attribute) with the page we just fetched directly.
    7. If they match, then count it as a successful bypass.

    As you can see from the chart below, looking up the IP address using the ‘mail’ subdomain is by far the most successful technique. Over 50% of cloud WAF customers that reveal their origin IP do so through the ‘mail’ subdomain. The ‘ssh’ domain is also a common culprit, likely because Cloudflare’s own documentation use it to illustrate how you can connect directly to your own origin IP address.

    screen-shot-2016-10-11-at-7-45-30-am

    The Fix: Protect the Endpoint and Prevent Bypass

    Endpoint protection has taken the industry by storm during the past year. Almost every major vendor is providing some form of endpoint security. So what is the endpoint exactly? An endpoint can be defined simply as: the final target a hacker is after. In the case of desktop security, it is the workstation a user works on. In the case of mobile platforms, it’s the smartphone a user has in their pocket.

    In the case of WordPress, the endpoint is the actual WordPress installation that the attacker is trying to compromise. We believe that to best protect a website, you need to protect the endpoint.

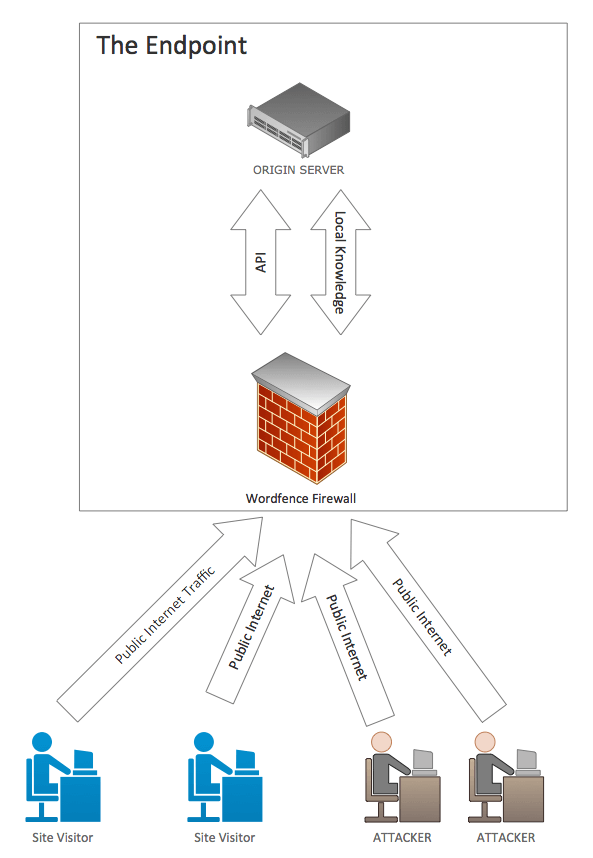
    The first benefit of protecting a website at the endpoint is there is no way for an attacker to bypass the security mechanisms. They can’t go around the Wordfence Firewall because it is an integral part of the endpoint. To use the endpoint application, you have to interact with our firewall.

    The second major benefit is that, by protecting the endpoint, we can provide a defense in depth strategy. We don’t just provide a firewall. We also include a malware scanner and a range of other features. It’s not feasible to include a malware scan unless you are executing on the endpoint itself.

    wordfence-waf-diagram

    Conclusion

    To fully protect your investment you need to employ an endpoint strategy that takes a defense in depth approach to security. Wordfence takes this approach.

    As our company has evolved we have had to consider whether we would invest in “cloud” security or focus on protecting our customers where their assets are. We chose to stay on the endpoint and the industry has now also shifted their focus to protecting the endpoint.

    In our opinion, using a cloud WAF is like hiring a security firm in Los Angeles and asking all of your visitors to go through their Los Angeles offices before visiting you in New York. We believe in posting guards where the assets are and putting additional defenses behind that first layer of security. This proven approach works for the over 1.5 million sites we protect and it is where the industry is headed.

    The post Endpoint vs Cloud Security: The Cloud WAF Bypass Problem appeared first on Wordfence.
  • WordPress Hack Modifies Core Files to Share Spam

    WordPress Hack Modifies Core Files to Share Spam

    One of the worst feelings a website owner can experience is discovering that your site has been hacked. Without proper security measures in place, even website owners with the best intentions can lose control of their website. When hackers gain access to your site, they can use it to host phishing content, distribute malware, steal…

    The post WordPress Hack Modifies Core Files to Share Spam appeared first on Sucuri Blog.

  • 18X Speedup in Wordfence Scan

    Wordfence 6.2.0 was released yesterday and it includes something really special: a huge improvement in scan performance. I’m going to share with you what changed and why Wordfence 6.2.0 is the same great quality malware and security scan running up to 18X faster.

    Malware scanning is a critical part of the layered approach to protection that Wordfence provides. The Wordfence Firewall stops attacks in their tracks. Scanning is how we determine if a hacker has gained access to your site. You’ll recall that we’ve also integrated the malware scan into the Wordfence Firewall to scan file uploads as they arrive. This gives you three layers of protection against attacks.

    Our Firewall has always been extremely fast and the malware scan built into the firewall uses the same model of execution. While we are always looking for ways to optimize our firewall code, we really don’t need to improve in that area because it’s so darn fast already.

    However, we had received reports from a few users that scanning would take quite a long time on larger sites. We have also had reports from a few hosting providers that when a large number of scans are running concurrently (200 or more), they could use a lot of disk IO resources.

    So we decided to tackle this issue head-on and work closely with our customers and hosting providers.

    Working to make scan faster

    I met with one large host in person and had a very informative and collaborative discussion (Thanks Heidi!!) that included follow-up conversations with our team and a direct channel of communication with our devs and QA team. Then we put our heads down and got to work.

    Ryan Britton, one of our senior developers at Wordfence led the technical effort and Matt Rusnak led the QA effort on this project. They went away and worked on this and when they came back with the numbers, I couldn’t believe the results.

    scanperformance3

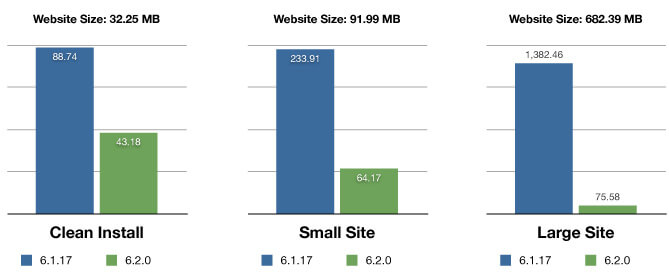
    To measure performance, we isolated the process running Wordfence and monitored disk reads. The above bar charts show the amount of data read in megabytes for the older version of Wordfence compared to 6.2.0 which is in green. Less is better because it reduces the amount of IO load on the physical server hosting the site running Wordfence.

    • For Wordfence 6.2.0 we halved the IO load on sites running a brand new plain WordPress installation.
    • On a small site of around 92MB we achieved a 3.6X reduction in disk IO load.
    • On a larger site with 682MB we are seeing an impressive 18.4X reduction in disk IO load.

    Larger sites will see an even greater increase in speed and reduction in IO load during scans. We don’t know what the average size of a WordPress site is, but we estimate that it’s similar to the large site model we used. My personal blog, for example, is 552MB of files and it’s been around for a reasonable amount of time.

    Scan functionality and detection capability stays exactly the same.

    We haven’t reduced the number of signatures we’re using for detection or the number of files we read. There was a bugfix included in this release where we no longer scan .txt files unless you have ‘High Sensitivity’ scanning enabled, but that is unrelated to performance improvements.

    How we made these huge performance gains

    We achieved this huge speed increase by changing the way we’re performing MD5 and SHA256 hashes of files, getting smarter about not hashing files where we aren’t using the hash and reducing the hashing operation to a single streaming read on each file.

    We also removed counters that were not needed that were increasing file reads. In addition, this new release keeps better track of which directories have been scanned so that we don’t need to reiterate through a large list of directories when the scan resumes.

    It’s worth noting that image-heavy sites will see a particularly large improvement in scan speed.

    …And then we went even further!

    One of the amazing things about the Wordfence team is that they are super passionate about what they do. For 6.2.0 I was expecting to get a modest increase in scan speed. Instead we got a huge gain in scan speed. Then the customer service team got involved and encouraged Dev and QA to go even further.

    What they came up with is what we’re calling a “Low resource scan”. When this option is enabled, Wordfence does exactly the same amount of work, but it introduces an artificial delay in the scan which consumes no additional resources but spreads the disk IO load out over time. This reduces peak usage load on servers that have slow disk or that are hosting a lot of other busy websites.

    You can enable the “Low resource scan” by going to the Wordfence options page on your WordPress site, scroll down to the “Scans to Include” heading and then at the bottom of that section you can find the option labeled “Use low resource scanning. Reduces server load by lengthening the scan duration.”. You can find the documentation for that option here.

    As you can tell from above, we have massively reduced the amount of disk IO that Wordfence generates, but just in case that’s not enough and your hosting provider asks you to reduce things further, you can now enable this option.

    In our tests, the low resource scan takes 1.7 to 3.7 times longer to run, depending on your site, while reducing peak load. Again, it does the same amount of work, just spread over more time.

    The low resource scan combined with our much faster scan engine gives you a very low impact way to regularly scan for malware while keeping your hosting provider happy and your site super fast. We recommend most people leave this setting off, but in extreme cases of limited resources, customers can now enable this setting.

    We recommend the following configuration:

    You will find the best performance gains when Wordfence is using the default scan configuration. For our own sites we leave low-resource scanning off and just use the default Wordfence options. The scan is now incredibly fast.

    On my own blog with 6127 files totaling 552MB of space, my scan now finishes in 24 seconds from a cold start to finish. I run my personal site on the cheapest $10/month Linode server available. That is incredibly fast on a very modest server.

    We think the standard configuration will work great for the vast majority of sites out there.

    In Conclusion

    As always a huge thanks from me to our incredible team for this collaborative effort. And a very special thanks to the customers and hosting providers who worked with us to help us better understand their needs.

    Wordfence remains committed to securing the WordPress community and platform. To that end we work closely with our customers and hosting providers to ensure that we continue to provide the best protection available for WordPress. This is another major leap forward in achieving our goal of a secure WordPress community and a more secure Web.

    As always we welcome your feedback in the comments below, or you can contact us using one of the channels on our contact page.

    The post 18X Speedup in Wordfence Scan appeared first on Wordfence.