Online Services

Tag: WordPress Security

  • We will always put our customers and community first

    We will always put our customers and community first

    On Tuesday we published a blog post about the 404 to 301 plugin inserting ad links into page content that only search engines could see. This is a technique called cloaking and will incur a penalty from Google.

    Since then we have received some criticism from the maintainers of the WordPress plugin repository for the way we handled this. We have also received some criticism from the community for victimizing a plugin author.

    I’d like to share a few additional facts and then explain why I wholeheartedly stand by our decision to publish and the way we handled this.

    • The plugin inserted links to websites into page content that would only show up when Google or another search engine crawled the site.
    • The content was hidden to the site owner or anyone who did not visit the site with a search engine user-agent (browser identification string).
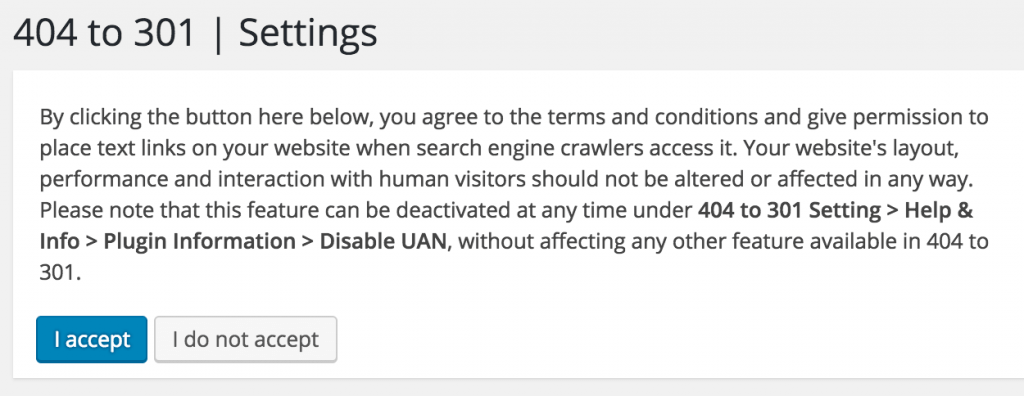
    • The plugin asked you for permission to do this by displaying terms of service that described exactly what it was intending to do. The ‘cloaking’ portion of the terms of service was at the end after a long copy of the GNU general public license that was included. It was below the fold in a scrolling element, so would not have been noticed by anyone who didn’t scroll down. (See below for screenshot)
    • On further investigation the ad domain, which is wpcdn.io, serves up three things:
      • The Payday Loan content we already disclosed. (See below for content)
      • A link to an adult UK based escort service. (See below for censored screenshot and content).
      • A string of text that is somewhat unique: sdf98jhk (See below for content)
    • If you google the string of text it returns 8,620 results and these appear to be WordPress sites that have had content injected by this plugin and that content has been indexed by Google. Random checks confirm that these sites are running the affected plugin. This confirms over 8,000 sites at a minimum were affected.
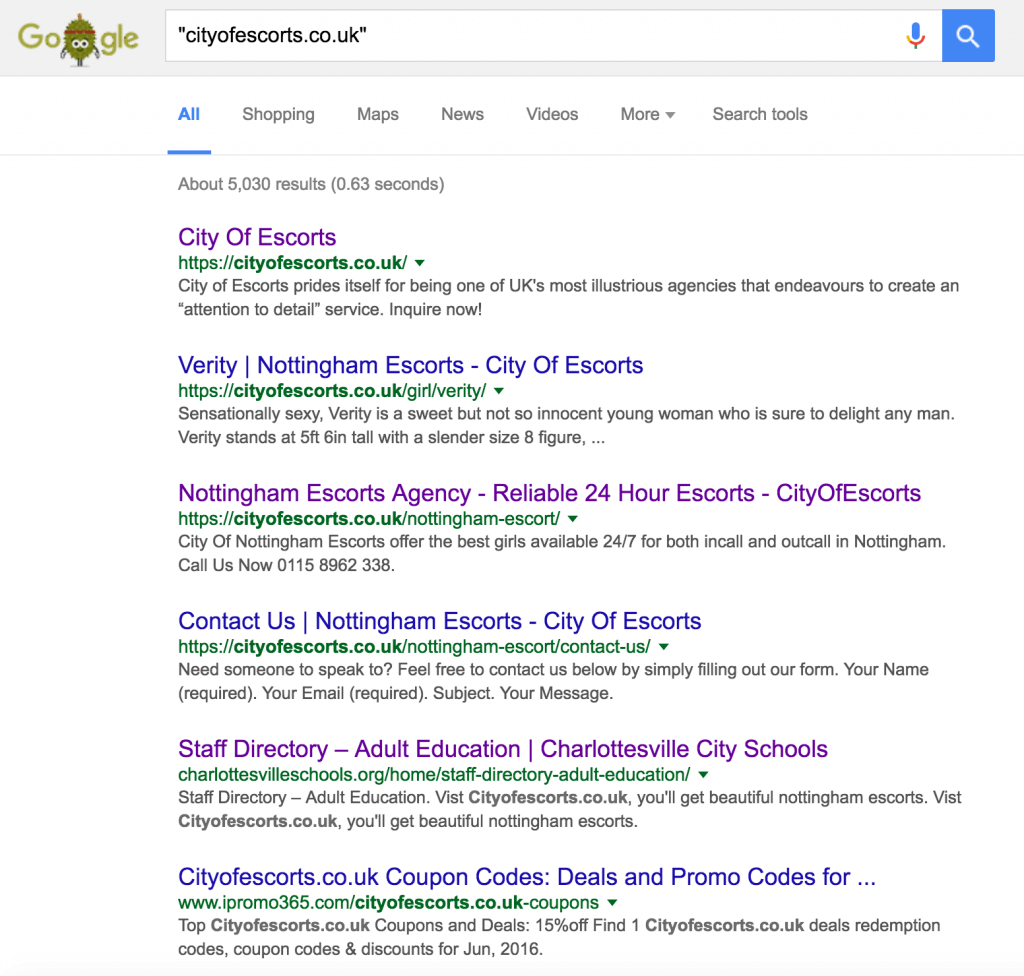
    • Sadly if you google the adult domain that is being served, it appears to have infected many other websites including a school’s site that is now serving adult content to Google. (See below for screenshot)
    • The ad domain was registered on January 14, 2016.
    • The plugin author’s account was used to upload the changes.
    • We were alerted to this plugin by a customer and upon investigation found that their site was surreptitiously serving up blackhat SEO content.

    This was not a vulnerability

    This is not a security hole in a plugin that requires the usual ‘responsible disclosure’ to the plugin author. This was a plugin that had malware pre-installed by the author’s account and was active on over 70,000 websites.

    It was urgent that we notify the community and our customers about this so that they could immediately react and limit the damage.

    The fact that the terms of service in the plugin actually ask for permission to engage in cloaking (see below for screenshot) indicated to us that this was done with the plugin author’s blessing, rather than being a case where a plugin author’s account was hacked. The exact wording from the ToS was:

    “By clicking the button here below, you agree to the terms and conditions and give permission to place text links on your website when search engine crawlers access it.”

    We were under absolutely no obligation to look after the plugin author’s interests when we discovered this because it wasn’t a security hole that was accidentally written by the author. Someone had intentionally placed spam on a large chunk of the WordPress community’s websites and was profiting from it. The terms of service indicated it was intentional.

    We needed to react quickly and that’s what we did.

    How we handled this incident

    On Tuesday this week Wordfence immediately notified our large security mailing list about the problem by posting on our blog and sending out an email linking to the post.

    We also notified the plugins@wordpress.org email address about the issue.

    We made no attempt to notify the author. Presumably he already knew he was doing bad things based on his terms of service.

    What happened once we sent out the notification

    We were criticized for our approach by the WordPress.org plugin repository maintainers. We were told we should have contacted the developer first. Then if they don’t reply or we can’t find out how to contact them, we should contact plugins@wordpress.org second. And only then should we post, preferably after something has been fixed.

    I strongly disagree with this approach and stand by our actions because this was a plugin that had malware intentionally pre-installed by the author. Why notify the author that they’ve been discovered?

    It seems more helpful to put the community in the driver’s seat. Let them take immediate action to limit damage that has already been intentionally done to their websites and their Google reputation. And then worry about the plugin author’s interests.

    And so that’s exactly what we did. We sent out an immediate notification to the community and included plugins@wordpress.org in that notification.

    What has the plugin author done?

    The plugin author now says that he has removed the malicious code as per his changelog. We have not independently verified this.

    The author has posted a blog post which you can find here:

    https://thefoxe.com/blog/404-to-301-plugin-detected-by-wordfence-here-is-what-actually-happened/

    We are intentionally not linking to the post to avoid promoting his website.

    The post starts by saying “There are people, making money from other’s mistakes, instead of correcting them.”.

    We’d like to point out the author was making money by surreptitiously injecting spam links into website content and as a side effect, destroying those website’s search engine rankings. How are we obligated to correct his greed and lack of morals?

    He was “shocked” that he received negative reviews of his plugin. We’d like to point out that there may be justification for those reviews.

    The author says “I found that the links and ads are being shown at the top of the page content instead of showing small credit text at very bottom, for crawlers.”. This suggests he knew he was cloaking, was doing it intentionally and thinks the problem is that the ads appeared to regular browsers too (in addition to search engines). We’d like to suggest he read up on what cloaking is and why it’s bad.

    He blames another developer who isn’t named, conflates security vulnerability with intentional malware, paints himself as the victim, accuses us of censoring his comments on our blog (we didn’t) and claims we profited by demonizing him.

    Final thoughts

    I created Wordfence because my own personal site was hacked by the Timthumb vulnerability back in 2012. I discovered the vulnerability which was a zero day, I wrote code that patched timthumb and then went on to lock myself in a room and code for 8 months straight to create Wordfence to help prevent this from happening to anyone else ever again.

    Today, Wordfence is a team of more than 20 highly trained and qualified individuals that come from a wide range of sectors in the security profession and community. We provide a world-class firewall that is free for the community and open source. We invest heavily in providing additional free resources to help the community like our free WordPress security Learning Center and like the prolific free support we provide on the wordpress.org forums.

    I know what it feels like to have someone intentionally install their own malicious code on your site and profit from that code. It hurts your livelihood and reputation and it was such an awful experience I’ve dedicated my career for the last 5 years to making sure that does not happen to anyone else.

    That is what happened in this case.

    In this case we were under no obligation to protect the plugin author’s interests. We notified the community first and we did it loudly. My team and I stand by our actions and we will do it again if we discover anyone else intentionally installing malware on community or customer websites.

    We will always put our customers and the community first.

    I welcome your comments but I’d like to ask you for a favor: Please avoid any witch-hunting or personal attacks on any individuals involved in this, including the plugin author and anyone else associated with the plugin or this incident.

    Yours Sincerely,

    Mark Maunder – Wordfence founder/ceo.

    References:

    The link to a UK based adult escort service that was being injected under certain conditions:

    Censored screen capture of the home page of cityofescorts, an adult site injected into content by this plugin:
    The payday loans content that was being injected under certain conditions. This affected our customer in the initial report and is how we discovered the issue:

    Payday loans content

    The text “sdf98jhk” that was being injected under certain conditions and that allows you to find affected sites using a google search.

    sdf1

    The section (once you scroll down) in the terms of service of the plugin that describe that the plugin will be cloaking content on your site.
     

    Google results for the adult website that was being injected by this plugin. It looks like a schools website is now serving adult content to google and we haven’t been able to confirm if this plugin is the culprit or it’s other malicious code.
    The post We will always put our customers and community first appeared first on Wordfence.

  • Top 50 Most Attacked WordPress Plugins This Week

    Top 50 Most Attacked WordPress Plugins This Week

    Last week we shared the top 20 most attacked WordPress themes and an explanation of why many of them are targeted. This week we’ve dug deep into the data and we are publishing the top 50 most attacked WordPress plugins during the past 7 days.

    The data we’re sharing today is based on the following high level metrics:

    • During the past week Wordfence blocked 20,644,496 unique attacks across all the sites we protect.
    • We saw attacks from 73,629 unique IP addresses during the period.
    • 20,622,975 attacks came from IPv4 addresses and 15,160 of those attacks were IPv6 addresses.
    • Of the approximately 1.5 million active websites that we protect, 581,689 of those sites received attacks during the past week.

    The following is a list of plugins that received the most attacks during the past week – counted as the most recent 7 days starting on Tuesday evening August 16th and looking back 7 days. Once again we are showing the plugin ‘slug’ which is the unique directory name that the plugin uses when it installs into WordPress.

    This week we are ordering things slightly differently. We have the plugins ordered by number of unique sites that received attacks, labeled as “Sites attacked”. We feel this is a more useful order because it shows how widespread an attack is on a particular plugin, rather than just raw volume of attacks.

    “Total Attacks” indicates the total number of attacks that we logged on that plugin. “IPs” is the total number of unique IP addresses that an attack targeting the plugin originated from.

    “Type” is the type of attack – in most cases it’s a “Local File Inclusion” attack which allows an attacker to download any file they want to on the target system. The vast majority of files that are targeted are either the wp-config.php file which contains the database username, password and server name or /etc/passwd which contains the host operating system usernames.

    Where we’ve labeled the Type as “Shell” it indicates an attack that allows an attacker to upload a shell to the target site which gives them full remote access. These are the most serious vulnerabilities and attacks.

    All attacks are on vulnerabilities that are already publicly known. If you run any of these WordPress plugins, make sure that:

    1. You are using the newest version of the plugin.
    2. That version does not have any known vulnerabilities.
    3. You are running Wordfence with the Firewall enabled because we protect against all vulnerabilities shown.

    The list of the top 50 most attacked plugins during the past week follows:

    Plugin Sites attacked Total attacks IPs Type
    recent-backups 182,525 351,014 3,467 LFI
    wp-symposium 149,860 242,715 3,460 Shell
    google-mp3-audio-player 138,282 307,743 2,032 LFI
    db-backup 129,519 287,043 2,189 LFI
    wptf-image-gallery 107,000 131,938 2,846 LFI
    wp-ecommerce-shop-styling 103,471 131,011 2,887 LFI
    candidate-application-form 103,017 127,359 2,820 LFI
    wp-miniaudioplayer 91,546 196,557 1,381 LFI
    ebook-download 88,461 189,640 1,408 LFI
    ajax-store-locator-wordpress_0 86,051 119,192 1,396 LFI
    hb-audio-gallery-lite 82,041 105,618 1,505 LFI
    simple-ads-manager 70,683 166,131 6,476 Shell
    revslider 53,549 145,626 407 Shell
    inboundio-marketing 53,063 112,696 874 Shell
    wpshop 51,609 111,546 830 Shell
    dzs-zoomsounds 51,089 225,032 731 Shell
    reflex-gallery 49,853 111,624 699 Shell
    wp-mobile-detector 38,764 115,235 800 Shell
    formcraft 25,192 52,604 668 Shell
    sexy-contact-form 19,076 50,649 316 Shell
    filedownload 12,584 19,400 353 LFI
    plugin-newsletter 11,982 23,887 451 LFI
    simple-download-button-shortcode 11,558 21,502 427 LFI
    pica-photo-gallery 11,059 16,587 262 LFI
    tinymce-thumbnail-gallery 10,972 16,429 263 LFI
    dukapress 10,814 16,235 333 LFI
    wp-filemanager 10,756 16,634 331 LFI
    history-collection 10,427 24,371 607 LFI
    s3bubble-amazon-s3-html-5-video-with-adverts 10,312 24,011 595 LFI
    simple-image-manipulator 7,268 8,272 448 LFI
    ibs-mappro 5,555 18,738 448 LFI
    image-export 5,442 6,047 266 LFI
    abtest 5,431 5,885 297 LFI
    wp-swimteam 5,119 5,433 238 LFI
    contus-video-gallery 4,921 17,866 345 LFI
    sell-downloads 4,393 4,746 240 LFI
    brandfolder 4,268 4,619 230 LFI
    thecartpress 4,164 4,534 274 LFI
    advanced-uploader 4,066 4,351 203 LFI
    aviary-image-editor-add-on-for-gravity-forms 3,548 5,749 247 Shell
    wp-post-frontend 1,811 16,690 294 Shell
    [redacted]* 1,716 2,133 65 Shell
    mdc-youtube-downloader 1,039 5,517 199 LFI
    document_manager 915 4,450 148 LFI
    paypal-currency-converter-basic-for-woocommerce 797 1,133 129 LFI
    justified-image-grid 788 17,852 35 LFI
    cherry-plugin 539 3,919 31 Shell
    aspose-cloud-ebook-generator 531 720 25 LFI
    gwolle-gb 331 406 46 LFI

    *The redacted plugin in the list was removed before publication. It is an undocumented older shell upload vulnerability which is being targeted. The vulnerability does not exist in the current version of the plugin. Because it’s undocumented it is technically a zero day vulnerability, even though the vulnerability has been fixed in newer versions of the plugin, so we decided to remove the plugin name.

    Notes

    The large number of local file inclusion vulnerabilities that are being exploited is surprising. I should also note that many of these LFI’s were discovered by Larry Cashdollar who I had the pleasure of seeing speak at Defcon in Las Vegas 2 weeks ago. So I suspect that many of these are being used in an attack script of some kind which may explain their prevalence in the attacks we’re seeing.

    Backlit keyboardThe clustering of LFI’s together and Shell exploits together in the list order is odd, but I don’t have a theory to explain that and there is no error in the data that accounts for that. It appears to be coincidence.

    The vulnerability in the Recent Backups plugin at the top of the list was disclosed in August 2015 and the plugin has now been removed from the repository, probably because it was not being maintained. The large number of exploits targeting this plugin are puzzling because as far as I can tell from archive.org, the plugin only had a few thousand installs. It may be because it is quite easy to “google dork” to find sites that are vulnerable and the abundance of target sites may make this an attractive target.

    As a final note, I’d like to add that this data is simply an indication of the volume of attacks that we are seeing on plugins in the wild across the large attack surface that is WordPress websites who are protected by Wordfence. It does not give any indication of whether a plugin in this list is more or less secure than others. It does not include data on how successful attacks on the plugins shown may or may not be. It is purely an indication of attack activity in the wild on WordPress plugins during the past week.

    Your comments are welcomed as always.

    The post Top 50 Most Attacked WordPress Plugins This Week appeared first on Wordfence.

  • SQL Injection Vulnerability in Ninja Forms

    SQL Injection Vulnerability in Ninja Forms

    As part of our regular research audits for our Sucuri Firewall, we discovered an SQL Injection vulnerability affecting the Ninja Forms plugin for WordPress, currently installed on 600,000+ websites. Vulnerability Disclosure Timeline: August 11th 9:35 am, 2016 – Initial report to the Ninja Forms team August 11th 2:49 pm, 2016 – Public release of version…

    The post SQL Injection Vulnerability in Ninja Forms appeared first on Sucuri Blog.

  • 404 to 301 Plugin Considered Harmful

    404 to 301 Plugin Considered Harmful

    Yesterday we received a site cleaning request where one of our customers was seeing spammy links, Payday Loans in this case, injected into their WordPress website page content. The links were only appearing when the site was visited by a search engine crawler. This is common when a site has been hacked.

    An extract from the customer communication with personal info removed:

    We look after a clients website [website removed] and believe that has been compromised.

    Specifically, the issue is that when google or bing’s search bots crawl the site, they see some text injected into the top of the homepage. I have been using a user agent switcher to verify it’s presence but it was first spotted when we did a pagespeed test here: [removed] and it showed in their ‘preview’ screengrab on the desktop view.

    This text seems isn’t always present and when it is there it’s only on the home url (not actually the page eg. if you visit [page removed] it doesn’t appear).

    [snip]

    For reference, the block of injected text appears under the site header (navigation etc.) and also in the body of our exit-intent popup:

    Make Ends Meet With Payday Loans

    It is often very easy to face any financial emergency if you have adequate money to pay for them. But, this can seem all too impossible if you often live from one paycheck to another. How will you be able to pay for your urgent financial emergencies? Most often than not, you can’t. Face the reality, when your job is unable to pay for your financial emergencies, it is best to turn to payday loan providers out there.

    [rest of content removed including link to payday loans site]

    Screen Shot 2016-08-16 at 10.59.59 AMIt turns out that this is not a hacked site. It is content that is injected by a plugin called 404 to 301 plugin which has 70,000 active installs and has a 4.5 star review from 56 reviewers. When you install the plugin it asks you to agree to a long agreement which includes parts of the GNU general public license. But at the end it also includes the following text (you have to scroll down to find it):


    Third Party Text Links

    Third party text networks supply text for display in 404 to 301. These networks may collect your visitors’ IP addresses, in native or hashed forms, for purposes of controlling the distribution of text links. 404 to 301 collects anonymous aggregated usage statistics.

    By clicking the button here below, you agree to the terms and conditions and give permission to place text links on your website when search engine crawlers access it. Your website’s layout, performance and interaction with human visitors should not be altered or affected in any way. Please note that this feature can be deactivated at any time under 404 to 301 Setting > Help & Info > Plugin Information > Disable UAN, without affecting any other feature available in 404 to 301.

    404 to 301 – Copyright © 2016.

    I’m reasonably sure that no sane webmaster would agree to:

    1. Cloaking, which is specifically banned by Google and will result in a search engine penalty.
    2. Allowing ads to be inserted into their site over which they have no editorial control, including PayDay loan ads.

    We are contacting the WordPress plugin repository maintainers who will likely remove the plugin by the time you read this post. Now that you’re fully informed, we suggest you make up your own mind about whether or not you want to keep this plugin installed if you have it on your site.

    As always we welcome your comments. Please note: We have disabled comments on this post due to the inflammatory nature of some of the comments we’re receiving.

    All company, product and service names used in this website are for identification purposes only. Use of these names, logos, and brands does not imply endorsement.

    The post 404 to 301 Plugin Considered Harmful appeared first on Wordfence.